
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Patch the VMware Client Integration Plugin asap

VMware issued a security update to fix a critical vulnerability in the VMware Client Integration Plugin, apply it as soon as possible. VMware issued a Security Advisory related to a critical security vulnerability (CVE-2016-2076) in the VMware Client Integration Plugin urging administrators to urgently apply the needed patch. The flaw could be exploited by attackers to […]

Patch the VMware Client Integration Plugin asap

VMware issued a security update to fix a critical vulnerability in the VMware Client Integration Plugin, apply it as soon as possible.

VMware issued a Security Advisory related to a critical security vulnerability (CVE-2016-2076) in the VMware Client Integration Plugin urging administrators to urgently apply the needed patch.

The flaw could be exploited by attackers to launch a Man in the Middle attack or Web session hijacking under certain conditions. The problem resides in the way the VMware Client Integration Plugin handles session content.

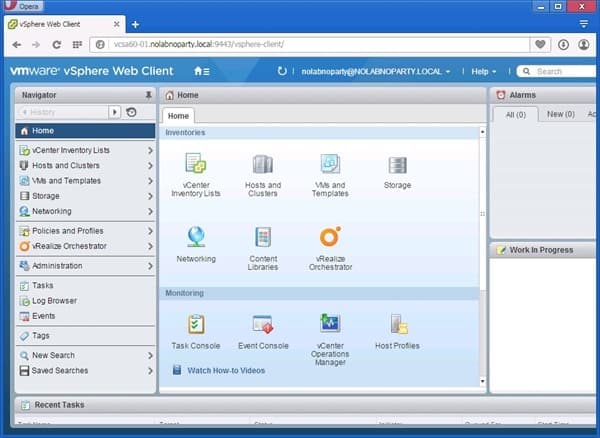
“The VMware Client Integration Plugin does not handle session content in a safe way. This may allow for a Man in the Middle attack or Web session hijacking in case the user of the vSphere Web Client visits a malicious Web site.” states the VMware advisory.

VMware Client Integration Plugin

The vulnerability affects the following versions of the VMware Client Integration Plugin shipped with:

  • vCenter Server 6.0 (any 6.0 version up to 6.0 U2)
  • vCenter Server 5.5 U3a, U3b, U3c
  • vCloud Director 5.5.5
  • vRealize Automation Identity Appliance 6.2.4

The experts at VMware highlighted that in order to solve the issue, both the server side (i.e. vCenter Server, vCloud Director, and vRealize Automation Identity Appliance)
and the client side (i.e. CIP of the vSphere Web Client) need to be updated.

Below the procedure to install the security updates:

  1. A) Install an updated version of: 
    – vCenter Server 
    – vCloud Director 
           – vRealize Automation Identity Appliance
  2. B) After step A), update the Client Integration Plugin on the system 
    from which the vSphere Web Client is used. 
           Updating the plugin on vSphere and vRA Identity Appliance is 
           explained in VMware Knowledge Base article 2145066. 
           Updating the plugin on vCloud Director is initiated by a prompt 
           when connecting the vSphere Web Client to the updated version of 
           vCloud Director.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – VMware, Virtualization)


