
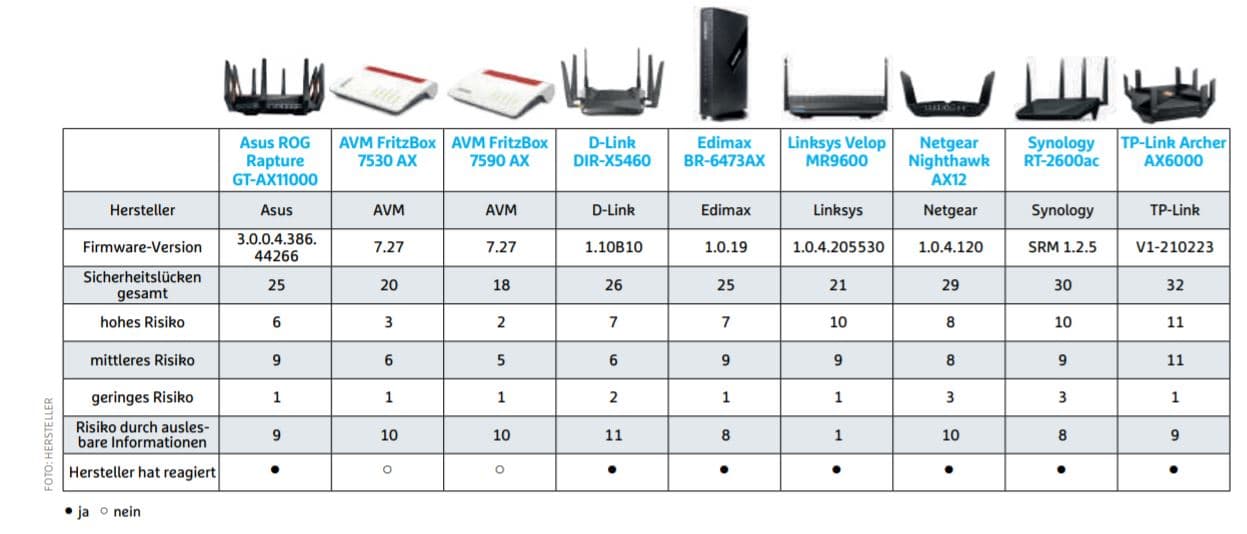
Researchers discovered a total of 226 potential security vulnerabilities in nine Wi-Fi popular routers from known manufacturers.
Security researchers and editors with the German IT magazine CHIP have discovered 226 potential security defects in nine Wi-Fi routers from known manufacturers (Asus, AVM, D-Link, Netgear, Edimax, TP-Link, Synology, and Linksys).
Millions of users are potentially impacted by these vulnerabilities.
The router affected by most of the flaws found by the researchers is the TP-Link Archer AX6000, experts discovered a total of 32 vulnerabilities, followed by Synology RT-2600ac with 30 issues and by Netgear Nighthawk AX12 with 29 bugs.

Experts also found tens of vulnerabilities in Netgear Nighthawk AX12, Asus ROG Rapture GT-AX11000, Edimax BR-6473AX, Linksys Velop MR9600, AVM FritzBox 7530 AX, and AVM FritzBox 7590 AX.
The researchers analyzed the network devices using IoT Inspector’s security platform, which checked for thousands of CVEs and security flaws.
The most common issues discovered by the experts were outdated Linux kernel in the firmware, outdated multimedia and VPN functions, presence of hardcoded credentials, the use of insecure communication protocols and weak default passwords.
“Some of the security issues were detected more than once. Very frequently, an outdated operating system, i.e. Linux kernel, is in use. Since the integration of a new kernel into the firmware is costly, no manufacturer was up to date here. The device software used is also commonly found to be outdated, as it all too often relies on standard tools like BusyBox.” reads the advisory published by the experts. “Additional services that the devices offer besides routing – such as multimedia functions or VPN – tend to be outdated as well. In fact, a large number of manufacturers use default passwords like “admin”, which in many cases can be read in plain text.”
Researchers pointed out that not all the issues they have identified are exploitable, they also found false positives.
The experts shared their findings with the manufacturers, most of the flaws have been already fixed.
“The test negatively exceeded all expectations for secure small business and home routers. Not all vulnerabilities are equally critical – but at the time of the test, all devices showed significant security vulnerabilities that could make a hacker’s life much easier,” says Florian Lukavsky, CTO of IoT Inspector.
Experts recommend users change factory settings, ensure devices have automatic updates, and disable unnecessary functions.
“Changing passwords on first use and enabling the automatic update function must be standard practice on all IoT devices, whether the device is used at home or in a corporate network. The greatest danger, besides vulnerabilities introduced by manufacturers, is using an IoT device according to the motto ‘plug, play and forget’,” IoT Inspector’s CEO Jan Wendenburg concludes.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, routers)
[adrotate banner=”5″]
[adrotate banner=”13″]


