
A New Zealander expert has found hundred of thousands of vulnerable engine immobilizers are remotely hackable due to a flaw.
The New Zealander Lachlan Temple (@skooooch) has discovered hundred of thousands of vulnerable engine immobilizers are remotely hackable. The expert discovered a flaw in a popular cheap car tracking and immobilizer gadget that can allow remote attackers to locate, eavesdrop, and in some cases interrupting the fuel supply to the engine to hundreds of thousands of vehicles, and more alarming, even while they are in motion.
Once the users have installed the engine immobilizers on their car they are able to remotely track the vehicle, block the engine, enable microphone recording, enable geo-fencing, and track the car movements.
The gadgets are rebranded by various vendors, including the Chinese ThinkRace, meanwhile in Australia the engine immobilizers are branded as “Response” and offered for sale at electronics chain JayCar for about A$150.

One of the models available on the market is able to control the car fuel pumps, a feature implemented to remotely immobilize a stolen vehicle, but Temple discovered that a an attacker could exploit a flaw in the management of session cookies to enable this function.
This means that while you are driving, someone everywhere is able to stop your engine!
Temple presented his findings at the Kiwicon security confab in Wellington, he added that today the flaws allow attackers who log into any account, including a demo account, to log into any of the 360,000 units ThinkRace that are sold without need of a password.

Lachlan Temple. Photo by Darren Pauli / The Register
“You just brute force everyone account, you can increment each one,” Temple told Vulture South. “You could disable someone’s car if they have wired the relay, so if that happened on a freeway that is pretty dangerous.” “Most people would wire it this way, that’s the main point of it and the reason why mechanics sell it.”
Temple suggests users to wire the relay to the starter motor, in this way a remote hacker cannot stop the engine while in motion and instead would prevent it starting up once turned off.
The flaws could be also exploited by attackers to access user personal details, including phone numbers, or eavesdrop on cars through the a microphone installed in the set of the engine immobilizers.
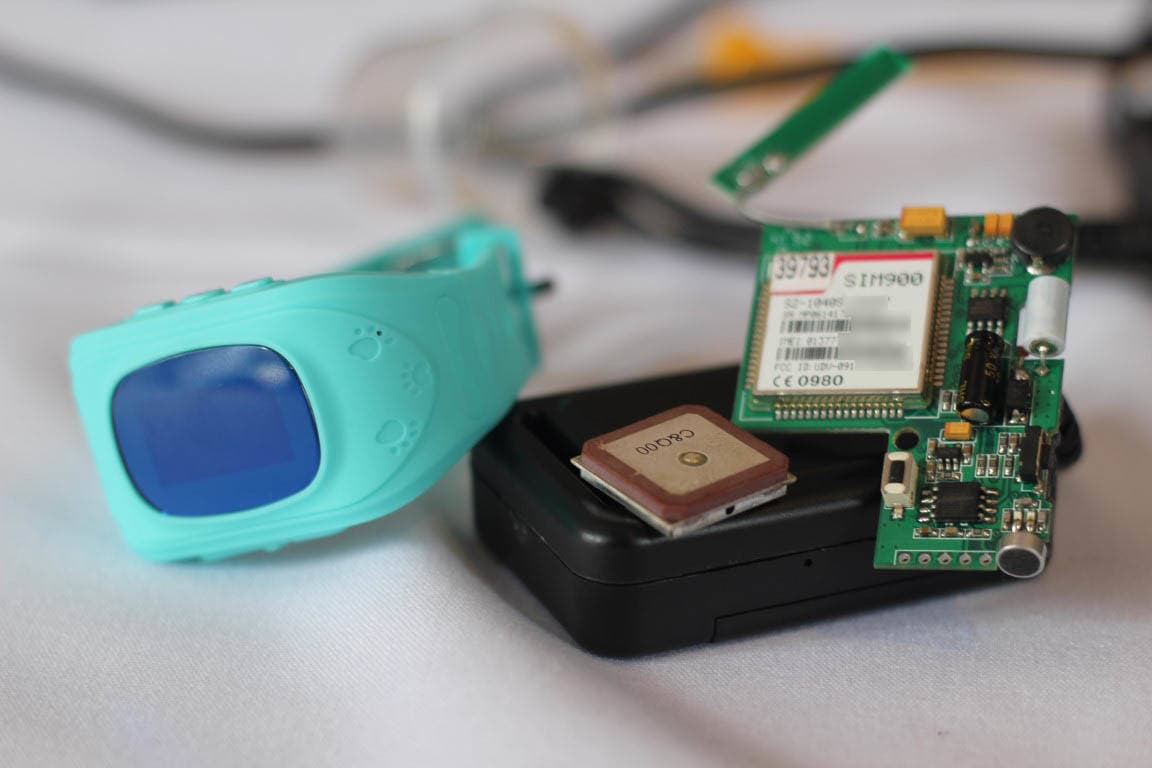
Temple discovered that the same tracker is used by ThinkRace in the watches sold to track children, in this case, an attacker can eavesdrop on kids and track them.
Temple announced that he will focus next test on more expensive tracking solution available on the market, including engine immobilizers used by commercial fleets of vehicles.
Stay Tuned …
(Security Affairs – engine immobilizers, car hacking)


