
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

WAGO Industrial Switches affected by multiple flaws

A security expert at SEC Consult discovered that some WAGO industrial managed switches are affected by several serious vulnerabilities. A security researcher at consulting company SEC Consult discovered several vulnerabilities in some models of WAGO industrial switches. The vulnerabilities affect WAGO industrial switches 852-303, 852-1305 and 852-1505 models. The company has already fixed the issues with […]

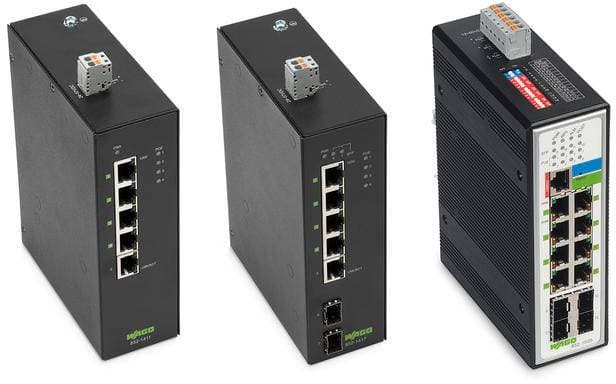
WAGO industrial switches 852

A security expert at SEC Consult discovered that some WAGO industrial managed switches are affected by several serious vulnerabilities.

A security researcher at consulting company SEC Consult discovered several vulnerabilities in some models of WAGO industrial switches.

The vulnerabilities affect WAGO industrial switches 852-303, 852-1305 and 852-1505 models. The company has already fixed the issues with the release of firmware versions 1.2.2.S0, 1.1.6.S0 and 1.1.5.S0, respectively.

“The industrial managed switch series 852 from WAGO is affected by multiple vulnerabilities such as old software components embedded in the firmware. Furthermore, hardcoded password hashes and credentials were also found by doing an automated scan with IoT Inspector.” reads the security advisory. “Two vulnerabilities (CVE-2017-16544 and CVE-2015-0235) were verified by emulating the device with the MEDUSA scaleable firmware runtime. The validity of the password hashes and the embedded keys were also verified by emulating the device.

One of the most severe issues is related to the presence of hardcoded credentials that can be used to connect the devices via Telnet and SSH.

“Hardcoded Credentials (CVE-2019-12550) – The device contains hardcoded users and passwords which can be used to login via SSH and Telnet.” continues the advisory.

The expert also found hardcoded private keys for the SSH daemon in the device’s firmware. An attacker can use them to carry out man-in-the-middle (MitM) attacks against the Dropbear SSH daemon without the victim noticing any fingerprint changes.

“The device contains hardcoded private keys for the SSH daemon. The fingerprint of the SSH host key from the corresponding SSH daemon matches to the embedded private key.” states the advisory.

SEC Consult also discovered that WAGO industrial switches use outdated versions of the BusyBox UNIX toolkit and the GNU C Library (glibc). Both libraries are affected by known vulnerabilities, some of which rated as critical.

Experts suggest restricting network access to the device and SSH server in order to protect the system. The good news is that affected switches are not exposed online.

The German VDE CERT has published an advisory to warn of the flaws in the WAGO devices.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Wago industrial switches, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


