
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A bug in the Walgreens mobile app leaked customers’ messages

Pharmacy store chain Walgreens has disclosed a data breach that impacted some customers of its mobile application. Pharmacy store chain Walgreens has disclosed a data breach that impacted some customers of its mobile application. The mobile app allows users to refill prescriptions by scanning barcode, manage medications with Pill Reminder, set Rx alerts for refills […]

Walgreens

Pharmacy store chain Walgreens has disclosed a data breach that impacted some customers of its mobile application.

Pharmacy store chain Walgreens has disclosed a data breach that impacted some customers of its mobile application.

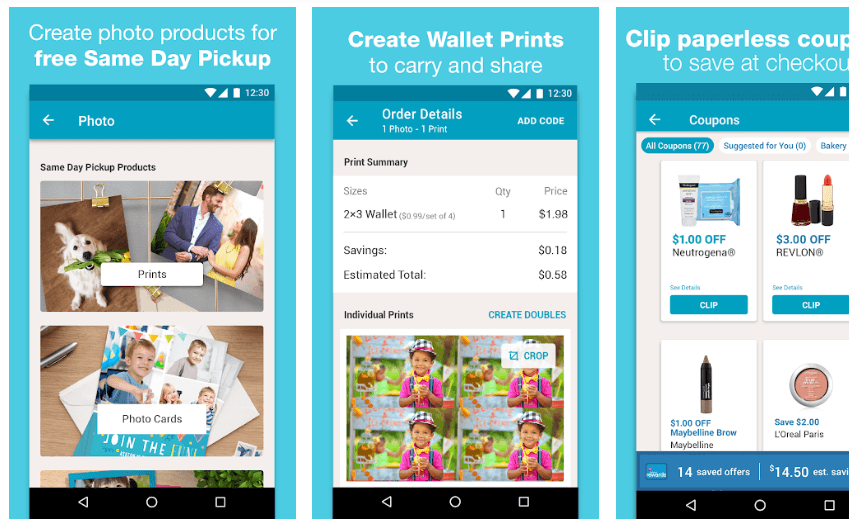
The mobile app allows users to refill prescriptions by scanning barcode, manage medications with Pill Reminder, set Rx alerts for refills and pickups, set up a video chat with doctors, refill and check prescription status, print photos, create personalized folded photo cards, and customize décor items.

The app already has over 10,000,000 millions of Android installs individuals and 50 million iOS installs.

According to the company, customers’ messages within the Walgreens mobile application may have been viewed by other users due to a bug in the personal secure messaging feature. The company discovered the issue on January 15, 2020, data was exposed between January 9 and January 15, 2020.

“We recently learned of unauthorized disclosure of one or more of your secure messages within the Walgreens mobile app. We are contacting you to provide you with information about the incident and also with information about steps you can take to protect yourself.” reads the data breach notification letter sent to the users.

“Our investigation determined that an internal application error allowed certain personal messages from Walgreens that are stored in a database to be viewable by other customers using the Walgreens mobile app. Once we learned of the incident, Walgreens promptly took steps to temporarily disable message viewing to prevent further disclosure and then implemented a technical correction that resolved the issue,”

Walgreens

The investigation conducted by the company revealed that information accessed by other customers might include first and last name, prescription number and drug name, store number, shipping address where applicable. The company revealed that financial information, such as Social Security number or bank account information, was not exposed.

At the time, it is nor clear how many customers have been affected.

Walgreens disabled the message viewing feature implemented in the mobile app to prevent further disclosure, meantime the company is working at a permanent correction.

“Walgreens promptly took steps to disable the message viewing feature within the Walgreens mobile app to prevent further disclosure until a permanent correction was implemented to resolve the issue. Walgreens will conduct additional testing as appropriate for future changes to verify the change will not impact the privacy of customer data,” concludes the notification.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – mobile app, data leak)

[adrotate banner=”5″]

[adrotate banner=”13″]


