
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Apple temporarily blocked Walkie-Talkie App on Apple Watch due to a flaw

A serious vulnerability in Walkie-Talkie App on Apple Watch forced the tech giant to disable the applications to avoid attackers spying on its users. Apple has temporarily disabled the Walkie-Talkie app on the Apple Watch due to a vulnerability that could be exploited to spy on users. The issue was reported to Apple via its report […]

apple Walkie-Talkie app

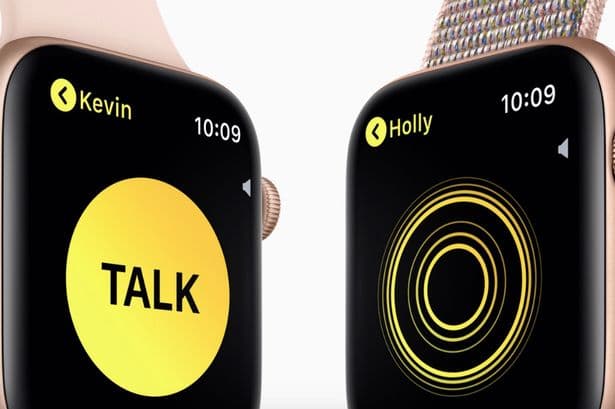
Apple Walkie-Talkie app – Source https://www.mirror.co.uk/tech/apple-watch-walkie-talkie-app-13237278

A serious vulnerability in Walkie-Talkie App on Apple Watch forced the tech giant to disable the applications to avoid attackers spying on its users.

Apple has temporarily disabled the Walkie-Talkie app on the Apple Watch due to a vulnerability that could be exploited to spy on users. The issue was reported to Apple via its report a vulnerability portal.

apple Walkie-Talkie app
Apple Walkie-Talkie app – Source The Mirror

The Walkie-Talkie app allows users to communicate with other users using a compatible Watch, it emulates the traditional behavior of walkie-talkie.

https://www.youtube.com/watch?v=7Op_I_dKS_k

According to TechCrunch, Apple is already working on a patch, but the application will not work until it will release a fix.

“Apple has disabled the Apple Watch Walkie Talkie app due to an unspecified vulnerability that could allow a person to listen to another customer’s iPhone without consent, the company told TechCrunch this evening.” reads the post published by TechCrunch. “Apple has apologized for the bug and for the inconvenience of being unable to use the feature while a fix is made.”

An attacker can use another user’s iPhone to listen to communications made throgh the app, at the time no other technical details have been made publicly disclosed.

“Although we are not aware of any use of the vulnerability against a customer and specific conditions and sequences of events are required to exploit it, we take the security and privacy of our customers extremely seriously,” reads a statement from Apple. “We concluded that disabling the app was the right course of action as this bug could allow someone to listen through another customer’s iPhone without consent.”

The good news is that Apple is not aware of attacks in the wild exploiting the vulnerability.

Early this year, another major vulnerability in the Apple FaceTime allowed hearing the audio of the person you were calling before he picks up the call.

At the time, privacy advocated and authorities raised concerns about how Apple managed to address the issue.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – walkie-talkie app, GDPR)

[adrotate banner=”5″]

[adrotate banner=”13″]


