
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Police seized two Tor relays investigating WannaCry attack, others disappeared in the same period

France’s cyber-crime investigation unit OCLCTIC seized one server running two Tor Relays Investigating the WannaCry attack. A few days after the massive WannaCry attack the French authorities seized a server running two Tor relays in connection to the ransomware campaign, both relays were also working as Tor entry guard nodes, key components of Tor routing when […]

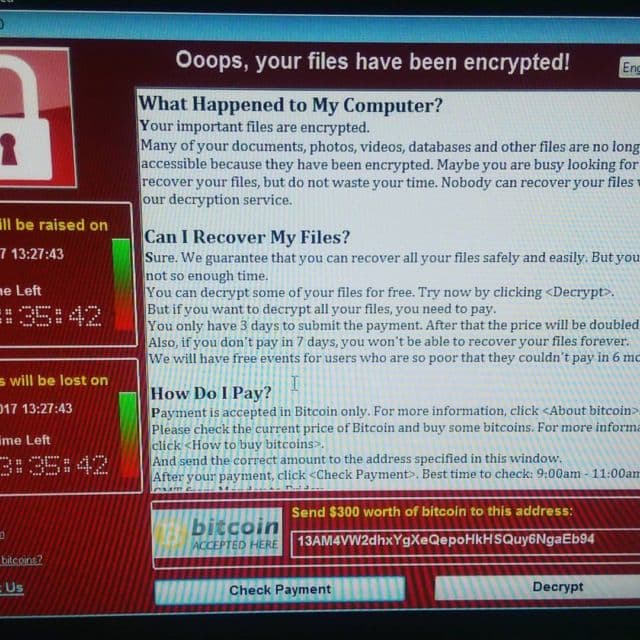
WannaCrypt ransomware

France’s cyber-crime investigation unit OCLCTIC seized one server running two Tor Relays Investigating the WannaCry attack.

A few days after the massive WannaCry attack the French authorities seized a server running two Tor relays in connection to the ransomware campaign, both relays were also working as Tor entry guard nodes, key components of Tor routing when users connect the anonymizing network.

The server was operated by the French activist Aeris that reported the police’s action through the Tor Project mailing on May 15 asking other Tor operators to revoke trust in the two seized relays.

The server was seized by France’s cyber-crime investigation unit OCLCTIC (L’Office Central de Lutte contre la Criminalité liée aux Technologies de l’Information et de la Communication).

WannaCry ransomware

According to Aeris, the police seized the server hosted at hosting company Online SAS, because the traffic associated with WannaCry ransomware that infected a big French company on May 12 was pointing the two Tor relays.

The WannaCry samples that infected the company were communicating with a command and control server hosted on the Tor Network, and it is likely that the server were used as a first hop of the Tor traffic.

“Most Tor servers are configured to log very few details, such as uptime and status metrics, so to safeguard the privacy of its users. Unless Aeris made customizations to default configs, French police have no chance of finding any useful information on the seized servers.” reported Catalin Cimpanu from Bleepingcomputer.com.

Aeris confirmed that tens of other Tor nodes in France disappeared just after the WannaCry attack, he provided Bleeping Computer a list of 30 servers he is currently investigating.

“We have confirmation of 6 Tor nodes seizures [from 5 operators],” the activist told Bleeping Computers. ” A seized relay is not of this list because of hosted on another provider.”

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – Tor, WannaCry)

[adrotate banner=”13″]


