
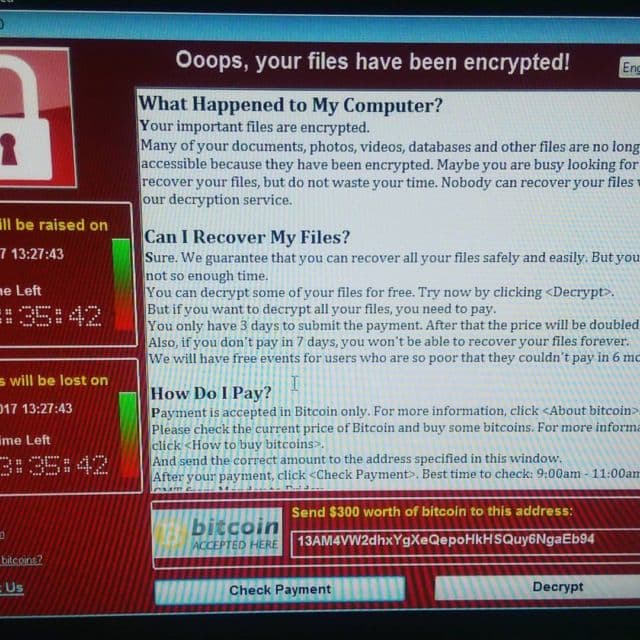
Security experts at threat intelligence firm Flashpoint conducted a linguistic analysis of dozens of ransom notes displayed by the WannaCry ransomware.
Malware researchers at threat intelligence firm Flashpoint conducted a linguistic analysis of 28 ransom notes displayed by the WannaCry ransomware.
Flashpoint analyzed 28 WannaCry ransom notes written in various language including Chinese (both simplified and traditional), Danish, Dutch, English, French, German, Indonesian, Italian, Japanese, Korean, Norwegian, Portuguese, Romanian, Russian, Spanish, Swedish and Turkish.
According to the experts, authors of the malware are fluent Chinese speakers and they also appear to know English.
Recently the security researcher at Google Neel Mehta, the experts at Kaspersky Lab and Symantec linked the threat to the North Korea-linked Lazarus APT due to similarities in a portion of code that Neel noticed in a very early variant of WannaCry ransomware found in February 2017 and in one of the malware used by the notorious APT group dated back February 2015.
The Chinese notes appear well written and more accurate of others.
“A number of unique characteristics in the note indicate it was written by a fluent Chinese speaker. A typo in the note, “帮组” (bang zu) instead of “帮助” (bang zhu) meaning “help,” strongly indicates the note was written using a Chinese-language input system rather than being translated from a different version. More generally, the note makes use of proper grammar, punctuation, syntax, and character choice, indicating the writer was likely fluent or at least native. There is, however, at least one minor grammatical error which may be explained by autocomplete, or a copy-editing error.” reads the analysis published by Flashpoint.
Experts highlighted that at least one of the words used in the Chinese note is more common in South China, Hong Kong, Singapore and Taiwan, while another term is more widely adopted in China mainland.
“The text uses certain terms that further narrow down a geographic location. One term, “礼拜” for “week,” is more common in South China, Hong Kong, Taiwan, or Singapore. The other “杀毒软件” for “anti-virus” is more common in the Chinese mainland.” continues the analysis
“Perhaps most compelling, the Chinese note contains substantial content not present in any other version of the note, is lengthier, and differs slightly in format.”
The English note of the ransomware appears well written, but it contains a major grammar mistake that suggests its author is either not a native speaker or possibly someone poorly educated.
In the following table, we can see the percent identical by word count between Google translate and WannaCry note versions.

“Given these facts, it is possible that Chinese is the author(s)’ native tongue, though other languages cannot be ruled out,” Flashpoint concluded. “It is also possible that the malware author(s)’ intentionally used a machine translation of their native tongue to mask their identity. It is worth noting that characteristics marking the Chinese note as authentic are subtle. It is thus possible, though unlikely, that they were intentionally included to mislead.”
The Flashpoint analysis suggests attackers may have used the Lazarus code as a false flag to deceive investigators, a second scenario sees North Korean APT recruiting freelance Chinese hackers to conduct the campaign.
[adrotate banner=”9″]
(Security Affairs – Wannacry ransomware, hacking)
[adrotate banner=”13″]


