
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

It’s Monday, how to avoid being infected with the WannaCry ransomware

The number of victims would rise on Monday when a large number of users will be back at work, then how to protect your systems from the WannaCry ransomware. The massive WannaCry attack targeted systems worldwide, according to the Europol the number of cyber attack hits 200,000 in at least 150 countries. The number of […]

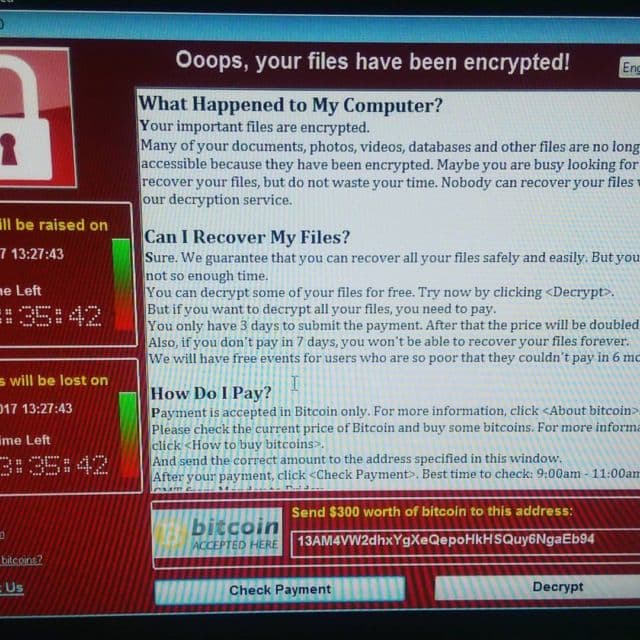
WannaCrypt ransomware

The number of victims would rise on Monday when a large number of users will be back at work, then how to protect your systems from the WannaCry ransomware.

The massive WannaCry attack targeted systems worldwide, according to the Europol the number of cyber attack hits 200,000 in at least 150 countries. The number of victims would rise on Monday when a large number of users will be back at work.
WannaCry ransomware 3.jpg

Europol Director Rob Wainwright told ITV’s Peston on Sunday program that we are facing an unprecedented attack.

“The global reach is unprecedented. The latest count is over 200,000 victims in at least 150 countries, and those victims, many of those will be businesses, including large corporations,” he said.

“At the moment, we are in the face of an escalating threat. The numbers are going up; I am worried about how the numbers will continue to grow when people go to work and turn (on) their machines on Monday morning.”

Experts believe it will be a black Monday, considering also that in the last hours, new versions of the WannaCry ransomware have been detected in the wild with a new kill switch.

https://twitter.com/msuiche/status/863730377642442752

The are a few things that must be clear about the threat:

The WannaCry ransomware spread itself within corporate networks, without user interaction, by exploiting the EternalBlue vulnerability in Microsoft Windows.

The ransomware drops mssecsvc.exe binary in the C:\windows folder.

The WannaCry ransomware installs itself as a service and executes these two activities:
  • files encrypting.
  • propagating malware through the local network by exploiting a flaw in the SMB protocol via 445 e 139 TCP ports. The malware searches for new machines to infect.
Below a few suggestions to protect your systems:

Against ransomware-based attacks keep your backup up to date.

  • Install the Microsoft MS17-010 security updates published on March 14.
  • Keep your antivirus software up-to-date.
  • Disable, if not necessary, the Server Message Block (SMB) e Remote Desktop Protocol (RDP) services;
  • To avoid being infected by other ransomware do not open links and attachments embedded in unsolicited email messages.

System administrators urge to apply security updates to the network devices used to protect their infrastructure and identify the threats (e.g. IPS/IDS).

Block any suspicious incoming traffic using SMB and RDP protocols.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – WannaCry ransomware, cybercrime)

[adrotate banner=”13″]


