Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

WarBerry Pi, a Tactical Exploitation device

If you need to test your environment in a short period of time the WarBerry Pi is the right device to gather information on the target network. WarBerry Pi is a device that could be used by pen testers to collect as much information as possible in a short period of time, without being noticed. In order […]

WarBerry Pi, a Tactical Exploitation device

If you need to test your environment in a short period of time the WarBerry Pi is the right device to gather information on the target network.

WarBerry Pi is a device that could be used by pen testers to collect as much information as possible in a short period of time, without being noticed. In order to use it, a security expert just needs to plug it in a network port.

The WarBerry Pi was designed only for academic purposes, but obviously, someone could think to use it to gather authorization from a network, for this reason, the author SecGroundZero bears no responsibility for any abuse.

“The WarBerry was built with one goal in mind; to be used in red teaming engagement where we want to obtain as much information as possible in a short period of time with being as stealth as possible. Just find a network port and plug it in.” states the description of the project published on GitHug. “The scripts have been designed in a way that the approach is targeted to avoid noise in the network that could lead to detection and to be as efficient as possible. The WarBerry script is a collection of scanning tools put together to provide that functionality.”

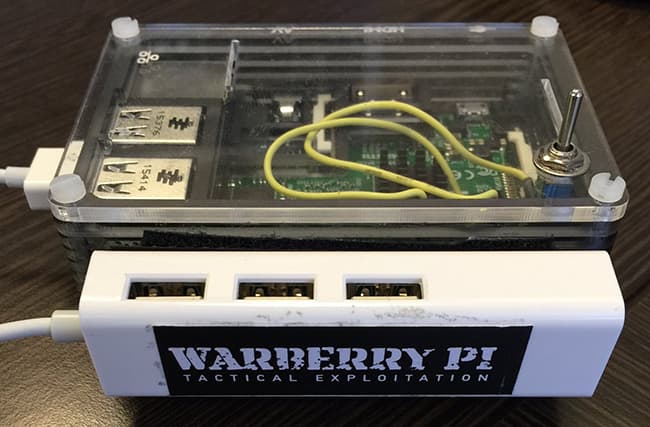
Warberry Pi device

Source – HelpNet Security

How does it works, once connected the WarBerry Pi to the target network, it has the capability to remain silent and collect information on the internal traffic by collecting IPs, MAC addresses and hostnames.

Such kind of devices is very insidious, they could represent a serious threat to any environment, once deployed they could be used by attackers to remote exfiltrate information. In the past, we have seen how to hide a Raspberry Pi in an ordinary laptop power brick, an object very common in any office and realizing in this way a physical backdoor into the network.

The project WarBerry Pi was published on Github provided instruction on its usage, once installed in the network an attacker can access it through SSH and check the data collected by the device that is stored in a specific folder dubbed “Results”.

The device highlights the importance of the physical security in any environment, the WarBerry Pi was designed to train blue teams to monitor for a possible intrusion in the network and block it.

SecGroundZero plans to release similar projects to train internal team against Wi-Fi and Bluetooth attacks.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – WarBerry Pi, hacking)