
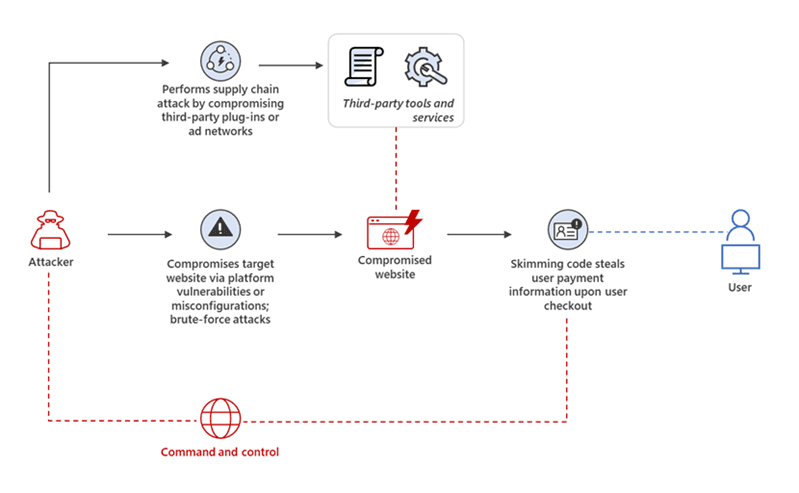
Threat actors behind web skimming campaigns are using malicious JavaScript to mimic Google Analytics and Meta Pixel scripts to avoid detection.
Microsoft security researchers recently observed web skimming campaigns that used multiple obfuscation techniques to avoid detection.
The threat actors obfuscated the skimming script by encoding it in PHP, which, in turn, was embedded in an image file, using this trick the code is executed when a website’s index page is loaded.
The experts also observed compromised web applications injected with malicious JavaScript masquerading as Google Analytics and Meta Pixel (formerly Facebook Pixel) scripts. Some skimming scripts also included anti-debugging mechanisms.
The term web skimming refers to the criminal practice to harvest payment information of visitors of a website during checkout. Crooks use to exploit vulnerabilities in e-commerce platforms and CMSs to inject the skimming script into the page of the e-store. In some cases, attackers can exploit vulnerabilities in installed third-party plugins and themes to inject malicious scripts.

“During our research, we came across two instances of malicious image files being uploaded to a Magento-hosted server. Both images contained a PHP script with a Base64-encoded JavaScript, and while they had identical JavaScript code, they slightly differed in their PHP implementation.” reads the analysis published by Microsoft. “The first image, disguised as a favicon (also known as a shortcut or URL icon), was available on VirusTotal, while the other one was a typical web image file discovered by our team.”
Microsoft also observed attackers masquerading as Google Analytics and Meta Pixel (formerly Facebook Pixel) scripts to avoid raising suspicion.
The attackers place a Base64-encoded string inside a spoofed Google Tag Manager code. This string decoded to trafficapps[.]business/data[.]php?p=form.

Experts noticed that the attackers behind the Meta Pixel spoofing used newly registered domains (NRDs) using HTTPS.
“Given the increasingly evasive tactics employed in skimming campaigns, organizations should ensure that their e-commerce platforms, CMSs, and installed plugins are up to date with the latest security patches and that they only download and use third-party plugins and services from trusted sources,” Microsoft concludes.
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, web skimming attacks)
[adrotate banner=”5″]
[adrotate banner=”13″]


