
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Hacking

WhatsSpy Public tool can spy on Whatsapp users

WhatsSpy Public is a web-based tool that could allow an attacker to access Whatsapp user information related to his activity. WhatsSpy Public is a web-based tool created by Maikel Zweerink that can trace the moves of a WhatsApp user. WhatsSpy is able to display user information in a friendly dashboard that includes events being displayed […]

WhatsSpy Public tool can spy on Whatsapp users

WhatsSpy Public is a web-based tool that could allow an attacker to access Whatsapp user information related to his activity.

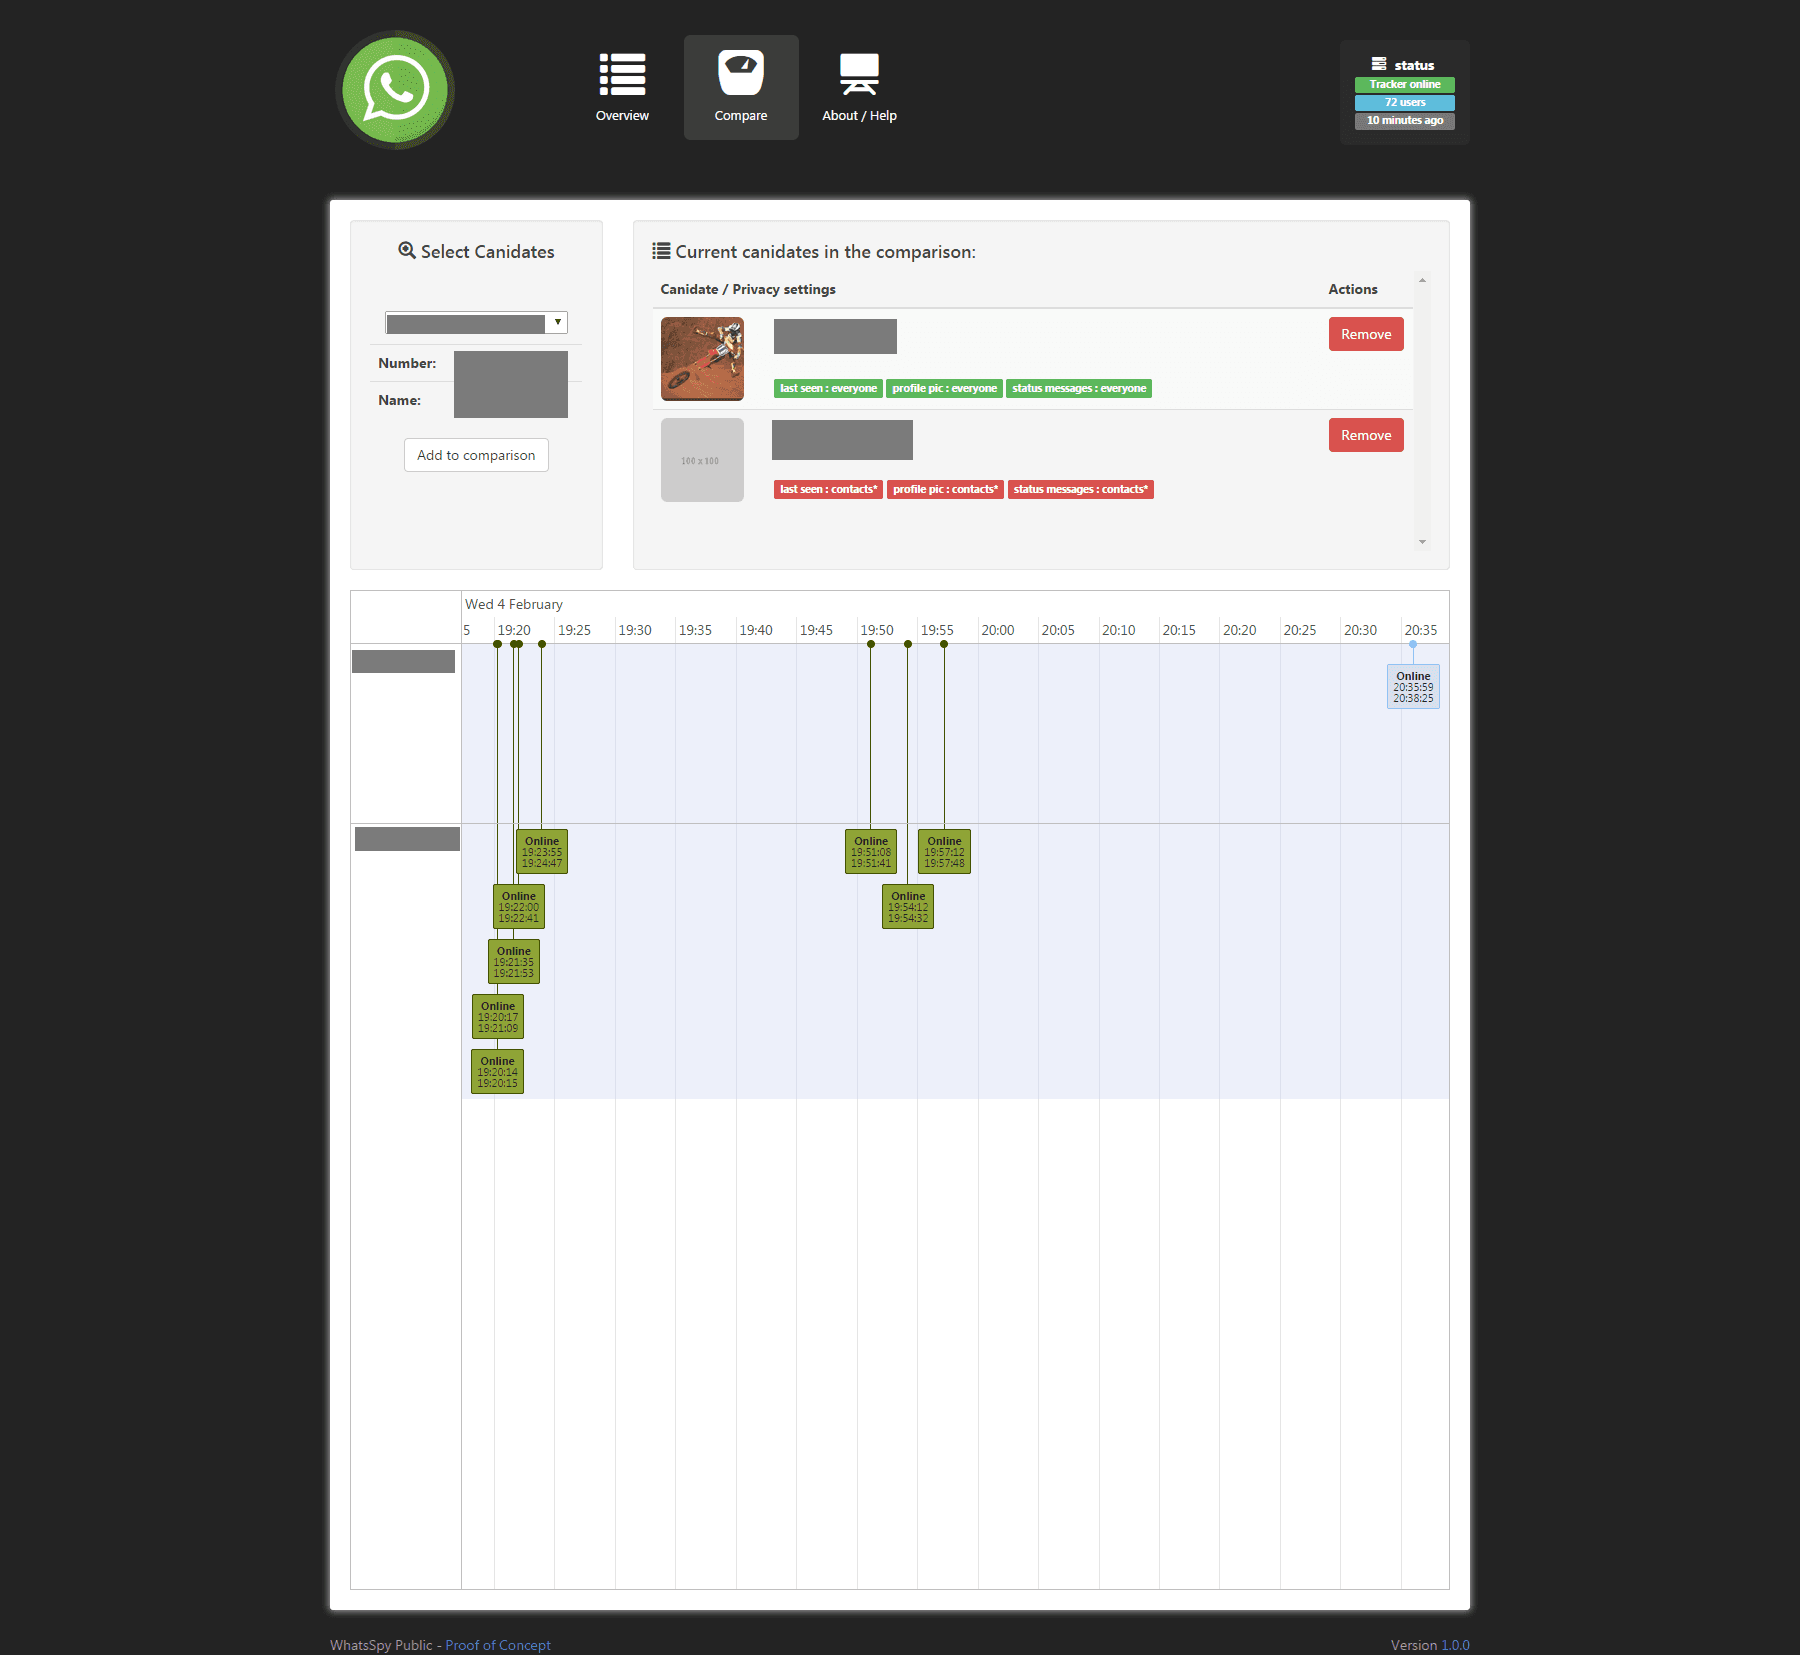
WhatsSpy Public is a web-based tool created by Maikel Zweerink that can trace the moves of a WhatsApp user. WhatsSpy is able to display user information in a friendly dashboard that includes events being displayed in a timeline.

whatsspy Public

The tool also allows experts to compare timelines of two users in order to conduct cross analysis. Zweerink has released the WhatsSpy Public tool on GitLab as a proof-of-concept that WhatsApp privacy is broken, he highlighted the application doesn’t rely on a specific hack or exploit.

Maikel Zweerink explained that he has discovered that some of the events sent out by the messaging app could be intercepted by anyone. Among the data that could be eavesdropped, there is the current status (independently of privacy settings), change of profile pictures, message status and any modification of privacy settings.

whatsspy Public 2

By analyzing the WhatsSpy Public dashboard it is possible to discover the exact moment when users start to use WhatsApp and when they disconnect from the service.

“WhatsSpy Public is an web-oriented application that tracks every move of whoever you like to follow. This application is setup as an Proof of Concept that Whatsapp is broken in terms of privacy. Once you’ve setup this application you can track users that you want to follow on Whatsapp. Once it’s running it keeps track of the following activities:”explained Zweerink  on the project page.

“I made this project for you to realise how broken the privacy options actually are. It just started out as experimenting with Whatsapp to build an Bot, but I was stunned when I realised someone could abuse this ‘online’ feature of Whatsapp to track anyone,” 

On the project page are reported the instructions for the installation of the WhatsSpy Public tool in Raspberry Pi, Server and VPS. The requirements includes:

  • Secondary Whatsapp account (phonenumber that doesn’t use Whatsapp)
  • Rooted Android phone OR Jailbroken iPhone OR PHP knowledge
  • Server/RPi that runs 24/7
  • Nginx or Apache with PHP (you can’t host on simple webhoster, you need bash)
  • Postgresql

There is no peace for Whatsapp users, recently the researcher Indrajeet Bhuyan discovered two privacy issues in Whatsapp web application and in the last months the same experts has discovered a way to crash the mobile application by sending specially crafted messages.

(Security Affairs –  Whatsapp, WhatsSpy Public)


