
After a weekend of outage and various mysterious password reset emails Apple has revealed that the iOS Developer Center was hacked.
After 3 days of absolute silence of the voice of a possible hack to the IOS Developer Center, Apple has just confirmed that it was the victim of a cyber attack. The iOS Developer Center web site has been down during this day and Apple officially announced that the company was the victim of a data breach and is investigating on the event.
Apple’s developers were informed of the data breach with a legitimate mail, its content revealed that the company detected a security breach on its Dev Center servers last Thursday.
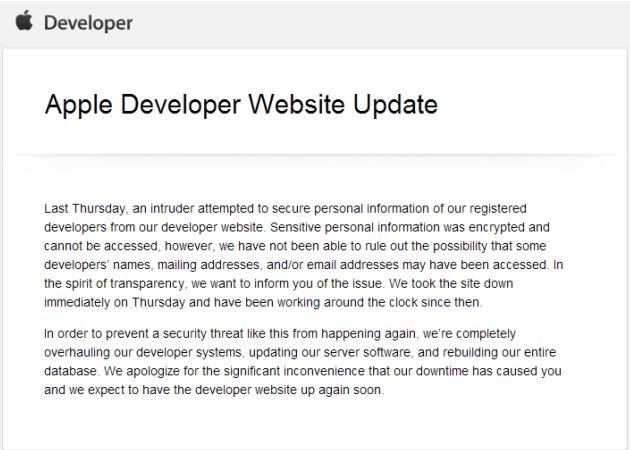
Despite the majority of the information was encrypted the attackers may have accessed developer’s personal information such as names, addresses, and email addresses. To prevent further damage Apple decided to suspend the iOS Developer Center service:
“In order to prevent a security threat like this from happening again, we’re completely overhauling our developer systems, updating our server software, and rebuilding our entire database.”
Immediately after that attack many developers reported various attempts of attacks, since the developer center went down on Thursday, dozens of developers reported receiving unsolicited password reset requests.
An Apple’s representative confirmed that:
- The hack only affected developer accounts meanwhile standard iTunes accounts were not exposed
- No credit card number has been exposed
- Apple waited three days to alert developers because it was trying to figure out exactly what data was breached
- There is no time table yet for when the Dev Center will return
Who is responsible for the attack?
A security researcher named Brahim BALİÇ (Ibrahim Balic) taking the credit for the breach to the iOS Developer Center, he issued a post against in which he revealed to have found 13 bugs reported to Apple including a vulnerability that allowed the access to users’ information.

“In total I have found 13 bugs and have reported through http://bugreport.apple.com. The bugs are all reported one by one and Apple was informed. I gave details to Apple as much as I can and I’ve also added screenshots.
One of those bugs has provided me access to the users’ details etc. I immediately reported this to Apple. I have taken 73 users details (all apple inc workers only) and prove them as an example.
4 hours later from my final report Apple developer portal gas closed down and you know it still is.”
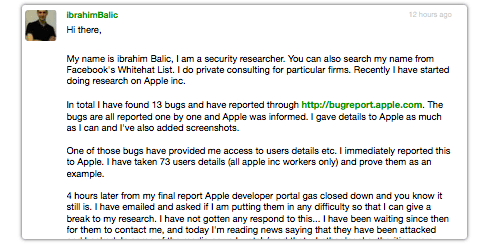
Resuming the researcher revealed the bugs in iOS Developer Center to Apple just before the site went down, and he hasn’t limited his proof of concept to 73 users details but he went ahead stealing more that 100,000 user’s personal information and published a video that I decided to non publish because contains references to hacked content.

It’s not the first time that Apple is hacked, early 2013 Apple confirmed to Reuters press agency that it was hit by a series of cyber attacks as part of the hacking campaign that targeted US news agencies and other enterprises.
What is interesting to note is the incident response for serious bugs, these ones found the iOS Developer Center seems to be critical judging the decision to stop the website for a few days, probably the vulnerabilities could give the access to more sensitive information contained in the same servers so Apple decided to suspend the activities since it has secured its architecture.
Pierluigi Paganini
(Security Affairs – Hacking, iOS Developer Center, Apple)


