
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emails among dumps published by Wikileaks includes 300+ malware

A malware researcher has analyzed the attachments of in the WikiLeaks email dumps and discovered more than 300 pieces of malware. WikiLeaks has published more than 300 pieces of malicious code among its caches of dumped emails. Dr Vesselin Bontchev (@bontchev), a top Bulgarian malware researcher, has analyzed documents published by the organization and detected […]

Emails among dumps published by Wikileaks includes 300+ malware

A malware researcher has analyzed the attachments of in the WikiLeaks email dumps and discovered more than 300 pieces of malware.

WikiLeaks has published more than 300 pieces of malicious code among its caches of dumped emails. Dr Vesselin Bontchev (@bontchev), a top Bulgarian malware researcher, has analyzed documents published by the organization and detected 324 instances of malware in its archive of dumped emails.

A check to the instance of malware allowed the malware expert to discover that the almost any instance appears to be an attachment of the dumped email.

The malicious codes are recognized by the Virus Total malware and URL online scanning service, they were likely sent by attackers to the recipients in the attempt to hack them.

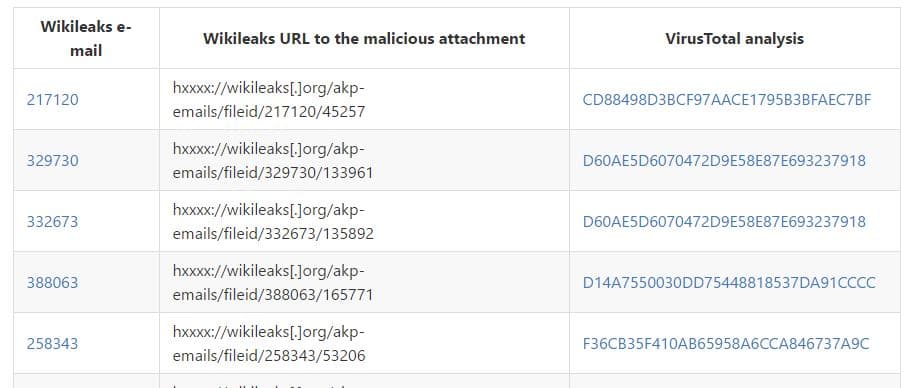
“The following table contains the confirmed malware residing on the Wikileaks site. The list is by no means exhaustive; I am just starting with the analysis. But what is listed below is definitely malware; no doubts about it.” wrote Dr Bontchev on GitHub.

“The first column contains a link to the e-mail on the Wikileaks site that contains the malicious attachment. The e-mail itself is safe to view (although the text is usually spam/scam/phish/whatever).”

wikileaks email malware

The situation may be worse because the piece of malware found by the Bulgarian researchers were identified in an initial search effort.

If you want to test the malware adopt all the necessary countermeasures to avoid infecting your machine.

Fortunately, the piece of malware are well known to the principal antivirus solutions, according to the malware researcher, the majority of the malicious codes have a Virus Total detection rate from 80 to 100 percent.

Anyway … be careful managing email attachments from Wikileaks archives.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs –  Wikileaks, malware)


