
Researcher discovers a zero-day vulnerability in Windows 7 and Windows Server 2008 while he was working on a Windows security tool.
The French security researcher Clément Labro discovered a zero-day vulnerability was discovered while the security researcher was working on an update Windows security tool.
The researcher was developing his own Windows privilege escalation enumeration script, named PrivescCheck, which is a sort of updated and extended version of the famous PowerUp.
“If you have ever run this script on Windows 7 or Windows Server 2008 R2, you probably noticed a weird recurring result and perhaps thought that it was a false positive just as I did. Or perhaps you’re reading this and you have no idea what I am talking about.” wrote the expert. “Anyway, the only thing you should know is that this script actually did spot a Windows 0-day privilege escalation vulnerability. Here is the story behind this finding…”
The expert confirmed that the flaw impacts the Windows 7 and Windows Server 2008 R2 operating systems.
The vulnerability impacts two misconfigured registry keys for the RPC Endpoint Mapper and DNSCache services.
- HKLM\SYSTEM\CurrentControlSet\Services\RpcEptMapper
- HKLM\SYSTEM\CurrentControlSet\Services\Dnscache
An attack with access to vulnerable systems can modify these registry keys to activate a sub-key with the name of the user’s service usually employed by the Windows Performance Monitoring mechanism.
The researchers was looking for some sort of tree structure detailing all the subkeys and values defining a service’s configuration when he found some interesting info on using “Performance” and “DLL” keywords.
A performance key specifies information for optional performance monitoring. It is possible to specify the name of the driver’s performance DLL and the names of certain exported functions in that DLL by setting the values under this key using AddReg entries in the driver’s INF file. This implies that it is theoretically possible to register a DLL in a driver service in order to monitor its performances using the Performance subkey.
This mechanism is still available in Windows 7 and Windows Server 2008 and allows developers to load their own DLL files to monitor performance using their own tools.
At the time of writing it is impossible to know if Microsoft will address the vulnerability disocvered by Labro.
Although both Windows OSs have reached the end of support in January 2020 this year, they will be covered by the Extended Security Updates (ESU) until January 2023, which means that even fully ESU-updated machines are currently affected by this issue.
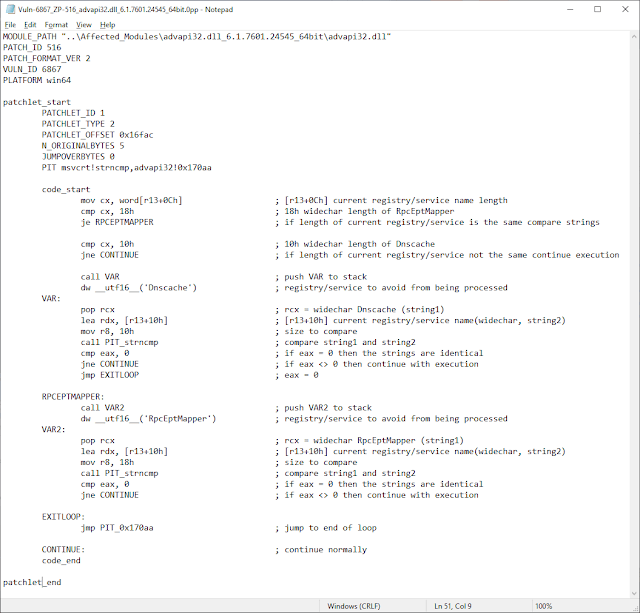
Researchers at 0patch, have developed their own micropatch for the zero-day in Windows 7 and Server 2008 R2.
“As an alternative to ESU, we at 0patch have “security adopted” Windows 7 and Windows Server 2008 R2 and are providing critical security patches for these platforms. Consequently, vulnerabilities like this one get our attention – and, usually, micropatches.” reported 0patch.

| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Windows)
[adrotate banner=”5″]
[adrotate banner=”13″]


