
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

SandboxEscaper released PoC code for a new Windows zero-day

Security expert SandboxEscaper published a proof-of-concept (PoC) code for a new Windows zero-day, it is the fourth she released this year. The proof-of-concept (PoC) code published by SandboxEscaper overwrites ‘pci.sys’ with information about software and hardware problems, collected through the Windows Error Reporting (WER) event-based feedback infrastructure. SandboxEscaper initially announced the release of the PoC code […]

Windows zero-day SandboxEscaper Windows Zero-day

Security expert SandboxEscaper published a proof-of-concept (PoC) code for a new Windows zero-day, it is the fourth she released this year.

The proof-of-concept (PoC) code published by SandboxEscaper overwrites ‘pci.sys’ with information about software and hardware problems, collected through the Windows Error Reporting (WER) event-based feedback infrastructure.

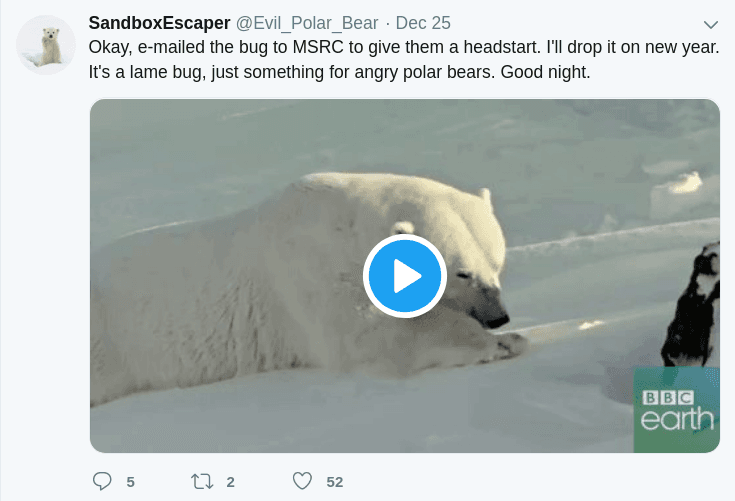
SandboxEscaper initially announced the release of the PoC code for the new year, but she decided to publicly disclose it two days after the Christmas day.

The expert warns of some limitations for the exploit code that may not work on some CPUs, for example, it could not work on systems based on a single CPU core.

SandboxEscaper also added that it could take time to trigger the issue because it relies on a race condition and other operations may break the outcome.

SandboxEscaper added that the exploit code could be used to disable third-party AV software.

“You can also use it to perhaps disable third-party AV software,” the expert explained.

Will Dormann, a security expert at CERT/CC, was able to successfully execute the exploit code on  Windows 10 Home, build 17134. The expert confirmed that the exploit not always works.

Experts from BleepingComputer pointed out that the exploit code could cause a DoS condition.

“Since the target is ‘pci.sys,’ SandboxEscaper’s PoC can cause a denial-of-service on the machine, from a user that does not have administrative privileges. ‘Pci.sys’ a system component necessary for correctly booting the operating system, since it enumerates physical device objects.” reads a blog post published on BleepingComputer.

SandboxEscaper said that she has reported the bug to the Microsoft Security Response Center (MSRC) once published.

Windows zero-day SandboxEscaper Windows Zero-day

SandboxEscaper disclosed another Windows zero-day in December, it
is an arbitrary file read vulnerability that could be exploited by a low-privileged user or a malicious program to read the content of any file on a Windows system.

Since August, SandboxEscaper has publicly dropped exploits for two Windows zero-day vulnerabilities forcing Microsoft to quickly address them to avoid its users being targeted by hackers.

In October, SandboxEscaper released the proof-of-concept exploit code for Microsoft Data Sharing that allowed a low privileged user to delete critical system files from Windows systems.

In August, SandboxEscaper released the PoC exploit for a local privilege escalation flaw in Microsoft Windows Task Scheduler.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Windows zero-day, hacking)

[adrotate banner=”5″] [adrotate banner=”13″]


