
Security Affairs
U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Tenable experts found 15 flaws in wireless presentation systems

Experts at Tenable discovered 15 vulnerabilities in eight wireless presentation systems, including flaws that can be exploited to remotely hack devices. Wireless presentation systems are used to display content on a screen or through several devices, including mobile devices and laptops. These systems are widely used in enterprises and educational organizations. Researchers at Tenable discovered […]

wireless presentation systems

Experts at Tenable discovered 15 vulnerabilities in eight wireless presentation systems, including flaws that can be exploited to remotely hack devices.

Wireless presentation systems are used to display content on a screen or through several devices, including mobile devices and laptops. These systems are widely used in enterprises and educational organizations.

Researchers at Tenable discovered 15 vulnerabilities in eight wireless presentation systems, some of them can be exploited for command injection and for gaining access to a device.

“Tenable found multiple vulnerabilities while investigating a Crestron AM-100. Tenable also discovered that the Crestron AM-100 shared a code base with the Barco wePresent, Extron ShareLink, InFocus LiteShow, TEQ AV IT WIPS710, SHARP PN-L703WA, Optoma WPS-Pro, Blackbox HD WPS, and possibly others.” reads the analysis published by Tenable. “The vulnerabilities listed below do not affect all devices”

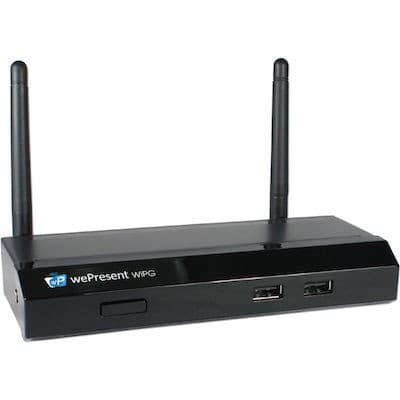
The experts focused their tests on Crestron AirMedia AM-100 and AM-101 products, but systems from other vendors could be affected because these devices reuse portions of code. Experts discovered that some of the issues they discovered also impact Barco wePresent, Extron ShareLink, InFocus LiteShow, TEQ AV IT WIPS710, SHARP PN-L703WA, Optoma WPS-Pro, Blackbox HD WPS, and potentially other vendors.

wireless presentation systems

Several flaws could be exploited by a remote, unauthenticated attacker to inject operating system commands. Others issues can be exploited by
a remote, unauthenticated attacker to change admin and moderator passwords and view presentations.

The issues, including a hardcoded session ID, allow unauthenticated, remote attacker to stop, start, and disconnect any screen sharing session due to insufficient authentication checking in the moderator controls. 

Experts also found a denial-of-service (DoS) flaw and credentials stored in plain text that could be accessible to authenticated users.

Searching for Crestron AirMedia devices exposed online with Shodan, we can find hundreds of devices, most of them located in the US, followed by Canada and Finland.

Tenable started reporting the vulnerabilities to vendors in January, but at the time of the public disclosure, only Extron and Barco have released firmware updates.

Waiting for the fix, users have to configure their environments to avoid these systems being exposed to the internet.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – wireless presentation systems, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


