
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Flaws in Wyze cam devices allow their complete takeover

Wyze Cam devices are affected by three security vulnerabilities that can allow attackers to takeover them and access camera feeds. Bitdefender researchers discovered three security vulnerabilities in the popular Wyze Cam devices that can be exploited by threat actors to execute arbitrary code and access camera feeds. The three flaws reported by the cybersecurity firm […]

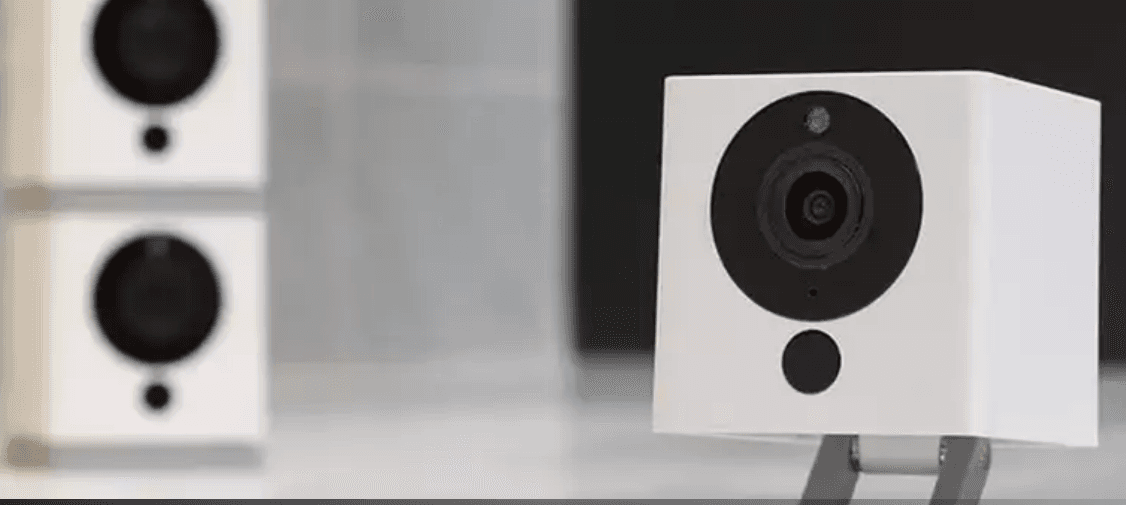
wyze cam 2

Wyze Cam devices are affected by three security vulnerabilities that can allow attackers to takeover them and access camera feeds.

Bitdefender researchers discovered three security vulnerabilities in the popular Wyze Cam devices that can be exploited by threat actors to execute arbitrary code and access camera feeds.

The three flaws reported by the cybersecurity firm are:

  • An authentication bypass tracked CVE-2019-9564
  • A stack-based buffer overflow, tracked as CVE-2019-12266, which could lead to remote control execution.
  • An unauthenticated access to contents of the SD card

A remote attacker could exploit the CVE-2019-9564 flaw to take over the device, including turning on/off the camera.

An attacker could chain the above issue with the CVE-2019-12266 flaw to access live audio and video feeds.

The flaws were reported to Wyze in May 2019, the company addressed the CVE-2019-9564 and CVE-2019-12266 flaws in September 2019 and November 2020, respectively.

The vendor addressed the unauthenticated access to the content of the SD card with the release of firmware updates on January 29, 2022.

According to the experts, there are 3 version of Wyze Cam devices on the market and the first one has been discontinued and will not receive security updates to address the flaws.

“The analyzed device comes in several versions: Wyze Cam version 1, Wyze Cam Black version 2, as well as Wyze Cam version 3. We learned that, while versions 2 and 3 have been patched against these vulnerabilities, version 1 has been discontinued and is no longer receiving security fixes.” reads the report published by the security firm. “Customers who keep using Wyze Cam version 1 are no longer protected and risk having their devices exploited.“

wyze cam 2
Source Punto Informatico website

Bitdefenders also provided the following recommendations to prevent attacks against IoT devices:

“Home users should keep a close eye on IoT devices and isolate them as much as possible from the local or guest network,” reads the post. “This can be done by setting up a dedicated SSID exclusively for IoT devices, or by moving them to the guest network if the router does not support the creation of additional SSIDs.”

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Wyze cam devices)

[adrotate banner=”5″]

[adrotate banner=”13″]


