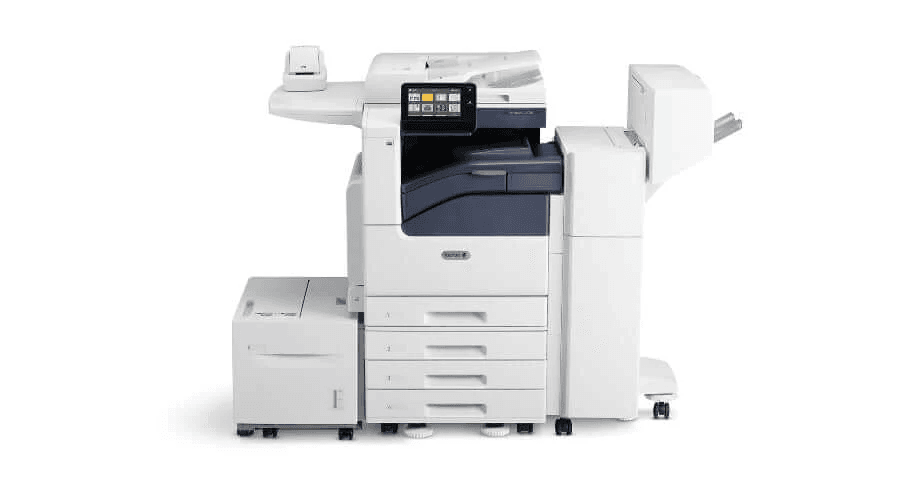
Xerox VersaLink C7025 Multifunction printer flaws could allow attackers to capture authentication credentials via pass-back attacks via LDAP and SMB/FTP services.
Rapid7 researchers discovered vulnerabilities in Xerox Versalink C7025 Multifunction printers (MFPs) that could allow attackers to capture authentication credentials via pass-back attacks via LDAP and SMB/FTP services.
The vulnerabilities are:
- CVE-2024-12511: SMB / FTP pass-back vulnerability
- CVE-2024-12510: LDAP pass-back vulnerability
The vulnerabilities impact Xerox Versalink MFPs and Firmware Version: 57.69.91 and earlier.
“While examining the Xerox Versalink C7025, Rapid7 found that the Versalink MFP device was vulnerable to a pass-back attack. This pass-back style attack leverages a vulnerability that allows a malicious actor to alter the MFP’s configuration and cause the MFP device to send authentication credentials back to the malicious actor.” reads the report published by Rapid7. “This style of attack can be used to capture authentication data for the following configured services: LDAP, SMB, FTP”
Below are the descriptions for the two vulnerabilities:
- Pass-back attack via LDAP CVE-2024-12510 (CVSS score: 6.7) – An attacker with access to the LDAP configuration page can change the LDAP server’s IP address to a rogue system, triggering an LDAP lookup that authenticates against their controlled host. By running a port listener, they can capture clear-text LDAP credentials. This attack requires access to the MFP printer admin account and an already configured LDAP service.

- Pass-back attack via user’s address book – SMB / FTP CVE-2024-12511 (CVSS score: 7.6) – An attacker can modify the user address book configuration to redirect SMB or FTP scans to a host they control, capturing authentication credentials. This allows them to intercept NetNTLMV2 handshakes for an SMB relay attack or obtain clear-text FTP credentials. The attack requires an SMB or FTP scan function to be set up and access to the printer console or web interface, potentially requiring admin privileges.
“If a malicious actor can successfully leverage these issues, it would allow them to capture credentials for Windows Active Directory.” concludes the report. “This means they could then move laterally within an organization’s environment and compromise other critical Windows servers and file systems.”
Organizations using Xerox VersaLink C7025 Multifunction printers should update to the latest firmware. If patching isn’t possible, they should set a strong admin password, avoid using high-privilege Windows accounts for LDAP or SMB, and disable unauthenticated remote access.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, newsletter)