
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

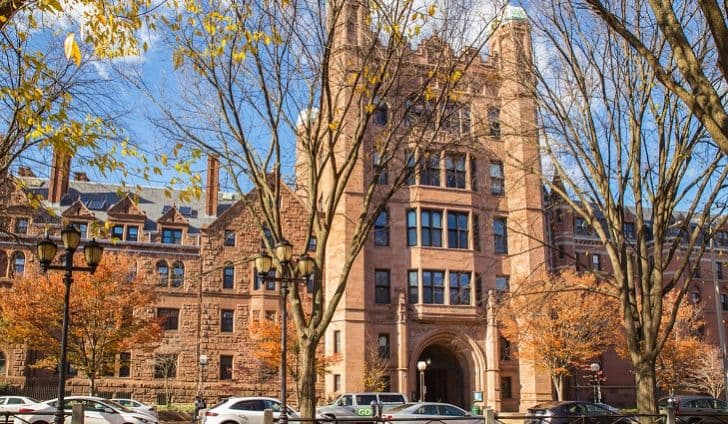
Ten years ago someone breached into a server of the Yale University

Ten years ago someone breached into a server of the Yale University, but because the intrusion happened nearly ten years ago there is much more information about how it occurred. After ten years, Yale University revealed a security breach that exposed an archive containing personal information of 119,000 people. Hackers breached into the database of the famous […]

yale university

Ten years ago someone breached into a server of the Yale University, but because the intrusion happened nearly ten years ago there is much more information about how it occurred.

After ten years, Yale University revealed a security breach that exposed an archive containing personal information of 119,000 people.

Hackers breached into the database of the famous University between April 2008 and January 2009 and apparently accessed a server where it is hosted a single database.

“On July 26th and 27th, Yale mailed notices to members of the Yale community, including alumni/ae, faculty members, and staff members, who were affected by a data intrusion that occurred in 2008-2009.” reads the security alert published by the Yale University.

yale university

The database contained data of individuals affiliated with the university, the unauthorized access was discovered on June 16, 2018, during a security review.

The hackers accessed names, Social Security numbers, dates of birth, Yale email addresses, and in some cases the physical addresses of individuals associated with the university.

Unfortunately, there is no way to understand how attackers hacked the server either “it is not feasible to determine the identities of the perpetrators.”

The academic institution announced that no financial information was exposed, it sent a notice letter to 97% of affected people in the Yale community.

Unfortunately, there is another disconcerting news for the Yale community, a letter sent by the University to the State of New Hampshire Attorney General, revealed that the same server was hacked a second time between March 2016 and June 2018.

This second intrusion caused the exposure of the names and Social Security numbers of 33 individuals, none of whom reside in New Hampshire.

Yale is offering identity monitoring services to all affected U.S. residents through the Kroll security firm. At the time there is no indication that the exposed data has been misused.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Yale University, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


