
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Yomi Hunter Joined the VirusTotal Sandbox Program!

We are pleased to announce that Yomi the Malware Hunter has successfully completed the on-boarding in the VirusTotal MultiSandbox Program! Official VirusTotal Announce: https://blog.virustotal.com/2019/05/virustotal-multisandbox-yoroi-yomi.html Yoroi can now contribute to the fight against malware threats sharing its analysis with Chronicle Security, the Alphabet’s subsidiary author of the notorious VirusTotal Threat Intelligence platform: one of the most widely used community platforms all around the […]

Yomi Malware Hunter

We are pleased to announce that Yomi the Malware Hunter has successfully completed the on-boarding in the VirusTotal MultiSandbox Program!

Official VirusTotal Announce: https://blog.virustotal.com/2019/05/virustotal-multisandbox-yoroi-yomi.html

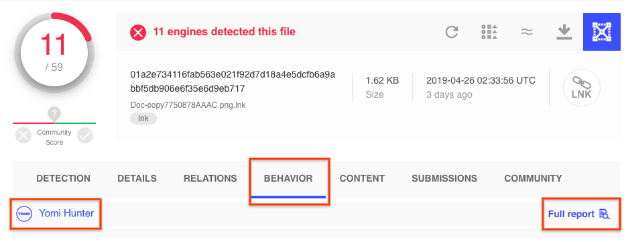
Yoroi can now contribute to the fight against malware threats sharing its analysis with Chronicle Security, the Alphabet’s subsidiary author of the notorious VirusTotal Threat Intelligence platform: one of the most widely used community platforms all around the world. The Yomi analysis reports will be available on the “Behavior tab” of the VirusTotal analysis page.

Yomi Malware Hunter

By clicking the “Full report”, every VT community user can now access the analysis report generated by the Yomi Sandbox, accessing fine grain details about malware execution, dropped files, https traffic, registry edits, spawned commands and system calls invocations. Including the MITRE ATT&CK™ matrix summarizing the key points of the malware attack.

Yomi Malware Hunter

If you want to try Yomi: The Malware Hunter please register here!

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Yomi, Virus Total)

[adrotate banner=”5″]

[adrotate banner=”13″]


