
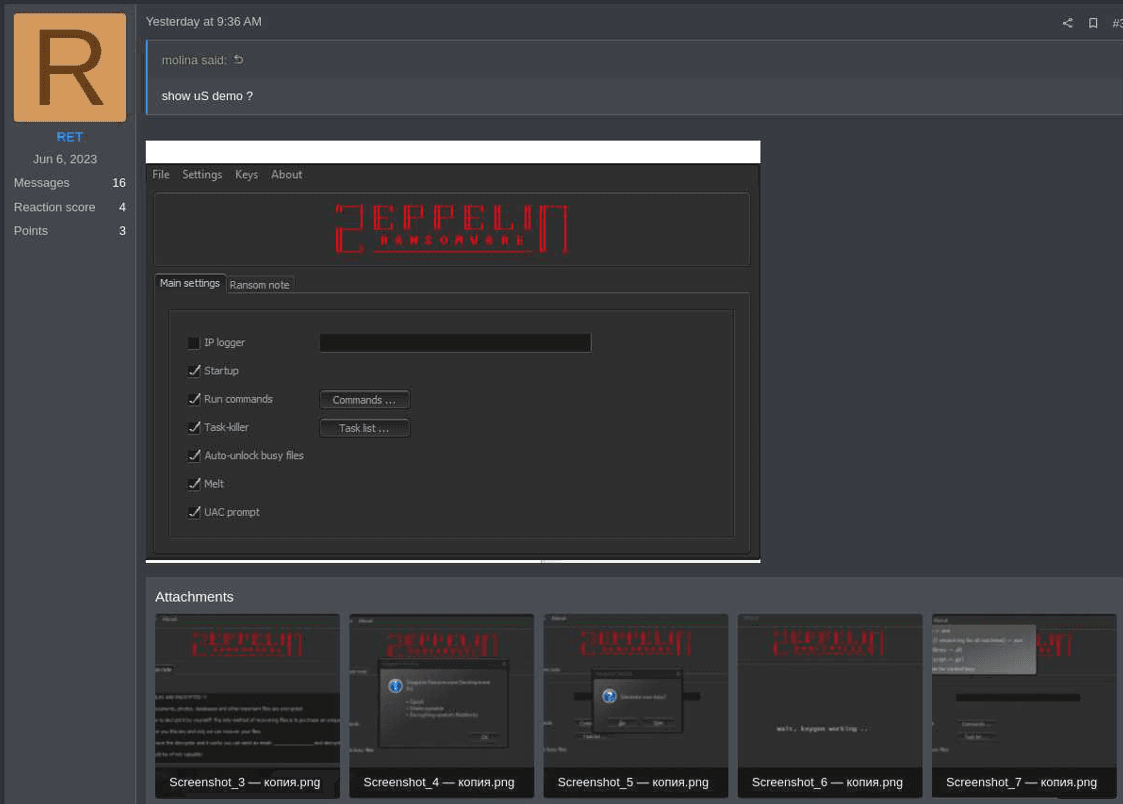
Screenshots of the builder (KELA) published by Bleeping Computer.
A threat actor announced the sale of the source code and a cracked version of the Zeppelin ransomware builder for $500.
Researchers from cybersecurity firm KELA reported that a threat actor announced on a cybercrime forum the sale of the source code and a cracked version of the Zeppelin ransomware builder for $500.
The seller clarified that it has sold the package to a single buyer and will not sell it to other clients.
The news was reported by Bleeping Computer which also shared a series of screenshots as proof of the sale.
The threat actor that bought the source code can use it to create a new strain of ransomware and launch a new ransomware operation.

The seller, who goes online with moniker RET, explained that it wasn’t the author of the ransomware malware, it had acquired the package without a license and cracked the builder version.
In August 222, the US Cybersecurity and Infrastructure Security Agency (CISA) and the Federal Bureau of Investigation (FBI) published a joint advisory to warn of Zeppelin ransomware attacks.
The Zeppelin ransomware first appeared on the threat landscape in November 2019 when experts from BlackBerry Cylance found a new variant of the Vega RaaS, dubbed Zeppelin.
The ransomware was involved in attacks aimed at technology and healthcare, defense contractors, educational institutions, manufacturers, companies across Europe, the United States, and Canada. At the time of its discovery, Zeppelin was distributed through watering hole attacks in which the PowerShell payloads were hosted on the Pastebin website.
Before deploying the Zeppelin ransomware, threat actors spend a couple of weeks mapping or enumerating the victim network to determine where data of interest is stored. The ransomware can be deployed as a .dll or .exe file or contained within a PowerShell loader.
Zeppelin actors request ransom payments in Bitcoin, they range from several thousand dollars to over a million dollars.
The group uses multiple attack vectors to gain access to victim networks, including RDP exploitation, SonicWall firewall vulnerabilities exploitation, and phishing attacks.
The threat actors also implement a double extortion model, threatening to leak stolen files in case the victims refuse to pay the ransom.
Zeppelin is typically deployed as a .dll or .exe file within a PowerShell loader. To each encrypted file, it appends a randomized nine-digit hexadecimal number as an extension. A ransom note is dropped on the compromised systems, usually on the desktop.
“The FBI has observed instances where Zeppelin actors executed their malware multiple times within a victim’s network, resulting in the creation of different IDs or file extensions, for each instance of an attack; this results in the victim needing several unique decryption keys.” reads the joint advisory.
In November 2022, law enforcement and private cybersecurity firms discovered some flaws in the encryption scheme of the malware that allowed them to release a decryptor working for files that were encrypted with versions since 2020.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ransomware)


