
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

ZeroFont phishing attack can bypass Office 365 protections

ZeroFont phishing attack – Crooks are using a new technique that involves manipulating font sizes to bypass Office 365 protections. According to cloud security firm Avanan, one of the detection mechanisms in Office 365 involves natural language processing to identify the content of the messages typically used in malicious emails. For example, an email including […]

Subway UK

ZeroFont phishing attack – Crooks are using a new technique that involves manipulating font sizes to bypass Office 365 protections.

According to cloud security firm Avanan, one of the detection mechanisms in Office 365 involves natural language processing to identify the content of the messages typically used in malicious emails.

For example, an email including the words “Apple” or “Microsoft” that are not sent from legitimate domains, or messages referencing user accounts, password resets or financial requests are flagged as malicious.

Experts from Avanan discovered phishing campaigns using emails in which some of the content is set to be displayed with zero-size font using <span style=”FONT-SIZE: 0px”>, for this reason, they dubbed the technique ZeroFont.

“Recently, we have been seeing a number of phishing attacks using a simple strategy to get their blatant email spoofs past Microsoft’s phishing scans. The tactic, which we are calling ZeroFont, involves inserting hidden words with a font size of zero that are invisible to the recipient in order to fool Microsoft’s natural language processing.” reads the analysis published by Avanan.

The email appears to the recipient as normal, but Microsoft’s filters are able to analyze also the text having a font size of “0”.

phishing zerofont

Summarizing, while the user sees a classic phishing content like this:
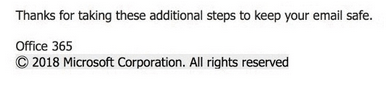
phishing zerofont

Microsoft’s filter will see the overall text including words written with “FONT-SIZE: 0px” attribute. This text, of course, doesn’t appear as a malicious content:
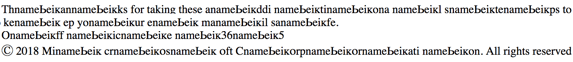
phishing zerofont


“Microsoft can not identify this as a spoofing email because it cannot see the word ‘Microsoft’ in the un-emulated version. Essentially, the ZeroFont attack makes it possible to display one message to the anti-phishing filters and another to the end user,” Avanan’s Yoav Nathaniel said in a blog post.

Natural language processing is essential to prevent phishing attacks, but a technique like ZeroFont demonstrated that attackers can bypass filters with a trick.

In the past, other techniques were devised to bypass anti-phishing filters, for example,  the Punycode phishing attack, the baseStriker phishing attack, the Unicode phishing attack, and the Hexadecimal Escape Characters phishing attack.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – ZeroFont phishing attack, cybercrime)

[adrotate banner=”5″]

[adrotate banner=”13″]


