Security Affairs
Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emsisoft releases a second decryptor in a few days, this time for ZeroFucks ransomware

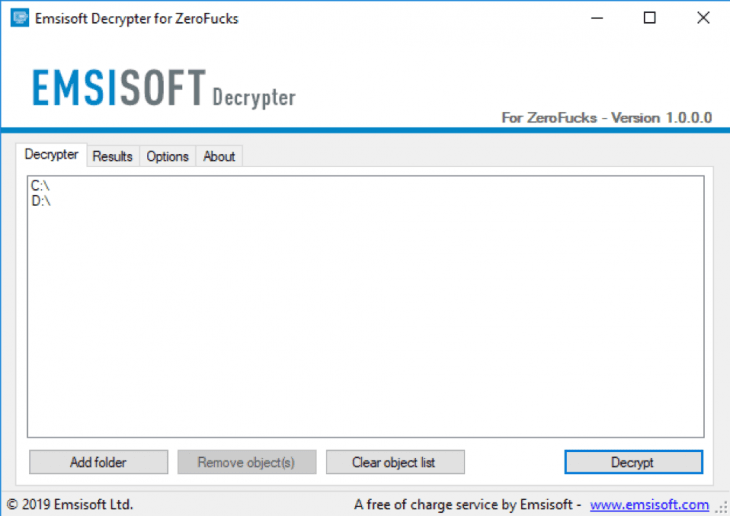
Security experts at Emsisoft released a second decryptor in a few days, this time announced a free decryptor for the ZeroFucks ransomware. A few days ago, the experts at Emsisoft released a free decryptor for the Ims00rry ransomware, now the malware team announced the released of a decryptor for the ZeroFucks ransomware. Victims of the […]

Fucks ransomware

Security experts at Emsisoft released a second decryptor in a few days, this time announced a free decryptor for the ZeroFucks ransomware.

A few days ago, the experts at Emsisoft released a free decryptor for the Ims00rry ransomware, now the malware team announced the released of a decryptor for the ZeroFucks ransomware.

Victims of the ZeroFucks ransomware don’t have to pay the ransom, they only need to download the decryptor form the link below:

Fucks ransomware

ZeroFucks ransomware encrypts files with AES-256 and replaces the extension in the filename with “.zerofucks” (i.e. “myphoto.jpg” is changed to “ myphoto.zerofucks”.

When the ransomware encrypts files the following GUI is displayed to the victims, crooks demand a €400 ransom worth of Bitcoins.

Fucks ransomware 2

Below the ransom note left on the infected systems by the ransomware:

“All your important files have been encrypted. If you want your files back, you need to pay €400 in Bitcoins. After the payment is received, we will give you access to unlock your files. Click on the Payment button to get more info.” reads ransom note.

“If you don’t pay within 48 hours, the price will be doubled. After another 24 hours, the price will be doubled again. If you don’t pay within 96 hours your files will be destroyed.”

Enjoy it!

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – ZeroFucks, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]