
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Malware

Detected new Zeus variant which makes use of steganography

Security experts at Malwarebytes detected a new of the popular Zeus banking trojan variant which makes use of steganography to hide the configuration file. The immortal Zeus malware strikes again, researchers at Malwarebytes have found a new variant of the banking trojan. The new variant of Zeus is using the steganography to disguise the configuration code […]

Detected new Zeus variant which makes use of steganography

Security experts at Malwarebytes detected a new of the popular Zeus banking trojan variant which makes use of steganography to hide the configuration file.

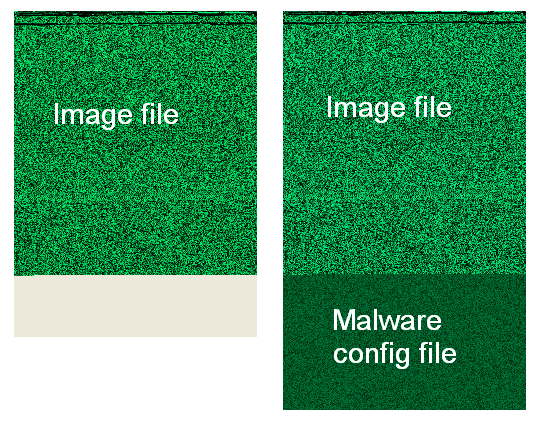
The immortal Zeus malware strikes again, researchers at Malwarebytes have found a new variant of the banking trojan. The new variant of Zeus is using the steganography to disguise the configuration code in a digital photo. Zeus is known as one of the most effective tools, the public release of its source code permitted to many criminal groups to customize its behavior and to develop new features, including the possibility to hide the C&C server inside the Tor network. The variant detected by Malwarebytes, dubbed  Zeus VM, downloads a configuration file that contains the list of banks targeted by the malware, the malicious code is able to steal online banking details, hijacking login details to the attackers and mask the transfers of money to a bank account managed by criminals. As explained by Jerome Segura the use of steganography was first noted by noted by a French security researcher who uses the nickname Xylitol

“A new variant of this trojan, dubbed ZeusVM, is using images as a decoy to retrieve its configuration file, a vital piece for its proper operation. French security researcher Xylitol noted something strange in one of the malvertising campaigns I reported a couple weeks ago.The malware was retrieving a JPG image hosted on the same server as were other malware components. ” Segura wrote.

The use of steganography is not new, malware authors adopt it to avoid security defense systems embedding code in a file format that appears legitimate.

“Hiding malevolent code in such a way can successfully bypass signature-based Intrusion Detection Systems or even antivirus software. From a webmaster point of view, images (especially ones that can be viewed) would appear harmless.” Segura added.

The researchers discovered that the image used by the Zeus variant is much larger of the original image found with a simple research made with Google because cybercriminals added additional data encrypted using Base64 encoding and then RC4 and XOR encryption algorithms.

steganograpgy Zeus malware

  Using an hexadecimal viewer it is possible to detect the malicious code added to the picture.

steganograpgy Zeus malware hex

Once decrypted the above text it is possible to observe that ZeusVM targeted popular financial institutions including Barclays, Deutsche Bank and Wells Fargo.

Pierluigi Paganini

(Security Affairs –  Zeus VM, steganography)


