
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Zimbra 10.1.20 patches multiple security issues, including a critical command injection bug

Zimbra patched nine flaws in version 10.1.20, including a critical SNMP monitoring command injection issue enabling arbitrary command execution. Zimbra released version 10.1.20 to fix nine security vulnerabilities, including a critical command injection flaw in the SNMP monitoring component. The vulnerability affects systems with SNMP notifications enabled and could allow attackers to execute arbitrary commands. […]

Zimbra CVE-2025-66376

Zimbra patched nine flaws in version 10.1.20, including a critical SNMP monitoring command injection issue enabling arbitrary command execution.

Zimbra released version 10.1.20 to fix nine security vulnerabilities, including a critical command injection flaw in the SNMP monitoring component.

The vulnerability affects systems with SNMP notifications enabled and could allow attackers to execute arbitrary commands. Users are urged to update to the latest version to mitigate potential exploitation risks.

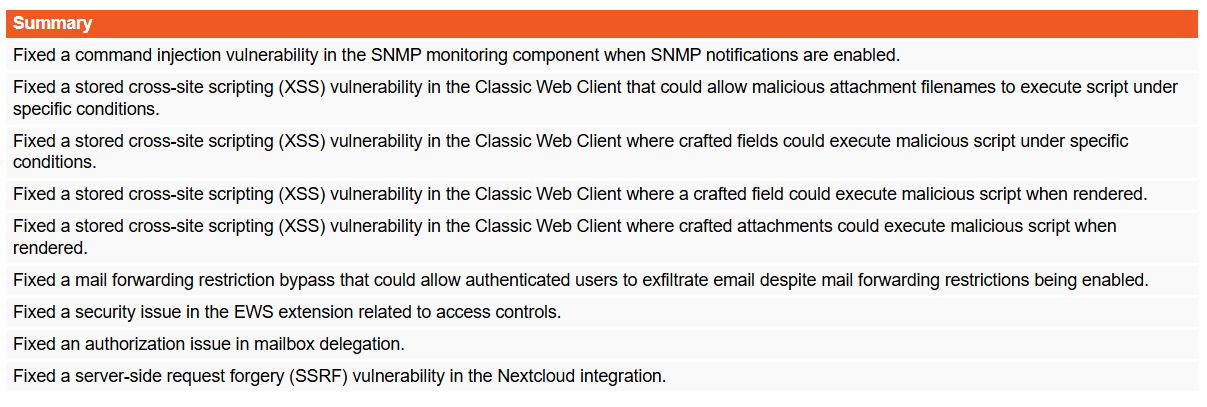
Other issues fixed in this release include multiple cross-site scripting (XSS) vulnerabilities affecting the Classic Web Client, which could allow attackers to execute malicious scripts through crafted attachment filenames, fields, or rendered content under specific conditions. The update also addresses a mail forwarding restriction bypass that could enable authenticated users to exfiltrate emails despite configured restrictions, as well as security issues involving access controls in the EWS extension, mailbox delegation authorization, and a server-side request forgery (SSRF) flaw in the Nextcloud integration.
In early July, Zimbra released version 10.1.19 to fix a critical stored XSS vulnerability in its Classic Web Client, which is widely used to access Zimbra Collaboration. The flaw can be exploited by sending specially crafted emails that execute malicious code when opened in the Classic UI.  Successful exploitation could allow attackers to access to mailbox information, session data, or account settings.

Google’s Threat Analysis Group discovered the vulnerability.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, command injection)


