A new powerful crimeware called ZingoStealer was released for free by a threat actor known as Haskers Gang.
ZingoStealer is a new information-stealer developed by a threat actor known as Haskers Gang who released it for free after they attempted to sell the source code for $500. The threat actors were also offering their own crypter, dubbed ExoCrypt for 300 Rubles (~$3 USD), to evade detection.
The cybercrime gang has been active since at least January 2020.
The crimeware allows operators to steal information from infected systems and abuse its resources to mine Monero. The malicious code is able to harvest system metadata and information stored by popular web browsers, including Google Chrome, Mozilla Firefox, Opera, and Opera GX.
The malware is also able to steal details from cryptocurrency wallets and load additional malware to conduct malicious operations.
“Cisco Talos recently observed a new information stealer, called “ZingoStealer” that has been released for free by a threat actor known as “Haskers Gang.”” reads the analysis published by Cisco Talos.
“It features the ability to steal sensitive information from victims and can download additional malware to infected systems. In many cases, this includes the RedLine Stealer and an XMRig-based cryptocurrency mining malware that is internally referred to as “ZingoMiner.””
ZingoStealer first appeared in the threat landscape in March 2022 and according to the Talos experts it is currently undergoing active development.
Following the initial analysis conducted by the experts, the Haskers Gang announced through its Telegram channel that the ownership of the ZingoStealer project is being transferred to a new threat actor.
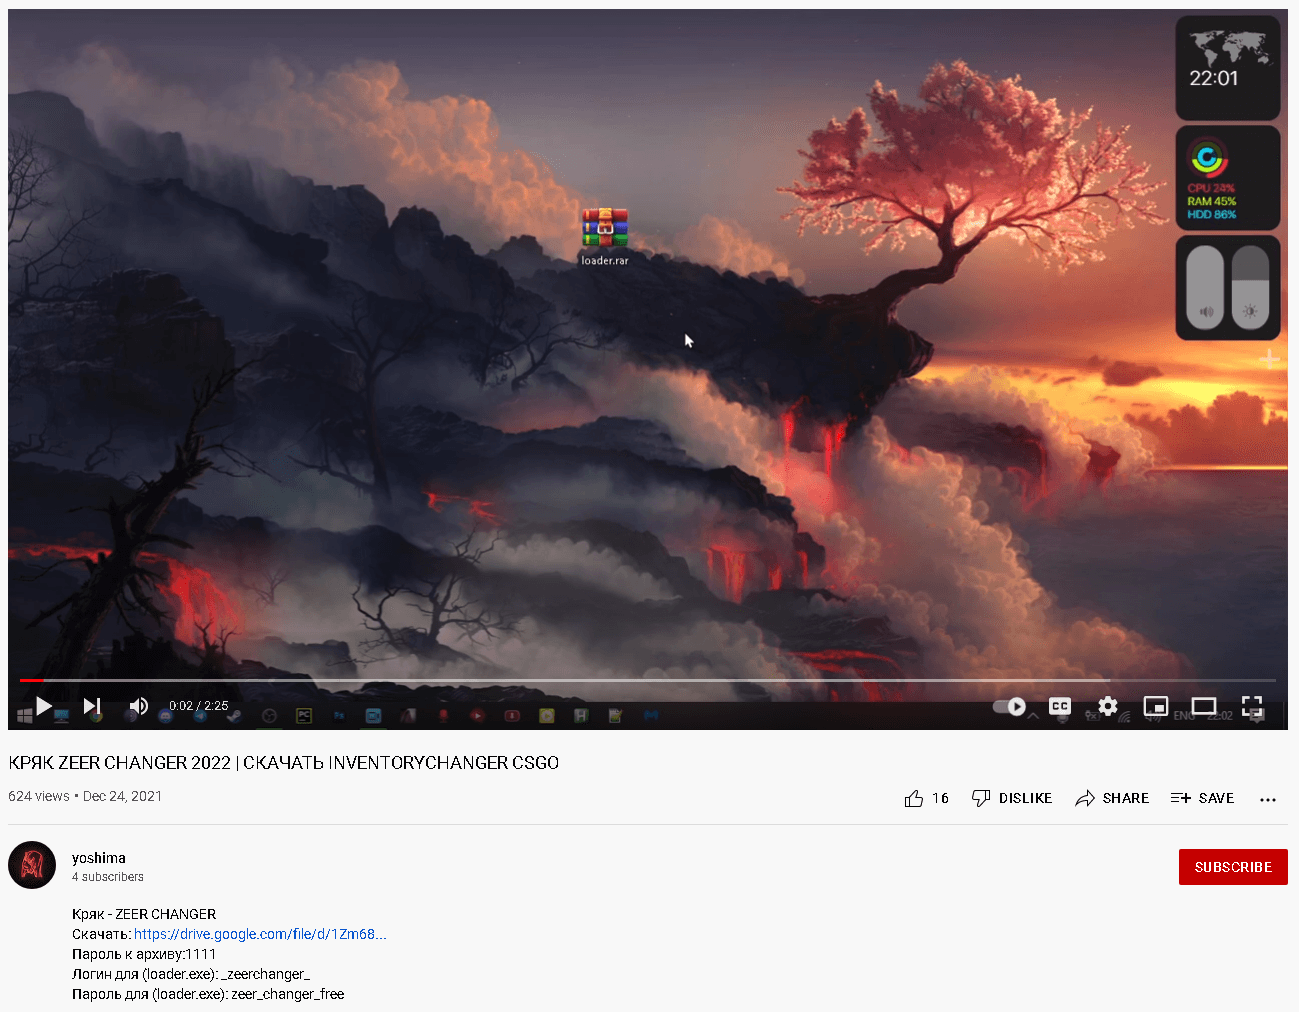
Talos researchers noticed a significant focus on infecting Russian-speaking victims, the threat is spreading under the guise of game cheats, key generators and pirated software, a circumstance that suggests it was developed to mainly target home users.
ZingoStealer uses Telegram chat features to exfiltrate data and distribute malware updates and components.
Experts said also to have observed the ZingoStealer executable being hosted on the Discord CDN, a circumstance that suggests threat actors are also distributing the malware within gaming-related Discord servers under the guise of video game cheats.
“While the malware is new, Cisco Talos has observed that it is undergoing consistent development and improvement and that the volume of new samples being observed in the wild continues to increase as more threat actors attempt to leverage it for nefarious purposes.” concludes the experts. “Users should be aware of the threats posed by these types of applications and should ensure that they are only executing applications distributed via legitimate mechanisms.”
Please vote for Security Affairs as the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog” and others of your choice.
To nominate, please visit: https://docs.google.com/forms/d/e/1FAIpQLSfxxrxICiMZ9QM9iiPuMQIC-IoM-NpQMOsFZnJXrBQRYJGCOw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, cybercrime)
[adrotate banner=”5″]
[adrotate banner=”13″]