
Security Affairs
QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|QNAP Warns Users as Plex2Shell Flaws Are Used to Hack NAS Devices|CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers|Fake GitHub Security Tools Infect Over 2,000 PCs With Malware|The BBC has a plan for a Black Sky event, and it runs on FM radio|Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly|SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7|SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122|Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION|Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Attackers actively exploit a critical zero-day in Zyxel CPE Series devices

Experts warn that threat actors are actively exploiting critical zero-day vulnerability, tracked as CVE-2024-40891, in Zyxel CPE Series devices. GreyNoise researchers are observing active exploitation attempts targeting a zero-day, tracked as CVE-2024-40891, in Zyxel CPE Series devices. The vulnerability is a command injection issue that remains unpatched and has not yet been publicly disclosed. Attackers can exploit […]

CVE-2024-40891 Zyxel CPE Series devices.

Experts warn that threat actors are actively exploiting critical zero-day vulnerability, tracked as CVE-2024-40891, in Zyxel CPE Series devices.

GreyNoise researchers are observing active exploitation attempts targeting a zero-day, tracked as CVE-2024-40891, in Zyxel CPE Series devices.

The vulnerability is a command injection issue that remains unpatched and has not yet been publicly disclosed. Attackers can exploit this flaw to execute arbitrary commands on affected devices, potentially resulting in device takeover, data exfiltration, or network infiltration.

“CVE-2024-40891 is very similar to CVE-2024-40890 (observed authentication attempts, observed command injection attempts), with the main difference being that the former is telnet-based while the latter is HTTP-based.” reads the advisory published by GreyNoise. “Both vulnerabilities allow unauthenticated attackers to execute arbitrary commands using service accounts (supervisor and/or zyuser).”

VulnCheck disclosed the Zyxel CPE Telnet command injection flaw CVE-2024-40891 on August 1, 2024, but the vendor has yet to publish an advisory. GreyNoise researchers collaborated with VulnCheck to verify the detection and created a tag for the issue on January 21, 2025. Due to widespread attacks, the disclosure was made immediately without vendor coordination.

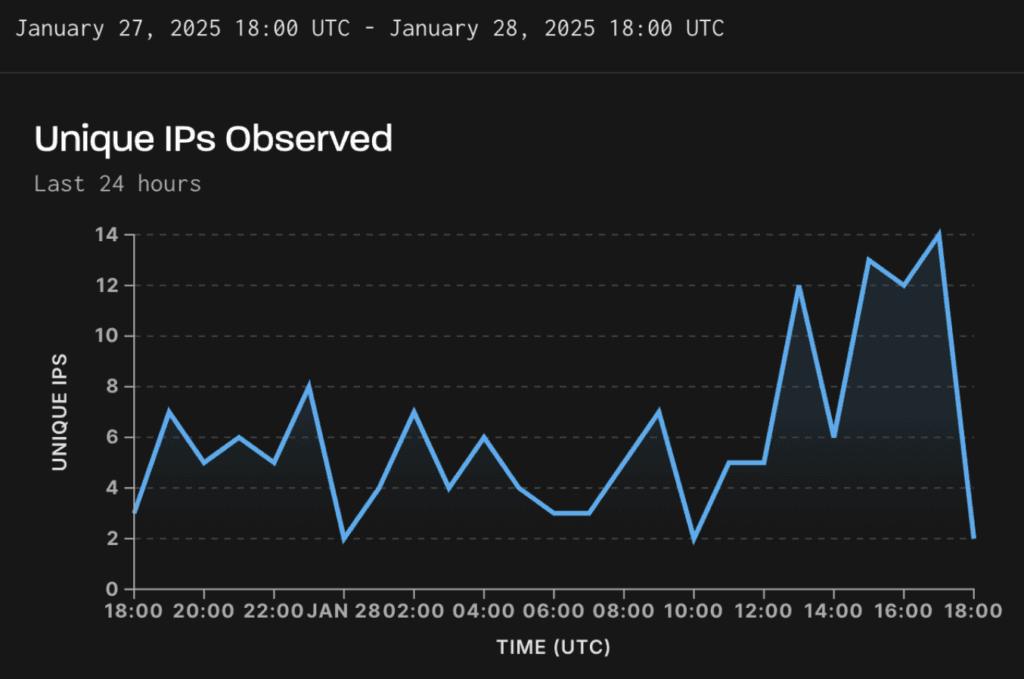
GreyNoise observed thousands of attack attempts originated from multiple IP addresses, most of them located in Taiwan. Cybersecurity firm Censys reported that more than 1,500 online devices are affected by the vulnerability.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CVE-2024-40891)


