A security flaw at DavaIndia Pharmacy exposed customer data and gave outsiders full admin control of its systems.
DavaIndia is a large Indian pharmacy retail chain focused on selling affordable generic medicines. Operated by Zota Health Care Ltd., the brand promotes low-cost alternatives to branded drugs to make healthcare more accessible across India.
DavaIndia runs hundreds of franchised stores nationwide and positions itself as a value-driven pharmacy network, offering prescription medicines, over-the-counter products, and wellness items at discounted prices. Its business model centers on reducing medicine costs while expanding access in both urban and semi-urban areas.
A security vulnerability at DavaIndia Pharmacy allowed unauthorized access to its platform, exposing customer order data and granting full administrative control. The weakness also put sensitive drug-control functions at risk, raising serious concerns about data protection and the integrity of its internal systems.
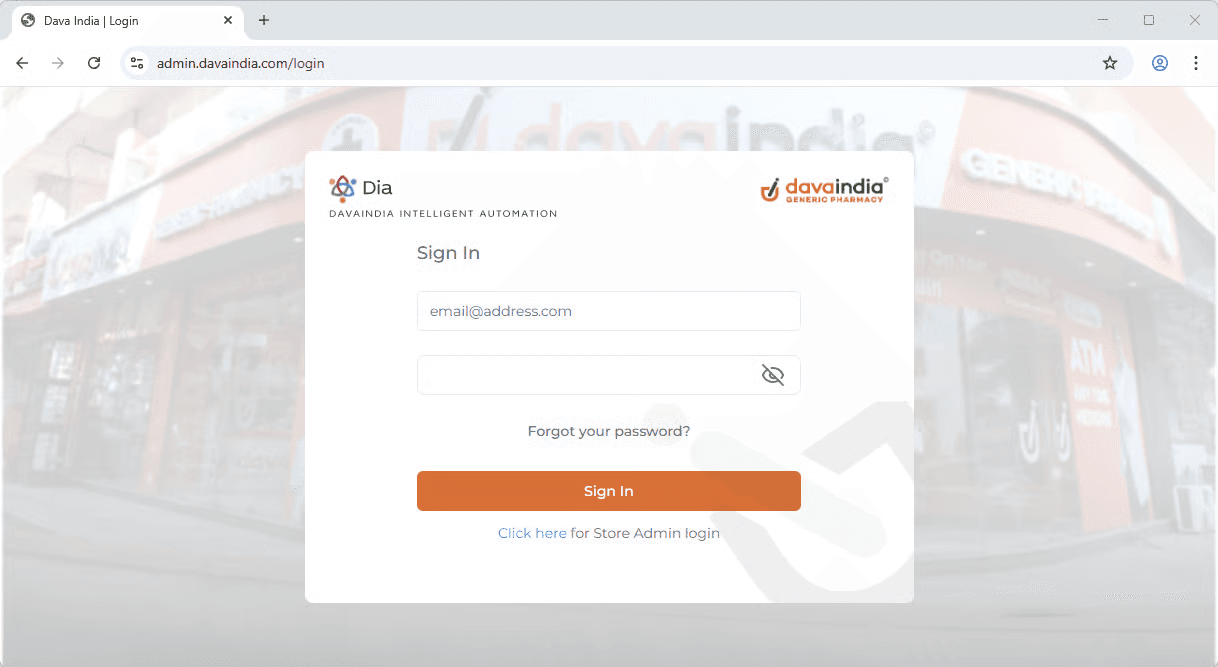
The security researcher Eaton Zveare disclosed serious flaws in DavaIndia. While analyzing its website, the researcher found an exposed admin subdomain that allowed unauthenticated access to super-admin APIs.

“The site is developed using Next.js, so naturally there’s plenty of client-side JS to pick through. One part that stood out immediately was the forgot password code that mentioned super-admin APIs” wrote the expert. “As a test, I went to the endpoint in the browser and was presented with the list of super admin users! All without authenticating.”
By crafting a POST request, he was able to create a new super admin account and gain full control of the platform.
With this access, it was possible to view and edit stores, pharmacist details, customer orders, personal data, products, inventory, and coupons. The researcher even generated a 100% discount coupon and demonstrated how prescription requirements could potentially be bypassed, highlighting major risks to customer privacy and drug controls.
“Some items require a prescription to purchase. This is controlled by a toggle” continues the expert. “If you wanted to buy something that would require a prescription, you could in theory toggle this off and then submit your order. This was not tested, but it is highly likely it would have worked.”
An exposed admin panel included a “Sponsor Settings” feature that allowed control over homepage videos, meaning an attacker could have swapped content, even pulling off a Rick Roll prank. The flaw was reported on August 20, 2025, and fixed within a month, though confirmation was delayed. With support from CERT-In, the case was finally confirmed closed on November 28, 2025, and publicly disclosed on February 13, 2026.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, DavaIndia Pharmacy)