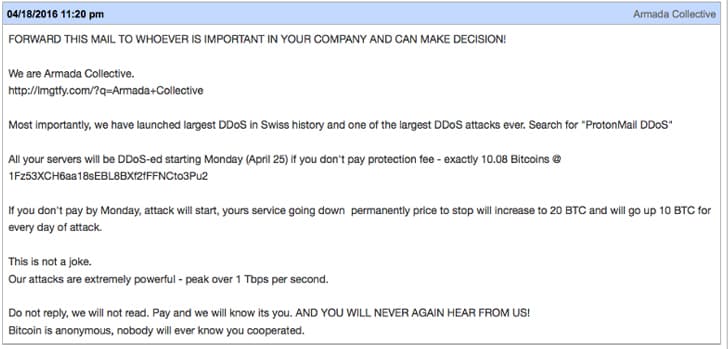
Businesses have already paid more than $100,000 to DDoS extortionists who claim to be the dreaded Armada Collective, but that never DDoS anyone.
A criminal organization made $100,000 from a number of businesses across the globe my threatening them of distributed denial-of-service (DDoS) attack. The criminals requested to the victims the payment of a ransomware to avoid being targeted by powerful DDoS, the worrying aspect of the story is that they is that they never launched a single attack.
The extortion is a consolidated practice in the criminal ecosystem, groups like DD4BC used a consolidated scheme to convince victims to pay the ransomware. Typically attackers launch a demonstrative attack that temporarily shut down the victim’s website then the crooks send a message to the victims requesting the payment of the ransom.
In September 2015, Akamai published samples of the extortion emails sent by the DD4BC group to the victims demanding ransom ranging from 25 Bitcoins to 50 Bitcoins ($6,000 and $12,000 at current currency exchange rates).
“Your site is going under attack unless you pay 25 Bitcoin,” one email stated. “Please note that it will not be easy to mitigate our attack, because our current UDP flood power is 400-500 Gbps, so don’t even bother.”
The attackers promise never to threaten the victim twice if they will pay the ransom. In the case victims ignore the first message they will receive a subsequent email to warn them against ignoring the ransom demand.
“And you are ignoring us. Probably because you don’t want to pay extortionists. And you believe that after sometime we will give up. But we never give up,” the follow-up messages read.
Back to the present, a group called Armada Collective is threatening companies worldwide, the crew is the same that shut down the popular encrypted mail service ProtonMail in November 2015 and extorted $6,000 to stop a prolonged DDoS attack that knocked it offline.
A hundred companies have received emails from the alleged members of Armada Collective demanding as much as $23,000 in Bitcoins in exchange for not being attacked.
A number of members of the Armada Collective were arrested in January 2016, so many experts speculate that someone is abusing the reputation of the Armada Collective for profit, and it works!
“We heard from more than 100 existing and prospective CloudFlare customers who had received the Armada Collective’s emailed threats. We’ve also compared notes with other DDoS mitigation vendors with customers that had received similar threats.” states a blog post published by Cloudflare.
“Our conclusion was a bit of a surprise: we’ve been unable to find a single incident where the current incarnation of the Armada Collective has actually launched a DDoS attack. In fact, because the extortion emails reuse Bitcoin addresses, there’s no way the Armada Collective can tell who has paid and who has not. In spite of that, the cybercrooks have collected hundreds of thousands of dollars in extortion payments.”

At the time I was writing, no DDoS attack was launched by the criminal organizations against the victims.
[adrotate banner=”9″]
(Security Affairs – Armada Collective, DDoS attacks)