
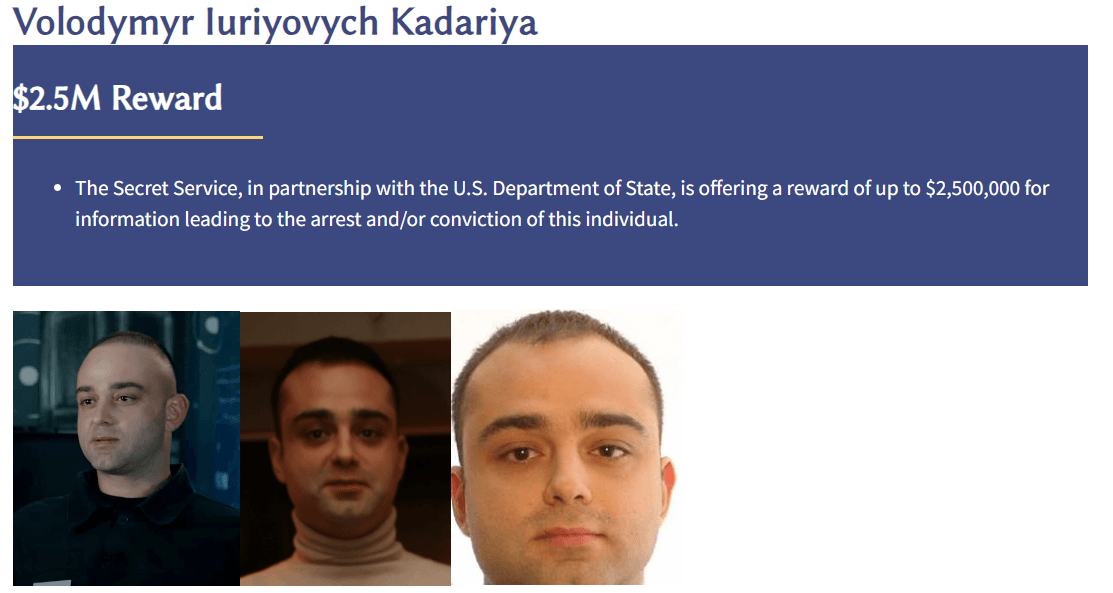
The US Department of State offers a $2.5 million reward for information leading to the arrest of a Belarusian cybercriminal involved in the mass malware distribution.
The US Department of State announced a $2.5 million reward for information leading to the arrest of Volodymyr Kadariya (38), a Belarusian national allegedly involved in a significant malware organization.

Kadariya has been indicted for distributing the Angler Exploit Kit and other malware to millions of victims. Along with co-defendants Maksim Silnikau and Andrei Tarasov, Kadariya is charged with wire fraud conspiracy and computer fraud conspiracy. The indictment alleges that from 2013 to 2022, Kadariya played a key role in distributing the Angler Exploit Kit, which was used to spread various malware, including ransomware, through malvertising and other methods.
“The U.S. Department of State is offering a reward of up to $2.5 million for information leading to the arrest and/or conviction in any country of Volodymyr Kadariya for his alleged participation in a significant malware organization.” reads the announcement published by US Department of State. “Kadariya is charged with cybercrime offenses associated with an alleged scheme to transmit the Angler Exploit Kit (AEK), other malware, and online scams to the computers of millions of unsuspecting victim Internet users through online advertisements – so-called “malvertising” – and other means from October 2013 through March 2022. At times during the scheme, the AEK was a leading vehicle through which cybercriminals delivered malware onto compromised electronic devices”
According to a notice published by the Secret Service, the malvertising campaigns appeared legitimate but redirected users to malicious sites, used to deliver malware to their devices.
“Kadariya and his co-conspirators also allegedly enabled the delivery of “scareware” ads that displayed false messages claiming to have identified a virus or other issue with a victim Internet user’s device. The messages then attempted to deceive the victim into buying or downloading dangerous software, providing remote access to the device, or disclosing personal identifying or financial information.” reads the notice. “Kadariya and his associates used multiple strategies to profit from their widespread hacking and wire fraud scheme, including by using accounts on predominantly Russian cybercrime forums to sell to cybercriminals access to the compromised devices of victim Internet users (so-called “loads” or “bots”), as well as information stolen from victims and recorded in “logs,” such as banking information and login credentials, to enable further efforts to defraud the victim Internet users or deliver additional malware to their devices.”
According to the indictment, Kadariya and his co-conspirators also sold access to the compromised systems to Russian cybercrime forums, and sold the banking and login information stolen from their infected systems.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware distribution)


