
Security researchers spotted a campaign that is employing a new stealthy malware tracked as BLISTER that targets windows systems.
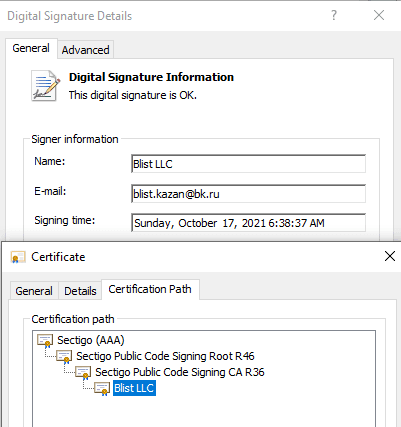
Elastic Security researchers uncovered a malware campaign that leverages a new malware and a stealthy loader tracked as BLISTER, that uses a valid code signing certificate issued by Sectigo to evade detection.
BLISTER loads second-stage payloads that are executed directly in the memory of the Windows system and maintain persistence. The malicious code has a low detection rate and implements multiple tricks to avoid detection.
“A valid code signing certificate is used to sign malware to help the attackers remain under the radar of the security community. We also discovered a novel malware loader used in the campaign, which we’ve named BLISTER. The majority of the malware samples observed have very low, or no, detections in VirusTotal.” “The infection vector and goals of the attackers remain unknown at this time.”

The certificate used to sign the loader code was issued by Sectigo for a company called Blist LLC, which has an email address from a Russian provider Mail.Ru.
The loader is embedded into legitimate libraries, such as colorui.dll, to avoid raising suspicion, it can be initially written to disk from simple dropper executables.
Upon execution, BLISTER decodes bootstrapping code stored in the resource section with a simple 4-byte XOR routine. The malware authors heavily obfuscated the bootstrapping code that initially sleeps for 10 minutes before executing in an attempt to evade sandbox analysis.
Then the loader decrypts the embedded malware payload, experts reported the use of CobaltStrike and BitRat as embedded payloads. The payload is loaded into the current process or injected into a newly pawned WerFault.exe process.
In order to achieve persistence, BLISTER copy itself to the C:\ProgramData folder and re-names a local copy of rundll32.exe. Then it creates a link to the current user’s Startup folder to launch the malware at logon as a child of explorer.exe.
Elastic’s researchers shared Yara rules for this campaign along with indicators of compromise.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


