
Cybersecurity researchers spotted a new malware-as-a-service (MaaS) called BunnyLoader that’s appeared in the threat landscape.
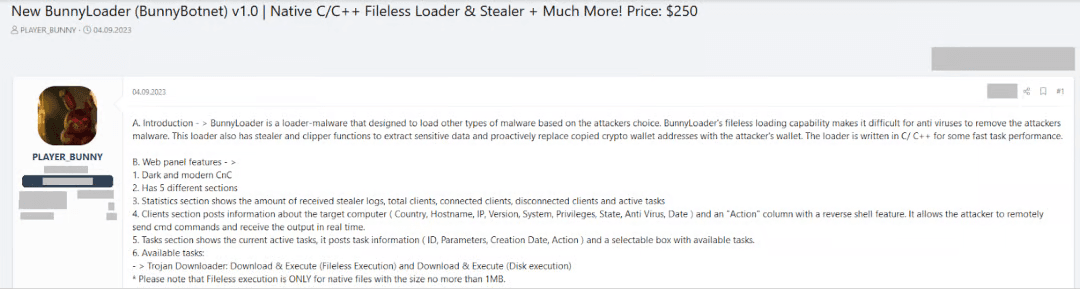
Zscaler ThreatLabz researchers discovered a new malware-as-a-service (MaaS) that is called BunnyLoader, which has been advertised for sale in multiple cybercrime forums since September 4, 2023.

The BunnyLoader malware loader is written in C/C++ and is sold on various forums for $250 for a lifetime license. The researchers believe that the BunnyLoader is under rapid development, the authors are releasing multiple updates to implement new features and fix bugs.
The malware also supports anti-sandbox techniques and evasion techniques, it can download and execute a second-stage payload, log keys, steal sensitive information and cryptocurrency, and execute remote commands.
“BunnyLoader provides various functionalities such as downloading and executing a second-stage payload, stealing browser credentials and system information, and much more.” reads the report published by Zscaler. “BunnyLoader employs a keylogger to log keystrokes as and a clipper to monitor the victim’s clipboard and replace cryptocurrency wallet addresses with actor-controlled cryptocurrency wallet addresses.”
The advertisement also states that BunnyLoader supports a fileless loader which allow the malware to download and execute further malware stages directly into the memory.
Stolen data are encapsulated into a ZIP archive and transmitted to a C2 server.
On September 15, 2023 the authors released BunnyLoader v1.7 and BunnyLoader v1.8 which implemented respectively additional AV evasion techniques and a keylogger functionality, fixed a bug in execution of tasks and in C2.
| BunnyLoader v1.7 | Sept 15, 2023 | Implemented additional AV evasion |
| BunnyLoader v1.8 | Sept 15, 2023 | Implemented keylogger functionalityBug fixes in execution of tasksFix C2 bugs |
On September 27, 2023, the authors fixed critical SQL injection vulnerabilities in command-and-control (C2) that would have allowed attackers to take over the C2 database.
The BunnyLoader panel supports multiple features such as:
- downloading and executing additional malware
- keylogging stealing credentials
- manipulating a victim’s clipboard to steal cryptocurrency
- running remote commands on the infected machine
- providing statistics for infections
- displaying the total connected/disconnected clients
- monitoring active tasks
- logging stealer’s activities

The researchers have yet to discover the distribution channel for malware, but they analyzed the activity of the malware upon execution.
Upon execution, the loader sets up persistence via a Windows Registry and performs a sequence of anti-VM techniques.
Then it sends the registration request to the C2 server and if the response from the C2 is “Connected”, BunnyLoader performs the core malicious actions.
The malware can download and execute next-stage malware, run keylogger and steal sensitive data, including web browser data and cryptocurrency wallets. The malware is also able to steal data from messaging apps and VPN clients.
“BunnyLoader is a new MaaS threat that is continuously evolving their tactics and adding new features to carry out successful campaigns against their targets.” continues the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, MaaS)


