
Threat actors behind the ChromeLoader malware campaign are using VHD files disguised as popular games, experts warn.
Researchers from Ahnlab Security Emergency Response Center (ASEC) recently uncovered a malware campaign distributing the ChromeLoader using VHD files.
ChromeLoader is a malicious Chrome browser extension, it is classified as a pervasive browser hijacker that modifies browser settings to redirect user traffic.
These VHD files are disguised as applications and hacks or cracks for popular Nintendo and Steam games, including ELDEN RING, Dark Souls 3, Red Dead Redemption 2, Call of Duty Deluxe Edition, Minecraft, The Legend of Zelda, Pokemon Ultra Moon, Animal Crossing New Horizons, Mario Kart 8 Deluxe, Microsoft Office 2010 and more.
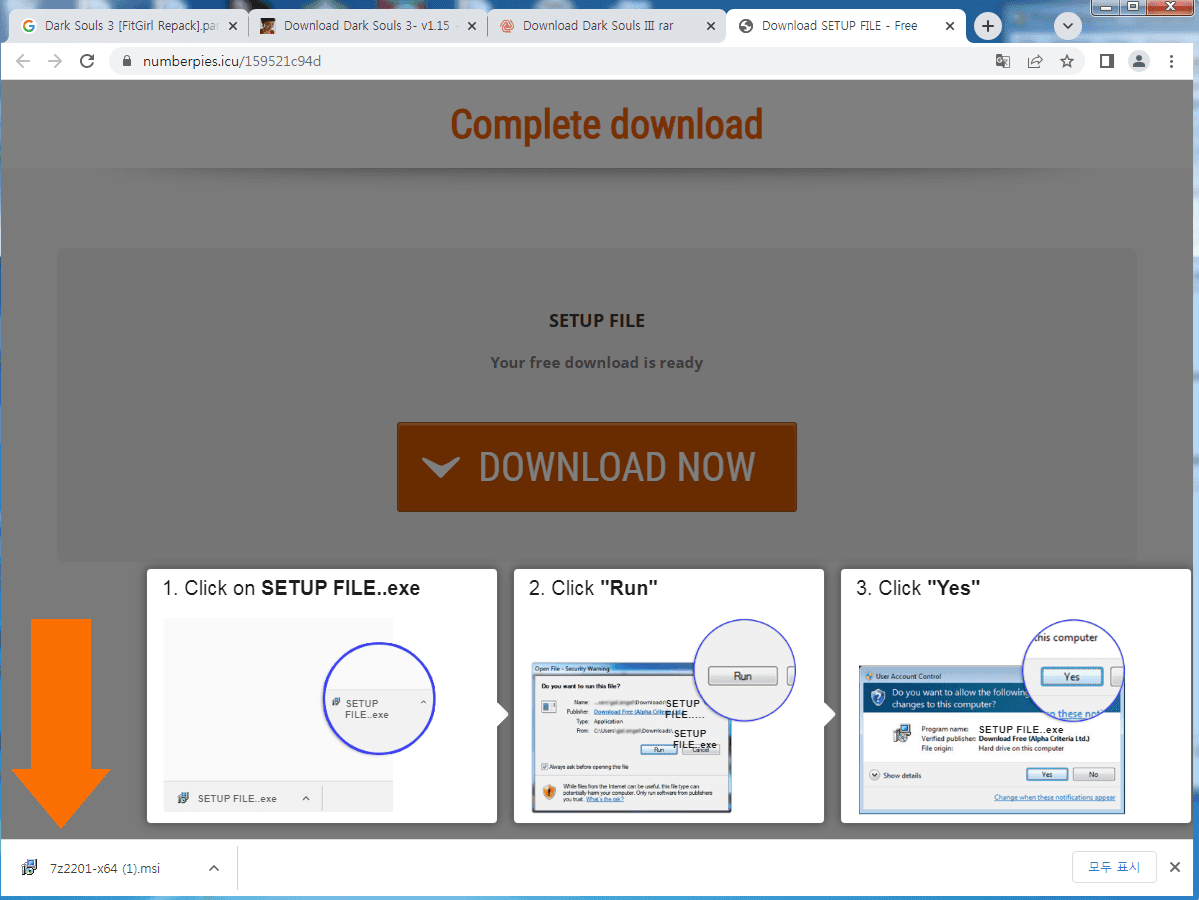
The experts discovered the files by querying Google for popular games and programs, they were distributed through multiple websites.

“Downloading an illegal program from any of these websites would cause multiple malicious advertisement websites to appear. The VHD files are assumed to have been downloaded from one of these advertisement websites.” reads the analysis published by ASEC.
Upon installing the malicious files, they will install the ChromeLoader extension.
The malicious extension redirects users to an advertisement website and collects browsing data and credentials.
The malware is able to redirect the user’s traffic and hijack user search queries to popular search engines, including Google, Yahoo, and Bing. The malicious code is also able to use PowerShell to inject itself into the browser and added the extension to the browser.
In May 2022, researchers from Red Canary observed a malvertising campaign spreading the ChromeLoader malware that hijacks the victims’ browsers.
In September 2022, VMware and Microsoft warned of an ongoing, widespread Chromeloader malware campaign that was dropping malicious browser extensions, node-WebKit malware, and ransomware.
The analysis of the VHD files revealed multiple hidden files except for the Install.lnk file.
Upon clicking on the Install.lnk, the properties.bat file and the properties.bat file are executed.
“Install.lnk runs the properties.bat file and the properties.bat file, in turn, decompresses the files.zip in the “%AppData%” path with a tar command. The files.zip file holds normal files and a malicious js file related to node-webkit(nw.js). node-webkit is a web application that uses Chromium and Node. It can be run through nw.exe and references data written in the package.json file.” continues the analysis.
Then the batch file executes “data.ini,” a VBScript, and a JavaScript that fetches the last-stage payload from a remote server.
The report includes indicators of compromise (IoCs) for the most recent ChromeLoader campaign.
“Recently, there has been an increase in malware using disk image files. Disguising malware as game hacks and crack programs is a method employed by many threat actors.” concludes the report. “Users must be particularly cautious about executing files downloaded from unknown sources, and it is advised that users download programs from their official websites. AhnLab’s anti-malware product, V3, detects and blocks the malware using the alias below.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)


