
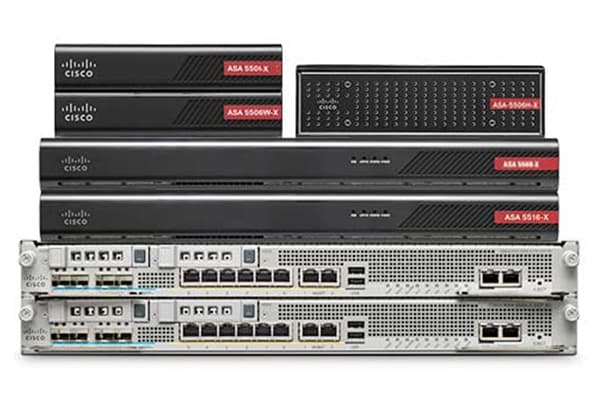
A flaw in the family of CISCO FirePower Firewall devices allows malware to bypass detection mechanism.
Cisco is releasing security updates to fix a critical vulnerability (CVE-2016-1345) that affects one of its newest products, the FirePower firewall. The flaw has been discovered by security researchers at Check Point Security.
According to the security advisory published by Cisco, an attacker can remotely exploit the flaw to allow malware bypass detection measured implemented by the FirePower firewall.
“A vulnerability in the malicious file detection and blocking features of Cisco Firepower System Software could allow an unauthenticated, remote attacker to bypass malware detection mechanisms on an affected system.” states the advisory.
The vulnerability is related the improper input validation of fields in HTTP headers. The attacker can remotely exploit the flaw by sending a specifically crafted HTTP request to a vulnerable system.
“A successful exploit could allow the attacker to bypass malicious file detection or blocking policies that are configured for the system, which could allow malware to pass through the system undetected.” continues the advisory.
Cisco ranked the vulnerability as “high severity” so it has promptly released the security updates that solve the issue in Cisco Firepower System Software 5.4.0.7 and later, 5.4.1.6 and later and 6.0.1 and later.
Cisco confirmed that systems Cisco Firepower System Software that has one or more file action policies configured and is running on any of the following Cisco products are vulnerable:
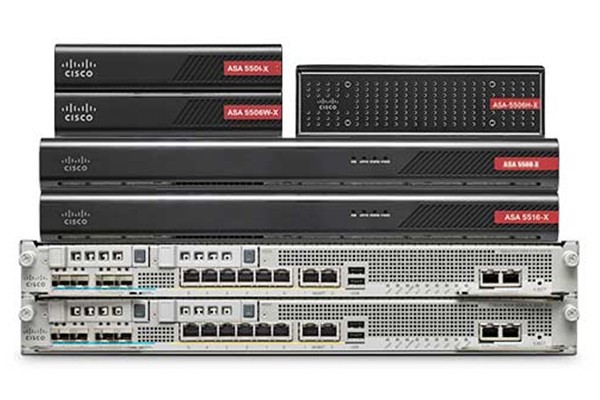
- Adaptive Security Appliance (ASA) 5500-X Series with FirePOWER Services
- Advanced Malware Protection (AMP) for Networks, 7000 Series Appliances
- Advanced Malware Protection (AMP) for Networks, 8000 Series Appliances
- FirePOWER 7000 Series Appliances
- FirePOWER 8000 Series Appliances
- FirePOWER Threat Defense for Integrated…
At the time I was writing there isn’t no news regarding systems compromised by exploiting the vulnerability. Impacted Cisco hardware
A simple way to discover if a system is affected by the vulnerability is to check Cisco configurations (Policies>Access Control>Malware and File), if the policy is set on “Block Files, Block Malware, or Detect Files” the system is vulnerable.
The vulnerability also impacts the versions 2.9.8.2 and later of the Snort open source network-based intrusion detection system, users can download the updates on its official website.
[adrotate banner=”9″]
(Security Affairs – Cisco FirePower firewall, hacking)


