Security Affairs
One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Coronavirus-themed attacks April 26 – May 02, 2020

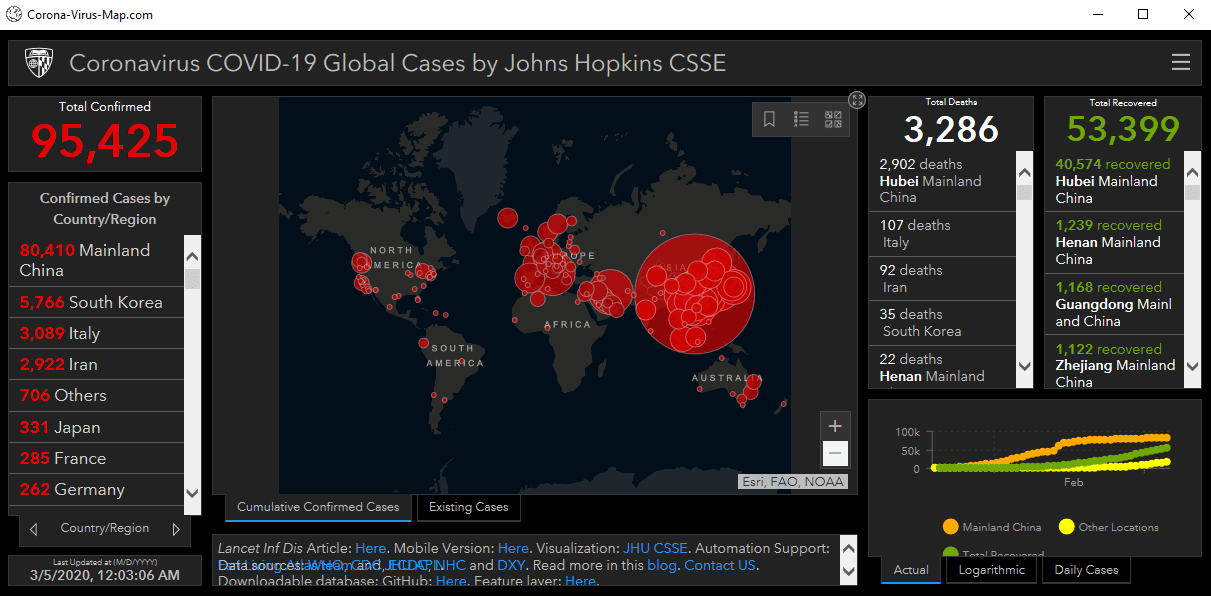
This post includes the details of the Coronavirus-themed attacks launched from April 26 to May 02, 2020. Please give me your vote for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERShttps://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform Threat actors exploit the interest in the Coronavirus outbreak while infections increase worldwide, experts are observing new campaigns on a daily bases. Below […]

Oxford University Lab

This post includes the details of the Coronavirus-themed attacks launched from April 26 to May 02, 2020.

Please give me your vote for European Cybersecurity Blogger Awards – VOTE FOR YOUR WINNERS
https://docs.google.com/forms/d/e/1FAIpQLSe8AkYMfAAwJ4JZzYRm8GfsJCDON8q83C9_wu5u10sNAt_CcA/viewform

Threat actors exploit the interest in the Coronavirus outbreak while infections increase worldwide, experts are observing new campaigns on a daily bases.

Below a list of attacks detected this week.

April 27 – Group-IB helps to detain operators of scam-service issuing fake passes to move around Moscow amid COVID-19 virus lockdown

Group-IB helped Russian Police in detaining the operators of a fraudulent online service, selling fake digital passes to move around Moscow amid COVID-19 lockdown.

April 28 – Experts warn of deliveries scams that use a COVID-19 theme

Kaspersky experts uncovered a new wave of phishing scams that use a COVID-19 theme and impersonate shipping carriers, including FedEx, UPS, and DHL.

April 30 – Crooks spread malware via pirated movies during COVID-19 outbreak

Microsoft warns of a spike in malware spreading via pirate streaming services and movie piracy sites during the COVID-19 pandemic.

April 30 – RDP brute-force attacks rocketed since beginning of COVID-19

The number of RDP brute-force attacks is skyrocketing in mid-March due to remote working imposed during the COVID-19 pandemic.

May 1 – COVID-19 disinformation and misinformation campaigns continue to proliferate

COVID-19 disinformation and misinformation campaigns continue to proliferate around the world, with potentially harmful consequences for society.

May 1 – Europol analyses on criminal operations in Europe during COVID-19 Crisis

Threat actors and criminal organizations continue to take advantage of the COVID-19 pandemic to make money, Europol warns.

May 2- TrickBot operators exploit COVID-19 as lures

IBM X-Force researchers spotted a new COVID-19-themed campaign spreading the infamous TrickBot trojan through fake messages.

If you are interested in COVID19-themed attacks from February 1 give a look at the following posts:

https://securityaffairs.co/wordpress/102301/cyber-crime/coronavirus-themed-attacks-april-19-april-25-2020.html

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – COVID-19, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]