
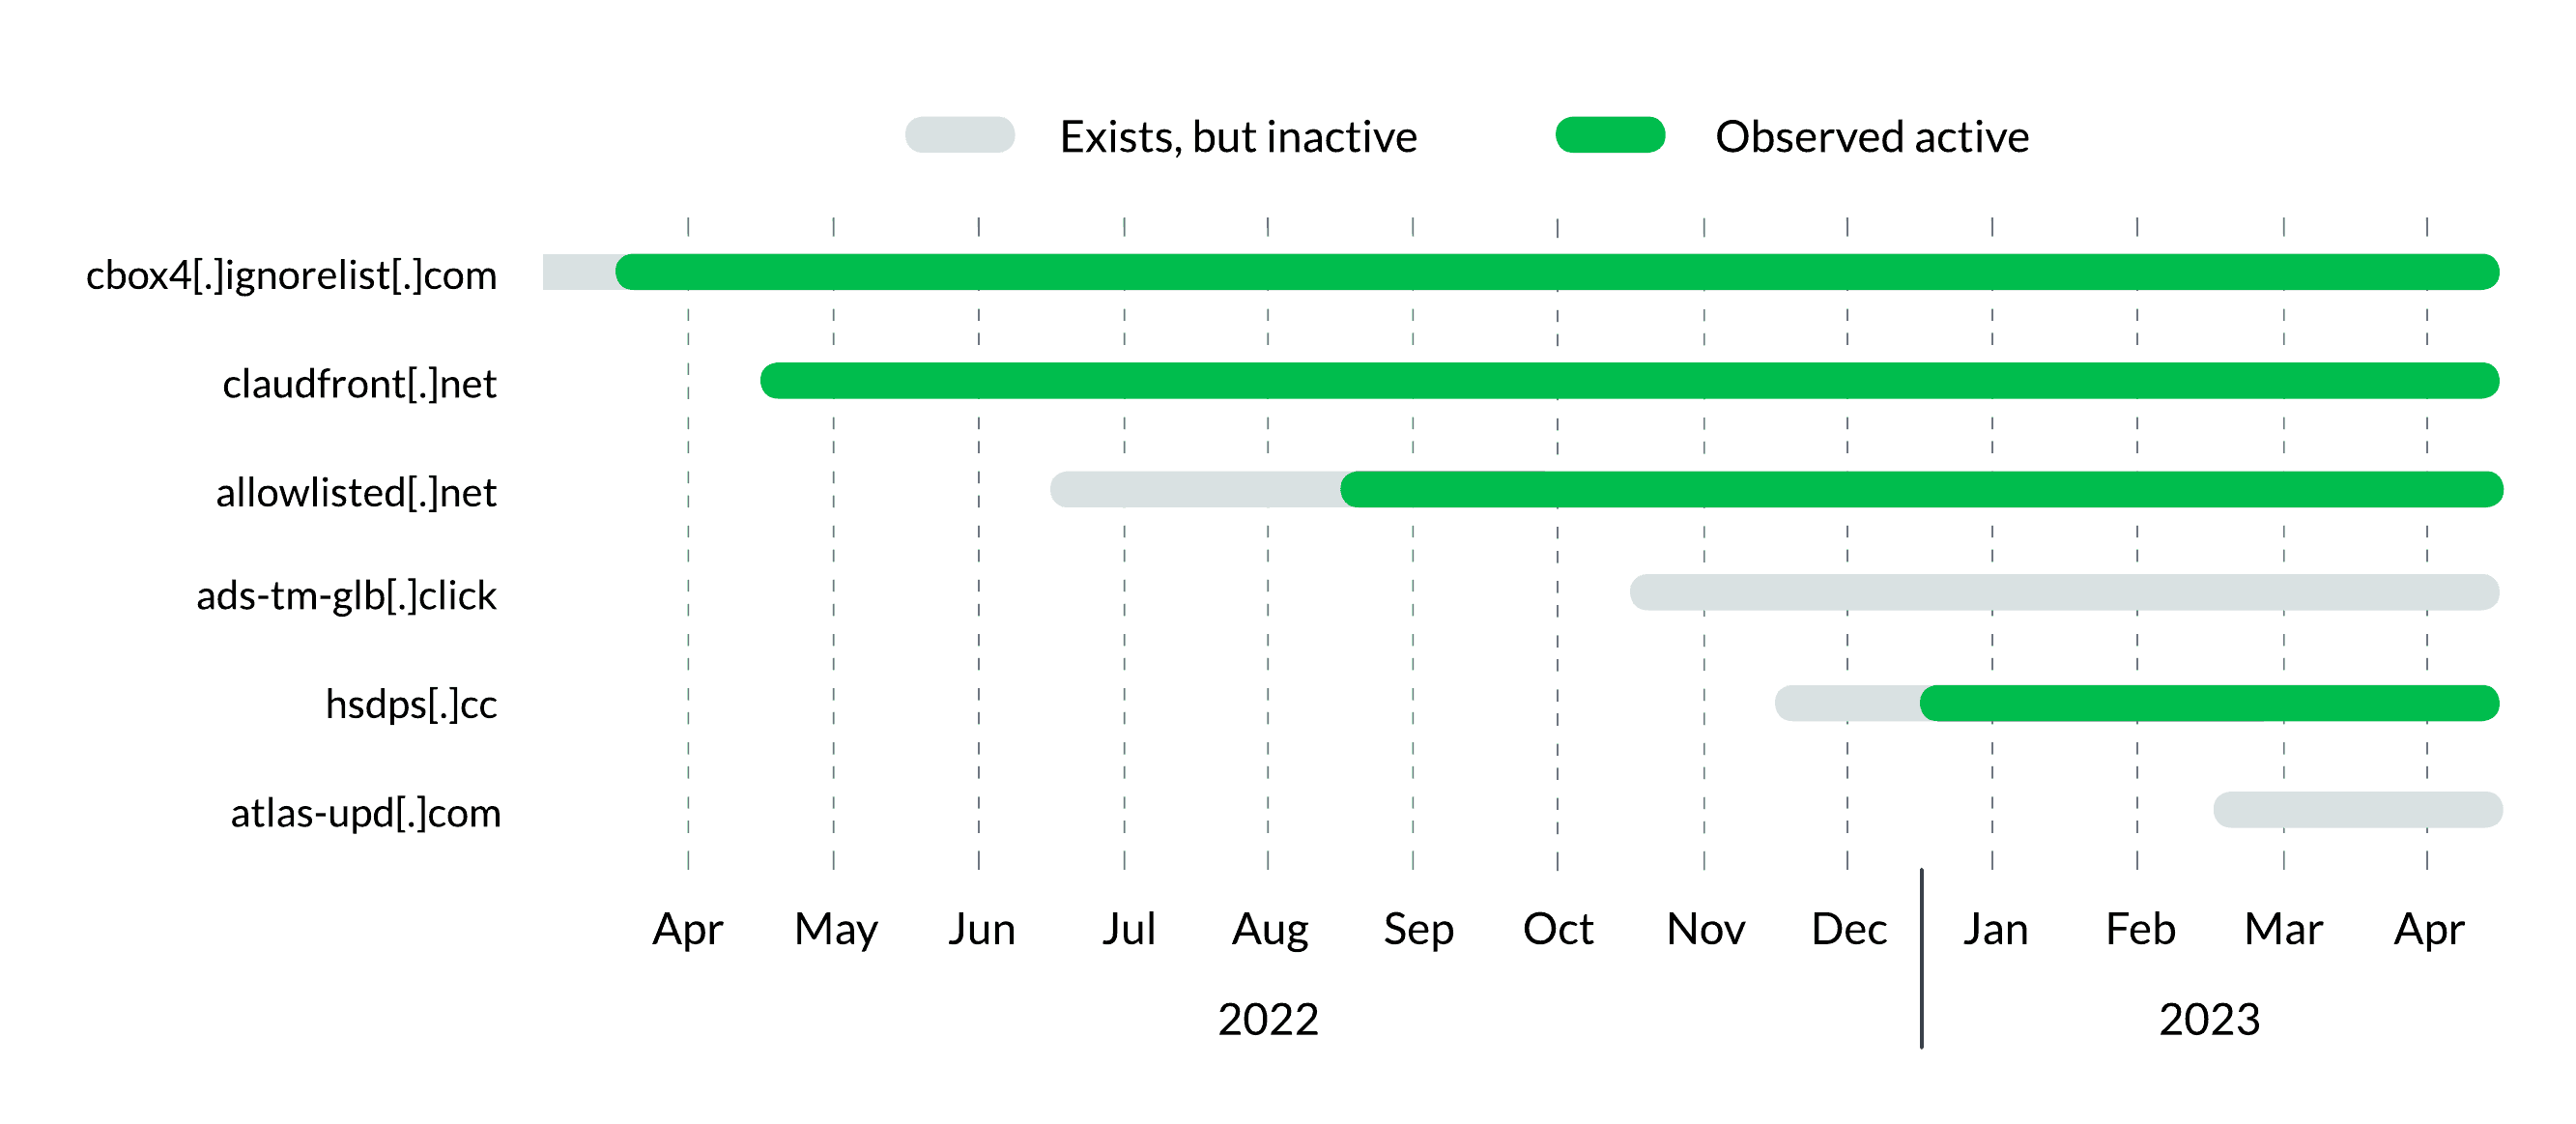
Infoblox researchers discovered a new sophisticated malware toolkit, dubbed Decoy Dog, targeting enterprise networks.
While analyzing billions of DNS records, Infoblox researchers discovered a sophisticated malware toolkit, dubbed Decoy Dog, that was employed in attacks aimed at enterprise networks.
Threat actors behind the malware were observed using known tricks to avoid detection such as registering a domain, but not using it for some time (domain aging technique) and DNS query dribbling.
The Decoy Dog is a cohesive toolkit that implements a number of highly unusual characteristics, which make it easy to identify when examining its domains on a DNS level.
Some of these characteristics are:
- Decoy Dog heavily relies on Pupy. The researchers pointed out that while the malware is open source, deploying it as a DNS C2 requires a significant effort. Its wide array of capabilities was appreciated and used by nation-state actors such as the China-linked APT group Earth Berberoka.
- Decoy Dog uses a unique DNS Signature that matches less than 0.0000027% of the 370 million active domains on the internet. The experts pointed out that this signature is not a feature of standard Pupy installations suggesting that behind the domains there is the same actor.
- DNS Beaconing / Outlier Behavior: Decoy Dog domains exhibit a pattern of periodic, but infrequent, DNS requests that makes them difficult to detect without a preventative DNS solution.
- Shared Hosting / Registration Similarities: The experts were able to group registrations by using registrars, name servers, IPs, and dynamic DNS providers.
- Enterprise Focus: Decoy Dog was only observed targeting enterprise networks.
Infoblox recommends organizations to add the indicators of compromise (IOCs) included in its report to their blocklists manually or via our GitHub repository infobloxopen:threat-intelligence.
“We believe that global security industry collaboration is necessary to understand the full end-to-end story of Decoy Dog and the C2 activity.” concludes the report. “Organizations with protective DNS are able to block these domains immediately, mitigating their risk while they continue to investigate further.”
Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections:
- The Teacher – Most Educational Blog
- The Entertainer – Most Entertaining Blog
- The Tech Whizz – Best Technical Blog
- Best Social Media Account to Follow (@securityaffairs)
Please nominate Security Affairs as your favorite blog.
Nominate here: https://docs.google.com/forms/d/e/1FAIpQLSfaFMkrMlrLhOBsRPKdv56Y4HgC88Bcji4V7OCxCm_OmyPoLw/viewform
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)


