
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Victims of the Gomasom Ransomware can now decrypt their files for free

Fabian Wosar, security researcher at Emsisoft, created a tool for decrypting files locked by the Gomasom Ransomware. Ransomware are the most threatening cyber threats for end-users, but today I have a good news for victims of the Gomasom ransomware, victims can rescue their locked files. The news was spread by the security researcher Fabian Wosar that developed a […]

Victims of the Gomasom Ransomware can now decrypt their files for free

Fabian Wosar, security researcher at Emsisoft, created a tool for decrypting files locked by the Gomasom Ransomware.

Ransomware are the most threatening cyber threats for end-users, but today I have a good news for victims of the Gomasom ransomware, victims can rescue their locked files.

The news was spread by the security researcher Fabian Wosar that developed a tool that could be used by victims to decrypt their file locked by the Gomasom Ransomware.

Gomasom (“GOogle MAil ranSOM“) is a new threat in the criminal ecosystem, it encrypts users’ files, leaving a Gmail address in each file’s name, and adding the .crypt file extension at the end.

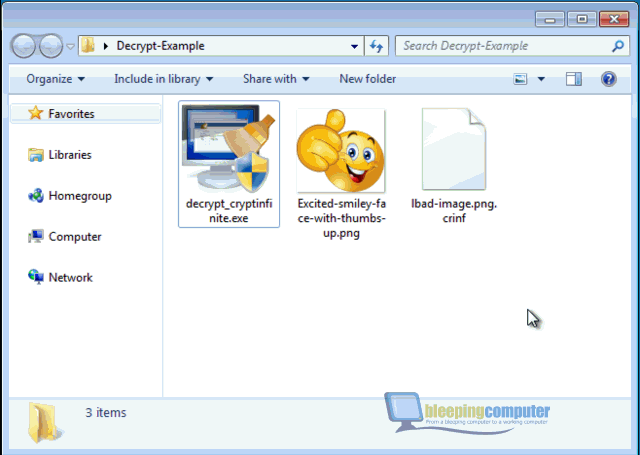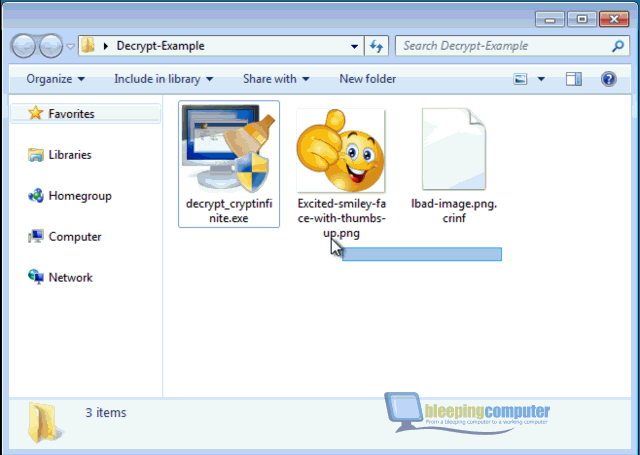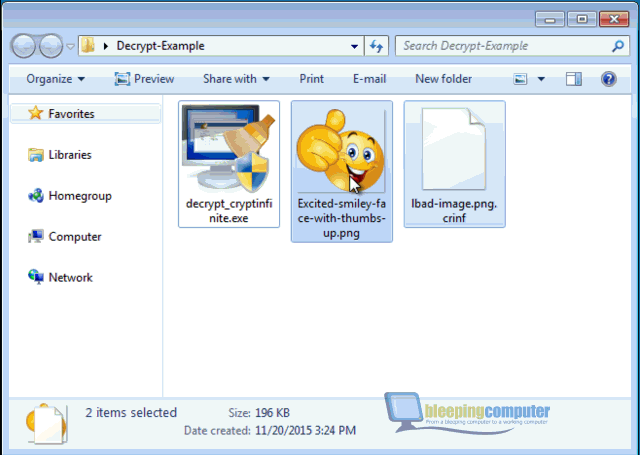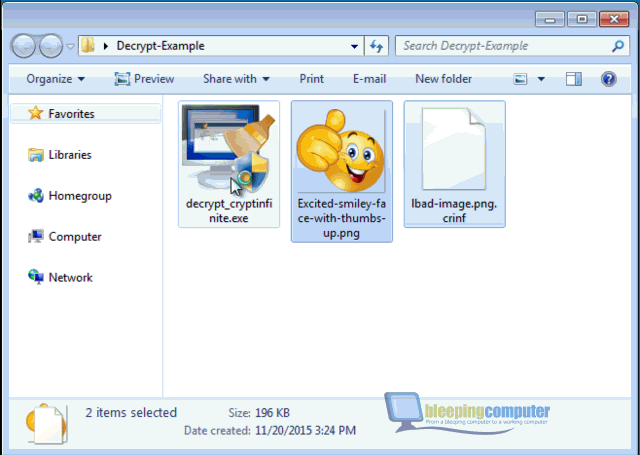
The tool analyzes the encrypted files allows users to get the decryption key and use it to decrypt their files. Wosar explained that the tool has a high success rate when the victim has the ability to analyze both the ransomware-encrypted and original version of a document.

Anyway it is always possible to retrieve the key with the tool because victims can take a PNG file encrypted with the ransomware, and compare it to a random PNG file from the Internet.

The tool to decrypt the file locked by Gomasom ransomware is available on the website of the Emsisoft security firm, meanwhile a user guide is available on the Bleeping Computer forum thread.

Gomasom Ransomware decryption tool

Pierluigi Paganini

(Security Affairs – Gomasom Ransomware, malware)


