
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Eleanor malware uses a Tor backdoor to control Macs

A malicious application named EasyDoc Converter.app delivers a sophisticated malware dubbed Eleanor malware that opens a Tor backdoor on the victim’s machine. Experts from security firm Bitdefender have spotted a new malware, dubbed Eleanor malware (Backdoor.MAC.Eleanor), that once compromised Macs set up a backdoor through Tor network. The malicious application, dubbed EasyDoc Converter.app, pretend to be a […]

Eleanor malware uses a Tor backdoor to control Macs

A malicious application named EasyDoc Converter.app delivers a sophisticated malware dubbed Eleanor malware that opens a Tor backdoor on the victim’s machine.

Experts from security firm Bitdefender have spotted a new malware, dubbed Eleanor malware (Backdoor.MAC.Eleanor), that once compromised Macs set up a backdoor through Tor network.

The malicious application, dubbed EasyDoc Converter.app, pretend to be a file converter, unfortunately, it delivers a sophisticated malware on the victim’s machine. Once infected the target, the malicious code recruits it as part of a botnet or spies on the victim’s machine.

“The backdoor is embedded into a fake file converter application that is accessible online on reputable sites offering Mac applications and software. The EasyDoc Converter.app poses as a drag-and-drop file converter, but has no real functionality – it simply downloads a malicious script.”  said Tiberius Axinte, Technical Leader, Bitdefender Antimalware Lab.

Once infected a Mac, the malware grants full access to the file system as reported by Bitdefender.

“This type of malware is particularly dangerous as it’s hard to detect and offers the attacker full control of the compromised system,” 

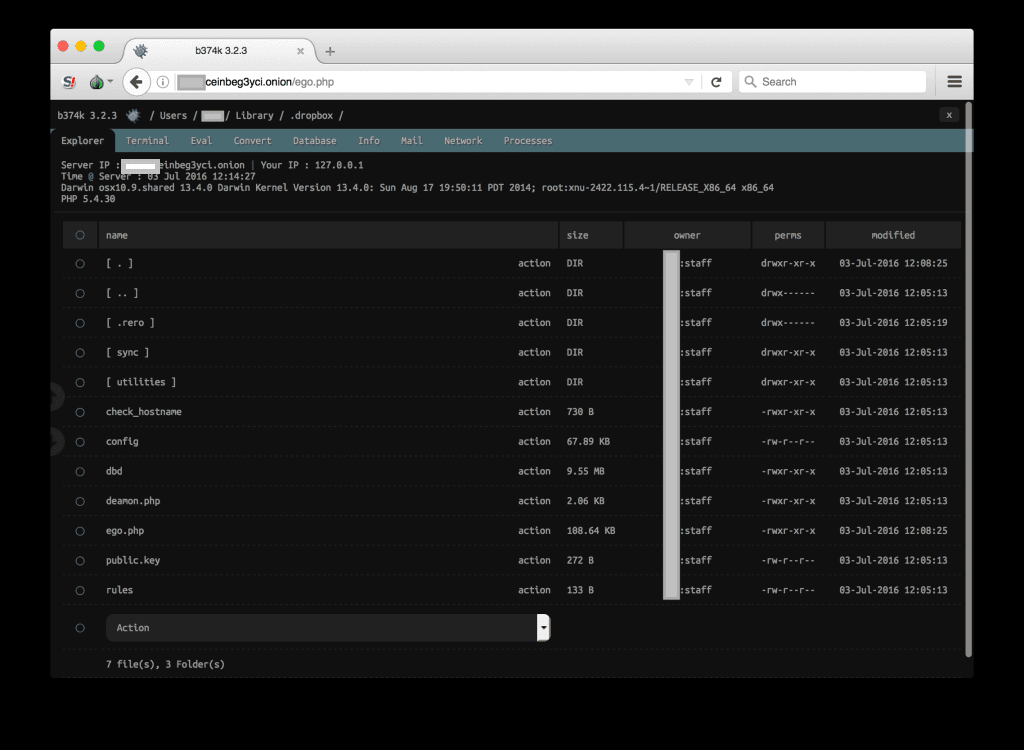
The Backdoor.MAC.Eleanor malware sets up a hidden Tor service and a PHP web server, it exposes a .onion domain that could be accessed by the attacker to control the bot.

Eleanor malware Tor

The Eleanor malware is able to use the camera on the infected machine by using the open-source tool wacaw. The attacker is able to take pictures of the victims and blackmail them.

Every infected Mac is associated with a Tor address, all the addresses are stored on pastebin.com using a PasteBin agent. The addresses are encrypted with a public key using RSA and base64 algorithms.

The malicious app used to deliver the Eleanor malware is not digitally signed by Apple, this means that by downloading applications exclusively from official store and reputable websites.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs –Eleanor malware, backdoor)


