
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Free Tool: Honey Feed

Cybersecurity expert Marco Ramilli shared another tool of his arsenal that extracts suspicious IPs from undesired connections, his HoneyPots. Hi folks, today I’d like to point you out another tool of mine which extracts suspicious IPs from undesired connections. In other words: HoneyPots. I run a personal HoneyPot network which stands from years and over […]

Honeypots 2

HoneyPot Page

Cybersecurity expert Marco Ramilli shared another tool of his arsenal that extracts suspicious IPs from undesired connections, his HoneyPots.

Hi folks, today I’d like to point you out another tool of mine which extracts suspicious IPs from undesired connections. In other words: HoneyPots. I run a personal HoneyPot network which stands from years and over time it harvested numerous IP addresses which could be, potentially, malicious (typically scanners). If you like having fresh HoneyPot feeds in your OSINT collection, please feel free to download them directly HERE. The downloaded file wraps malicious (as intended by HoneyPots) IPs and the “last seen” date so which you might decide if the IP is getting too old for blocking purposes. The file is structured as an array of JSON object in order to facilitate the ingestion in every feeder or database. The following image shows what I meant

Honeypots
Json Representation

The feed is update every 24h, so it would be useless to make multiple downloads per day. The entire system detect approximately 140k events per day.

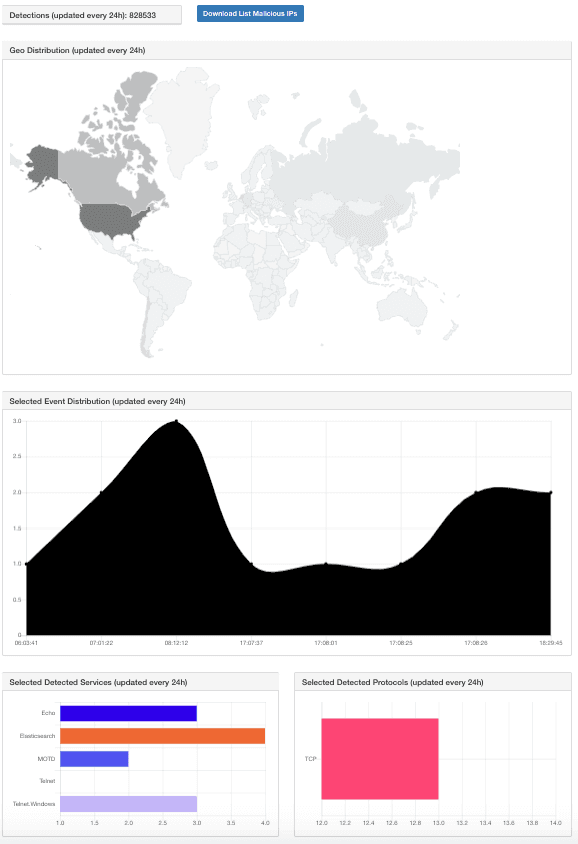
Following a set of interesting and very selective graphic views are presented. Geographic distribution is shown in order to have a quick overview of which country is hitting mostly my HoneyPot network, a nice event wave shows the time of the most relevant hits while selected protocols and services graph shows the most interesting hit selected protocols.

Honeypots 2
HoneyPot Page

Hope you might appreciate my intent to share with cybersecurity community free data in order to improve our digital space. Have fun and if you have questions or suggestion please feel free to contact me.

Early February, Marco Ramilli released for free the Malware Hunter tool a simple but interesting catching tool based on static YARA rules.

https://marcoramilli.com/2019/02/06/free-tool-malware-hunter/

About the author: Marco Ramilli, Founder of Yoroi

I am a computer security scientist with an intensive hacking background. I do have a MD in computer engineering and a PhD on computer security from University of Bologna. During my PhD program I worked for US Government (@ National Institute of Standards and Technology, Security Division) where I did intensive researches in Malware evasion techniques and penetration testing of electronic voting systems.

I do have experience in security testing since I have been performing penetration testing on several US electronic voting systems. I’ve also been encharged of testing uVote voting system from the Italian Minister of homeland security. I met Palantir Technologies where I was introduced to the Intelligence Ecosystem. I decided to amplify my cybersecurity experiences by diving into SCADA security issues with some of the biggest industrial aglomerates in Italy. I finally decided to found Yoroi: an innovative Managed Cyber Security Service Provider developing some of the most amazing cybersecurity defence center I’ve ever experienced! Now I technically lead Yoroi defending our customers strongly believing in: Defence Belongs To Humans

[adrotate banner=”9″][adrotate banner=”12″]

Edited by Pierluigi Paganini

(Security Affairs – HoneyPots, Honey Feed)

[adrotate banner=”5″]

[adrotate banner=”13″]


