
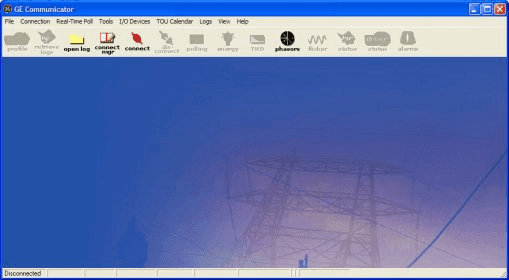
ICS-CERT is warning of several vulnerabilities in the GE Communicator software, including hardcoded credentials and privilege escalation bugs.
ICS-CERT is warning of five flaws affecting the GE Communicator software, including privilege escalation issues and
GE Communicator is a is a user-friendly software for programming and monitoring supported metering devices. The software allows users to program the meters, view real-time metered data, and analyze collected data.
The application is used by organizations worldwide, including electric utilities and large manufacturers.
The flaws could be exploited by an attacker to gain admin rights to a workstation running the GE Communicator software. Experts pointed out that in order to exploit the issues the attackers need either network access to the workstation or local logon access to the workstation with regular user privileges.
“Successful exploitation of these vulnerabilities could allow an attacker to gain administrative privileges, manipulate widgets and UI elements, gain control over the database, or execute administrative commands.” reads the advisory published by the ICS-CERT.

The most severe flaw, tracked as CVE-2019-6548, is related to the use of hard-coded credentials CWE-798 (CVSS v3 base score of 8.1).
“Two backdoor accounts with hardcoded credentials exist, which may allow control over the database. This service is inaccessible to attackers if Windows default firewall settings are used by the end user.” reads the advisory. “CVE-2019-6548 has been assigned to this vulnerability.”
ICS-CERT also report two uncontrolled search path vulnerabilities:
- uncontrolled search path CWE-427 (CVE-2019-6564) that could be exploited by an attacker with non-administrative rights to place malicious files within the installer file directory to gain administrative privileges on a system during installation or upgrade.
-
uncontrolled search path CWE-427 (CVE-2019-6546) that could be exploited by an attacker to place malicious files within the working directory of the program, which may allow an attacker to manipulate widgets and UI elements.
The remaining issues are improper access controls
The following Communicator components, all versions prior to 4.0.517, are affected:
- Communicator Installer
- Communicator Application
- Communicator PostGreSQL
- Communicator MeterManager
- Communicator WISE Uninstaller
GE addressed the vulnerabilities with the release of GE Communicator 4.0.517.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(
[adrotate banner=”5″]
[adrotate banner=”13″]


