
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Caution, Hackers targeted the cPanel Database

The cPanel Inc. company that manages the popular web hosting account management tool is warning customers about a possible data breach occurred over the weekend. According to the cPanel firm customers’ account information may have been compromised, hackers tried to access a database containing users’ data, including names, salted passwords, and contact information. cPanel Inc. added that […]

Caution, Hackers targeted the cPanel Database

The cPanel Inc. company that manages the popular web hosting account management tool is warning customers about a possible data breach occurred over the weekend.

According to the cPanel firm customers’ account information may have been compromised, hackers tried to access a database containing users’ data, including names, salted passwords, and contact information. cPanel Inc. added that financial have not been accessed because are stored on a different server. The company said it interrupted the breach, but the hackers might have still gained access to the details of cPanel Store and Manage2 users.

“I am writing to let you know that one of our user databases may have been breached. Although we successfully interrupted the breach, it is still possible that user contact information may have been susceptible.” states the official cPanel’s statement.

“The customer contact information that may have been susceptible is limited to names, contact information, and encrypted (and salted) passwords. Please note that our credit card information is stored in a separate system designed for credit card storage and is not impacted by this possible breach.”

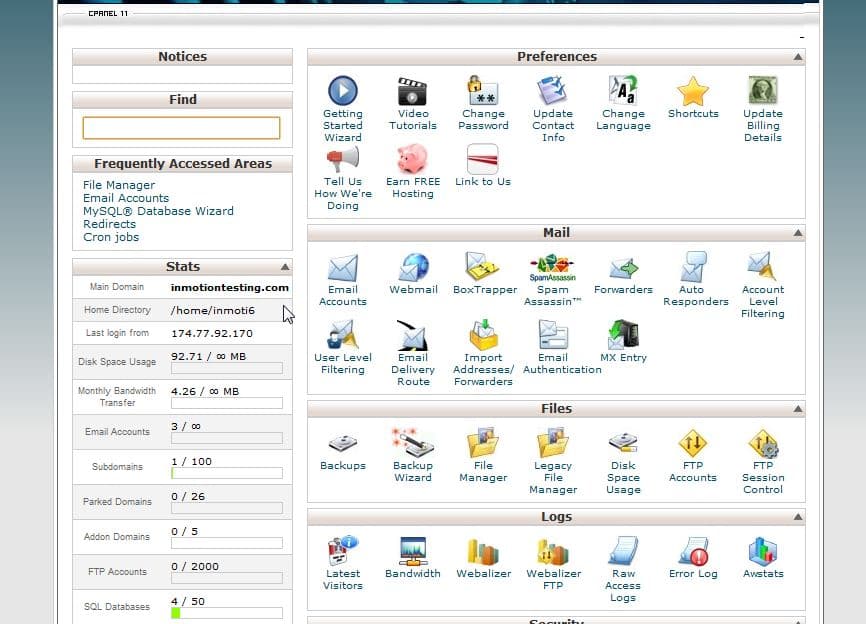
cpanel stats

The company announced the adoption of further measures to protect its systems and customers, it will force a password reset to limit the impact of the alleged security breach.

“Although current passwords are stored salted and encrypted, we are accelerating our move to stronger password encryption at the same time in order to minimize disruption. In order to safeguard the system, we will force all users with older password encryption to change their passwords,” says Aaron Stone, director of internal development at cPanel.

A couple of weeks ago, cPanel released new builds that fix dozen vulnerabilities in both cPanel & WebHost Manager versions, some of the flaws are critical and could be exploited by hackers to execute arbitrary code.

“It is important to highlight that this incident was not related to cPanel products or the Targeted Security Release published on January 18th.”

cPanel urges customers to change passwords provided to cPanel tech support via the ticket system.

Pierluigi Paganini

(Security Affairs – cPanel, hacking)


