Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

LockBit ransomware gang claims the hack of Continental automotive group

The LockBit ransomware group claimed to have hacked the multinational automotive group Continental and threatens to leak stolen data. LockBit ransomware gang announced to have hacked the German multinational automotive parts manufacturing company Continental. The group added the name of the company to its Tor leak site and is threatening to publish alleged stolen data if the […]

Lockbit 2.0 ransomware Continental

The LockBit ransomware group claimed to have hacked the multinational automotive group Continental and threatens to leak stolen data.

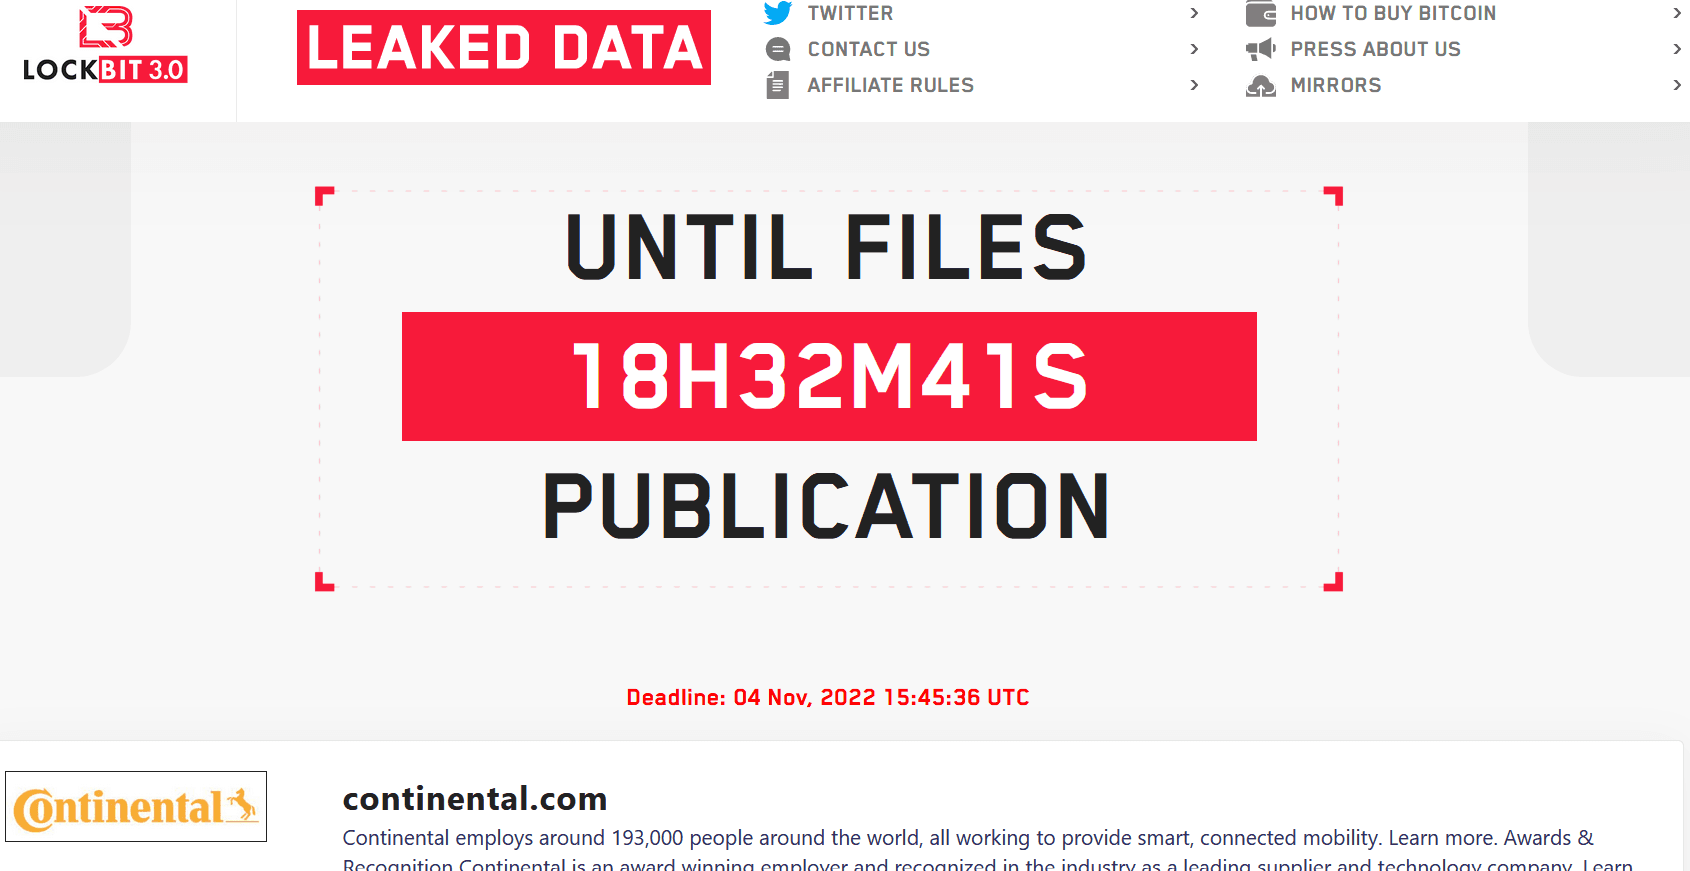
LockBit ransomware gang announced to have hacked the German multinational automotive parts manufacturing company Continental. The group added the name of the company to its Tor leak site and is threatening to publish alleged stolen data if the victim will not pay the ransom.

The cybercriminals have fixed the deadline on November 4, 2022, at 15:45:36 UTC. At this time the group announced that it will publish all available data, a circumstance that suggests the victim has yet to negotiate with the criminals or it has refused to pay the ransom.

Lockbit 2.0 ransomware Continental

At this time, it is not clear if the Lockbit 3.0 ransomware group is responsible for the attack that Continental disclosed on August 24, 2022.

“In a cyberattack, attackers infiltrated parts of Continental’s IT systems. The company detected the attack in early August and then averted it. Continental’s business activities have not been affected at any point. The technology company maintains full control over its IT systems. According to current information, the IT systems of third parties have not been affected.” reads the statement published by the company in August. “Immediately after the attack was discovered, Continental took all necessary defensive measures to restore the full integrity of its IT systems.”

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Lockbit)

[adrotate banner=”5″]

[adrotate banner=”13″]