
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Kaspersky warns of a new Loki Bot campaign target corporate mailboxes

Security experts from Kaspersky Lab have uncovered a new spam campaign leveraging the Loki Bot malware to target corporate mailboxes. The Loki Bot attacks started in July and aimed at stealing passwords from browsers, messaging applications, mail and FTP clients, and cryptocurrency wallets Loki Bot operators employ various social engineering technique to trick victims into opening weaponized attachments that […]

Loki Bot

Security experts from Kaspersky Lab have uncovered a new spam campaign leveraging the Loki Bot malware to target corporate mailboxes.

The Loki Bot attacks started in July and aimed at stealing passwords from browsers, messaging applications, mail and FTP clients, and cryptocurrency wallets

Loki Bot operators employ various social engineering technique to trick victims into opening weaponized attachments that would deploy the Loki Bot stealer.

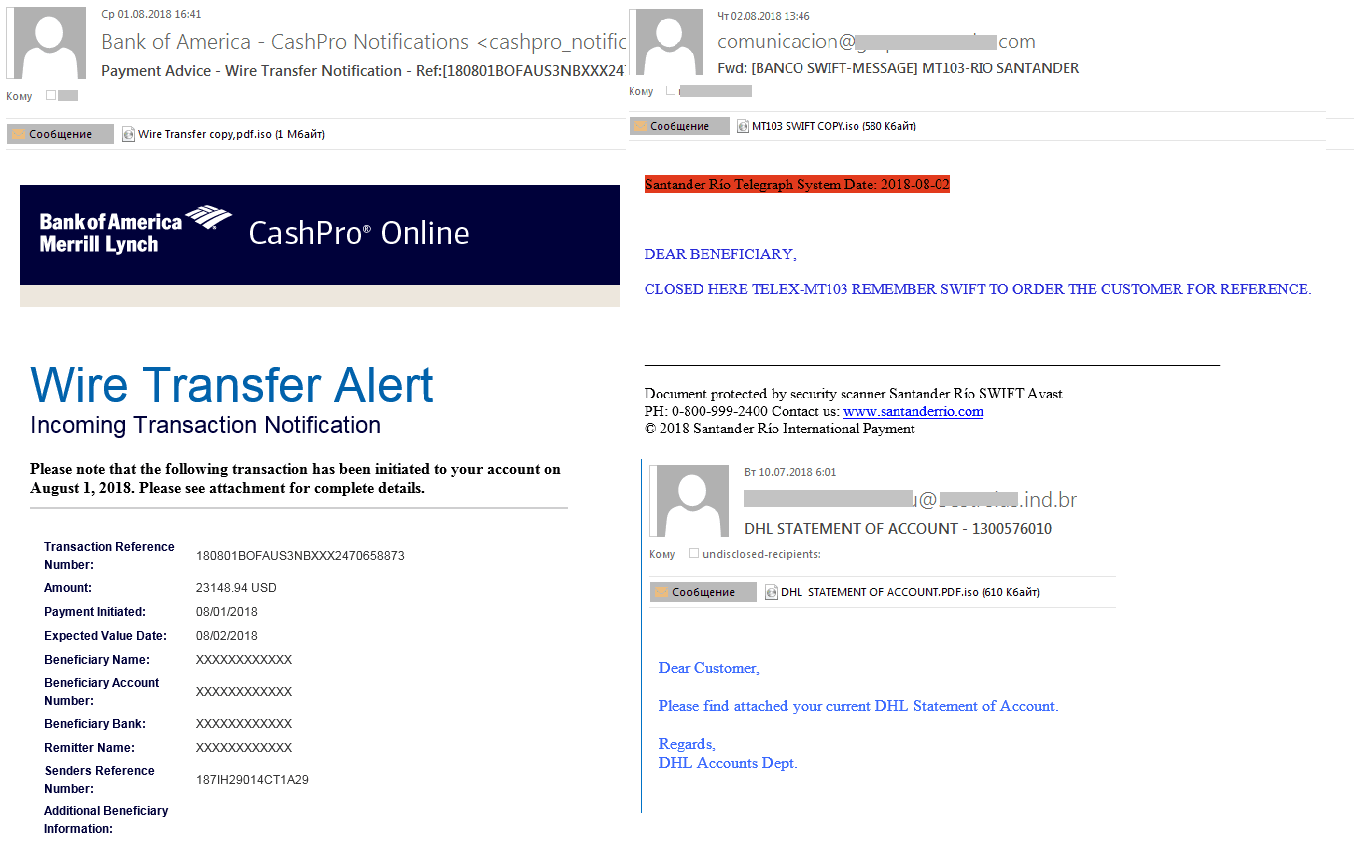
The messages use attachments with .iso extensions, a type of file that worked as a container for delivering malware.

“Starting from early July, we have seen malicious spam activity that has targeted corporate mailboxes. The messages discovered so far contain an attachment with an .iso extension that Kaspersky Lab solutions detect as Loki Bot.” reads the analysis published by Kaspersky.

“The malware’s key objective is to steal passwords from browsers, messaging applications, mail and FTP clients, and cryptocurrency wallets. Loki Bot dispatches all its loot to the malware owners.”

The messages masquerade as notifications from other companies, or as orders and offers.

Threat actors are sending out copies of Loki Bot to company email addresses that were available on public sources or from the companies’ own websites.

Loki Bot

Experts observed different spam messages including fake notifications from well-known companies, fake notifications containing financial documents, and fake orders or offers.

Researchers highlighted the importance for organizations of adopting security measures that include both technical protections and training for employees.

“Every year we observe an increase in spam attacks on the corporate sector.” Kaspersky concludes.

“The perpetrators have used phishing and malicious spam, including forged business emails, in their pursuit of confidential corporate information: intellectual property, authentication data, databases, bank accounts, etc.” 

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Loki Bot, malware)

[adrotate banner=”5″]

[adrotate banner=”13″]


