
Security Affairs
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches|One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers|U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog|White House Network Appears in Global Residential Proxy Traffic|OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries|ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe|OpenAI Reports Covert Underperformance in GPT-6 Astra|UNM Health Shuts Clinics and Diverts Patients During Security Incident|Russian APT29 Targets Mobile Users with Watering Hole Attacks|U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Malware controlled through commands hidden in memes posted on Twitter

New Malware Takes Commands From Memes Posted On Twitter Security researchers at Trend Micro have spotted a new strain of malware that retrieved commands from memes posted on a Twitter account controlled by the attackers. In this way, attackers make it hard to detect traffic associated with the malware that is this case appears as legitimate […]

twitter memes malware

New Malware Takes Commands From Memes Posted On Twitter

Security researchers at Trend Micro have spotted a new strain of malware that retrieved commands from memes posted on a Twitter account controlled by the attackers. In this way, attackers make it hard to detect traffic associated with the malware that is this case appears as legitimate Twitter traffic.

The use of legitimate web services to control malware is not a novelty, it the past crooks used legitimate services like Gmail, DropBox, PasteBin, and also Twitter to control malicious codes.

The malware discovered by Trend Micro leverages on the steganography to hide the commands embedded in a meme posted on Twitter. 

“This new threat (detected as TROJAN.MSIL.BERBOMTHUM.AA) is notable because the malware’s commands are received via a legitimate service (which is also a popular social networking platform), employs the use of benign-looking yet malicious memes, and it cannot be taken down unless the malicious Twitter account is disabled.” reads the post published by Trend Micro.

“Twitter has already taken the account offline as of December 13, 2018.”

Attackers hid the “/print” command in the memes, it allows them to take screenshots of the infected machine and send them back to a C&C server whose address is obtained through a hard-coded URL on pastebin.com.

The BERBOMTHUM malware checks the Twitter account used by the attackers, downloads and scans meme files, and extracts the command they include.

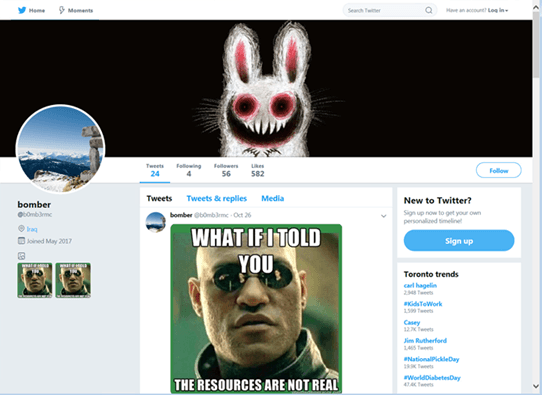
The Twitter account used by miscreants was created in 2017 and contained only two memes posted on October 25 and 26. The images were used to deliver the “/print” commands to the malware.

twitter memes malware

Below the list of commands supported by the malware:

CommandsDescription
/printScreen capture
/processosRetrieve list of running processes
/clipCapture clipboard content
/usernameRetrieve username from infected machine
/docsRetrieve filenames from a predefined path such as (desktop, %AppData% etc.)

According to Trend Micro, the malware is in the early stages of its development, experts noticed that the Pastebin link points to a local, 

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs –malware, memes)

[adrotate banner=”5″] [adrotate banner=”13″]


