
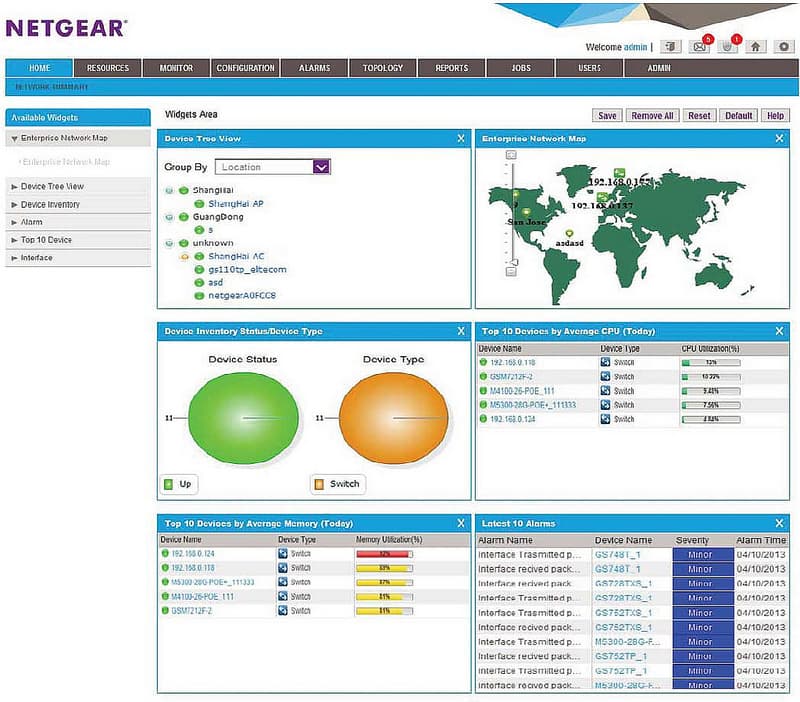
A security researcher has released the exploit code for two serious vulnerabilities in the Netgear ProSAFE NMS300 network management system.
Do you have a Netgear ProSAFE NMS300 Management System? Now you have a reason to worry because the security researcher Pedro Ribeiro has discovered two serious vulnerabilities in the network device.
The Netgear ProSAFE NMS300 Management System allows administrators to monitor and manage their networks by using a user friendly web-based interface.
The device is affected by a vulnerability (Unrestricted Upload of File with Dangerous Type), coded CVE-2016-1524, that could be exploited by a remote, unauthenticated attacker to upload an arbitrary file to the system.
Once uploaded a file, it will be available in the server’s root directory at the following URL:
http://<IP>:8080/null<filename>
and it could be executed with SYSTEM privileges.
The remote code execution vulnerability received a CVSS score of 8.3, it can be exploited by sending a specially crafted POST request to one of two Java servlets present in default NMS300 installations.
“By sending a specially crafted POST request to the servlets, an attacker can upload arbitrary files that will then be accessible from the NMS300 server’s root directory as http://<IP>:8080/null<filename>. The NMS300 server runs with SYSTEM privileges.” states the advisory issued CERT Coordination Center at Carnegie Mellon University .

The second flaw (Improper Limitation of a Pathname to a Restricted Directory (‘Path Traversal’) ), coded CVE-2016-1525, discovered in the Netgear ProSAFE NMS300 is a directory traversal that could be exploited by an authenticated attacker to download any file from the device.
“An authenticated attacker can manipulate the realName parameter of a crafted POST request sent to http://<IP>:8080/data/config/image.do?method=add to load an arbitrary local file from the server host to a predictable location in the web service. The file can then be downloaded from http://<IP>:8080/data/config/image.do?method=export&imageId=<ID>, where <ID> is a count that increments by one every time a file is uploaded in this manner.” continues the advisory.
The security experts Ribeiro reported the flaws to Netgear via CERT/CC in December, but the issues are still present in the systems.
Riberio also published a proof-of-concept-code for the exploitation of the flaws, they are two Metasploit modules available for the download.
Waiting for a fix, let me suggest you to isolate the web management interface of your device from the Internet.
(Security Affairs – Netgear ProSAFE NMS300 Management System, hacking)


